Posts
4648Following
742Followers
1662
 repeated
Rebane
rebane2001@infosec.exchange
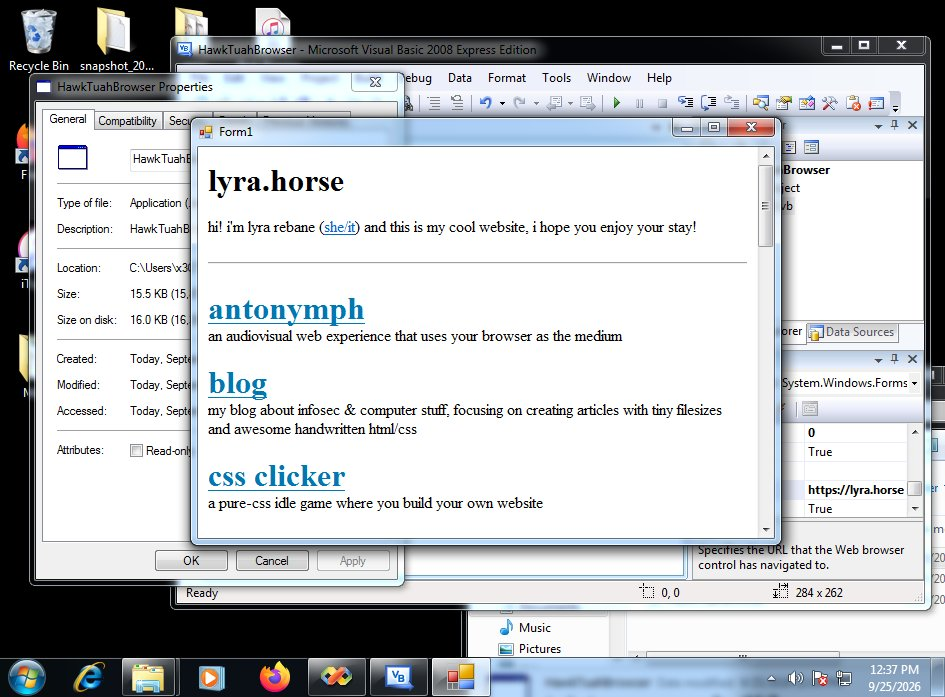
Introducing 𝙷𝚊𝚠𝚔𝚃𝚞𝚊𝚑𝙱𝚛𝚘𝚠𝚜𝚎𝚛.𝚎𝚡𝚎
- 15 KB native web browser
- 6 MB of RAM for the host
- 0 lines of Visual Basic (no C# cuz idk how to write it)
- no URL bar because surfing through 88x31s is more fun
- title bar kept cuz then u can close it and minimize buttons
 3
3
 0
buherator
buherator"Local Network Access permission required: top-level site “https://infosec.place/”, initiator “https://infosec.place/”, attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
I could reproduce it by scrolling a shit ton in my timeline (won't do again), but I think a minimal test case would be a simple `img src="http://localhost...` served from a non-local origin.
In that case though the source would be there in Inspector, but in case of Akkoma infinite scroll does some magic that prevents me from simply looking up the tag by URL, that's why I'm thinking if some kind of "stack trace" is available for network events that would lead me to the offending element?
1
0
0
buherator
buherator
1
0
0
buherator
buheratorWhen booking for events it *always* takes *days* to get from registering for an event and getting there to show your QR or whatever. And while an attacker who hijacks your session has 0 benefit from accessing it for a prolonged time, somehow #security finds it crucial that users are auto logged-out after 30mins.
It would take just a *tiny* bit of thinking to avoid making things worse for everyone.
[1] https://wstg.owasp.org/latest/4-Web_Application_Security_Testing/06-Session_Management/07-Session_Timeout/ (congrats to #OWASP for breaking all your indexed links in search engines, also very helpful!)
0
1
2
repeated
Kevin Beaumont
GossiTheDog@cyberplace.socialBBC News has 4 YouTube videos up in the past day about OpenAI hacking “governments”, with approaching a million views.
If you want to know the technical details of this elite frontier AI hacking - these are examples of the actual OpenAI agent requests.
It’s really dumb shit. The story here is OpenAI are utterly incompetent at cybersecurity, as are their victims.
 5
5
0
buherator
buherator#Firefox
RE: https://infosec.place/objects/c55e1bcb-86a9-4d16-b9fb-83dccaeb4dad
2
2
4
repeated
 repeated
David Revoy
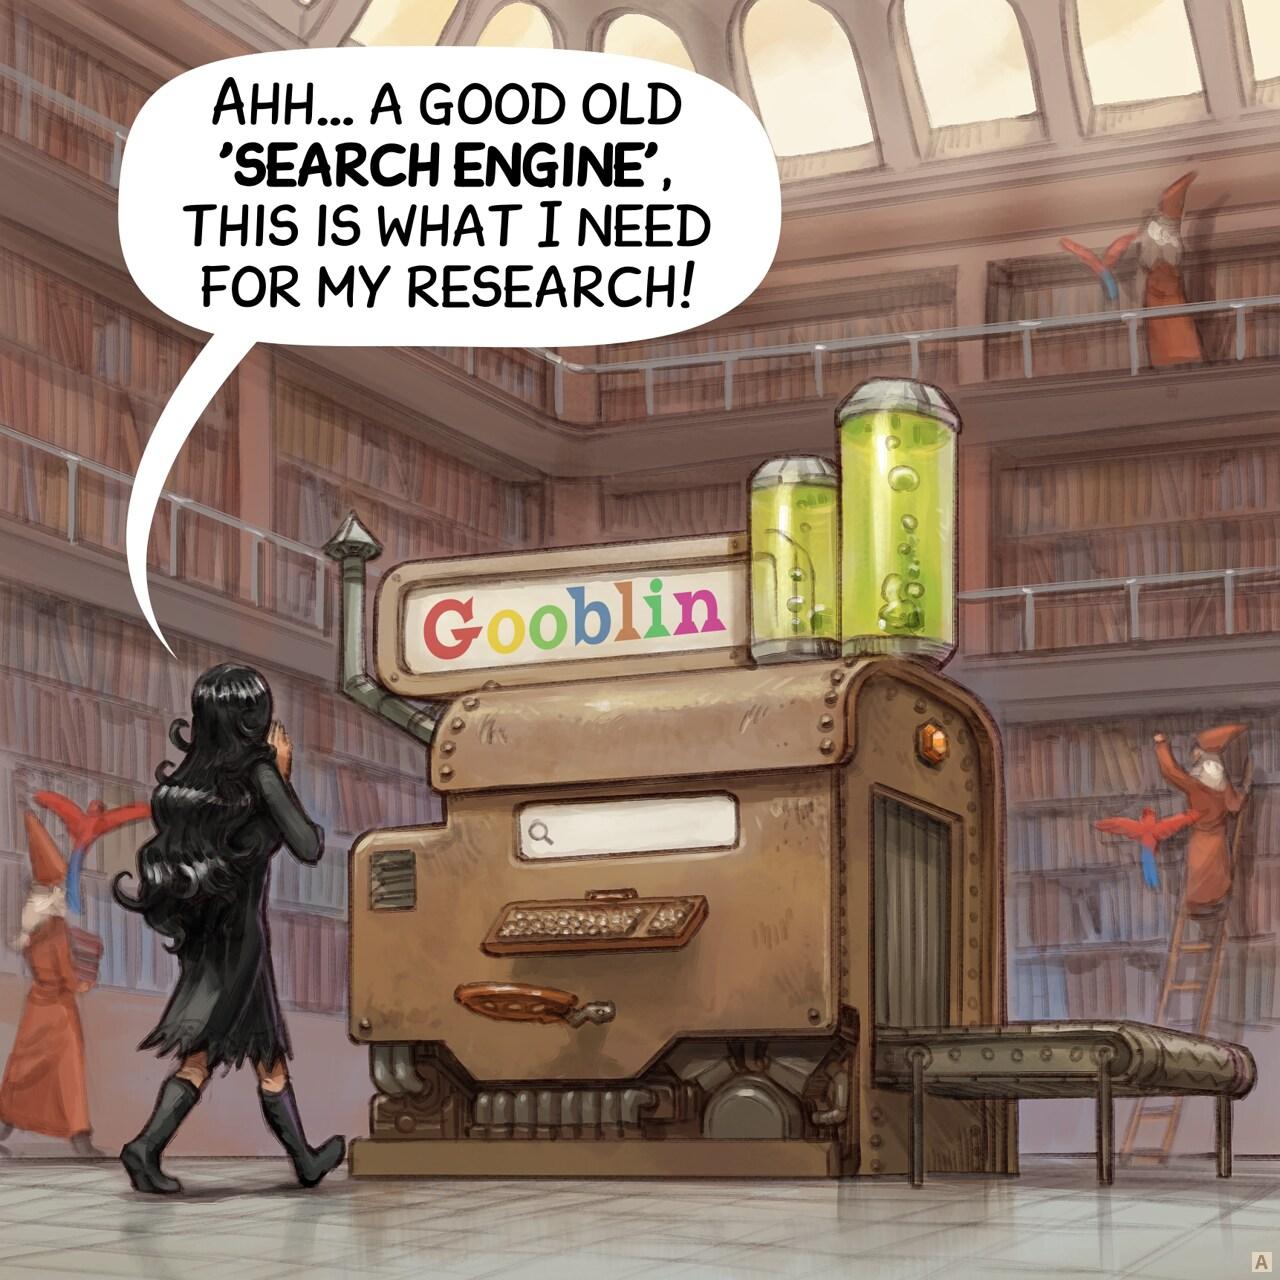
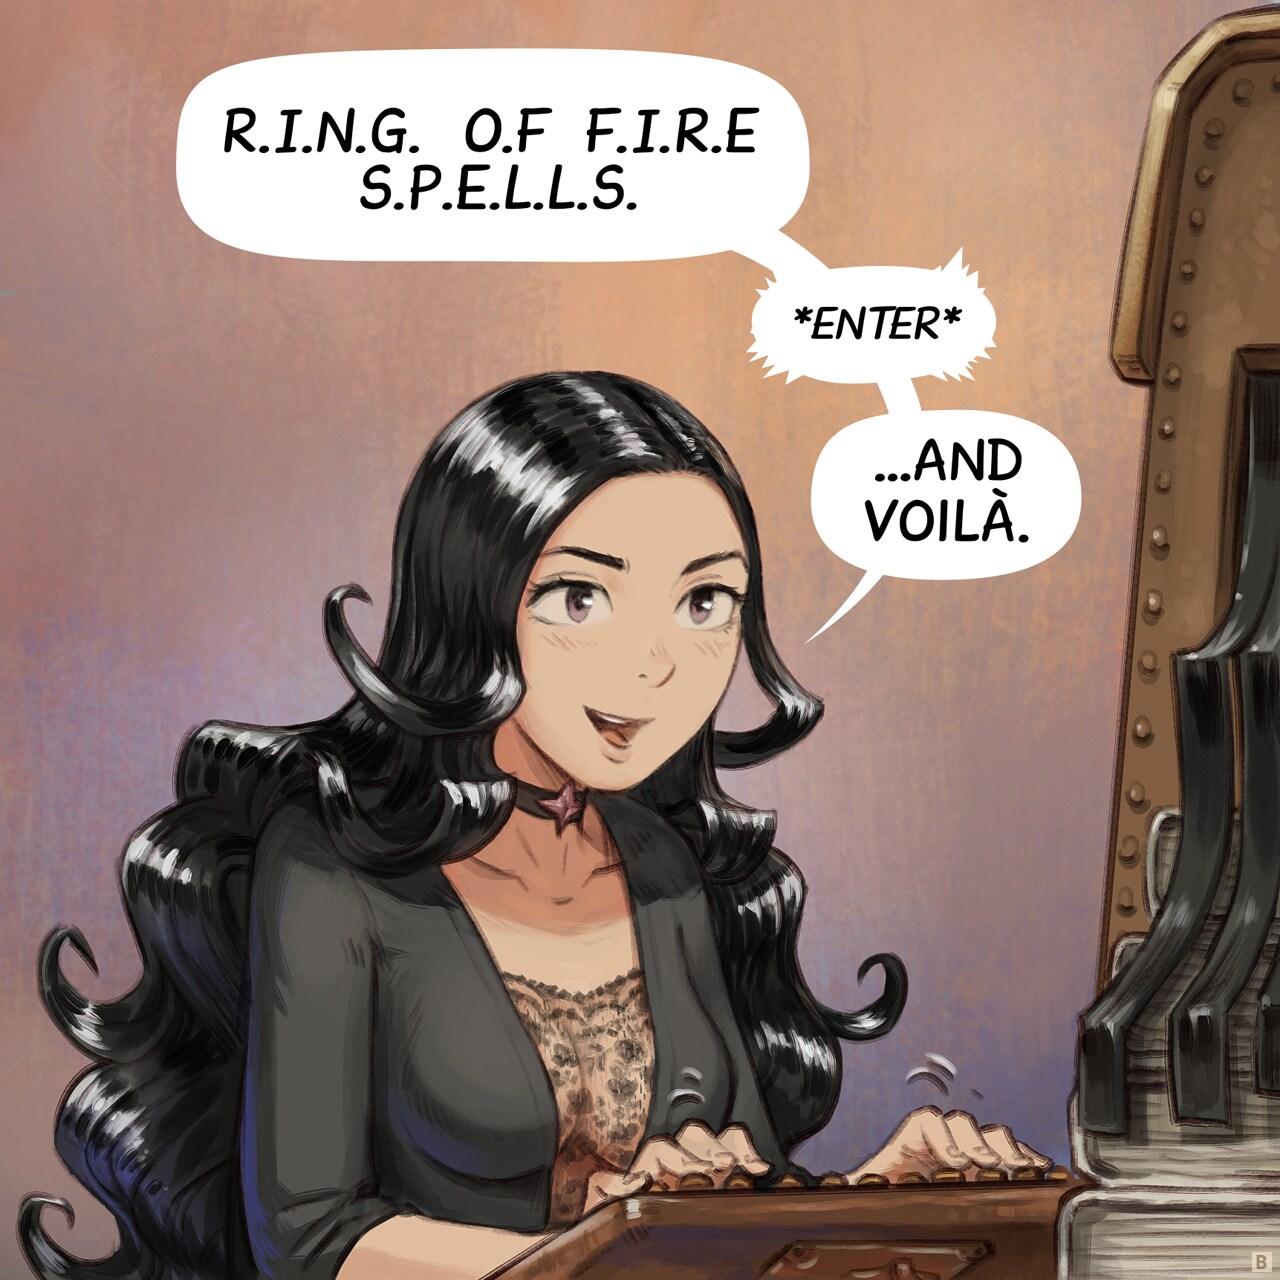
davidrevoy@framapiaf.orgThe Degraded Search Engine
Bonus speedpaint: https://www.peppercarrot.com/en/miniFantasyTheater/071.html#bonus
#webcomic #krita #miniFantasyTheater
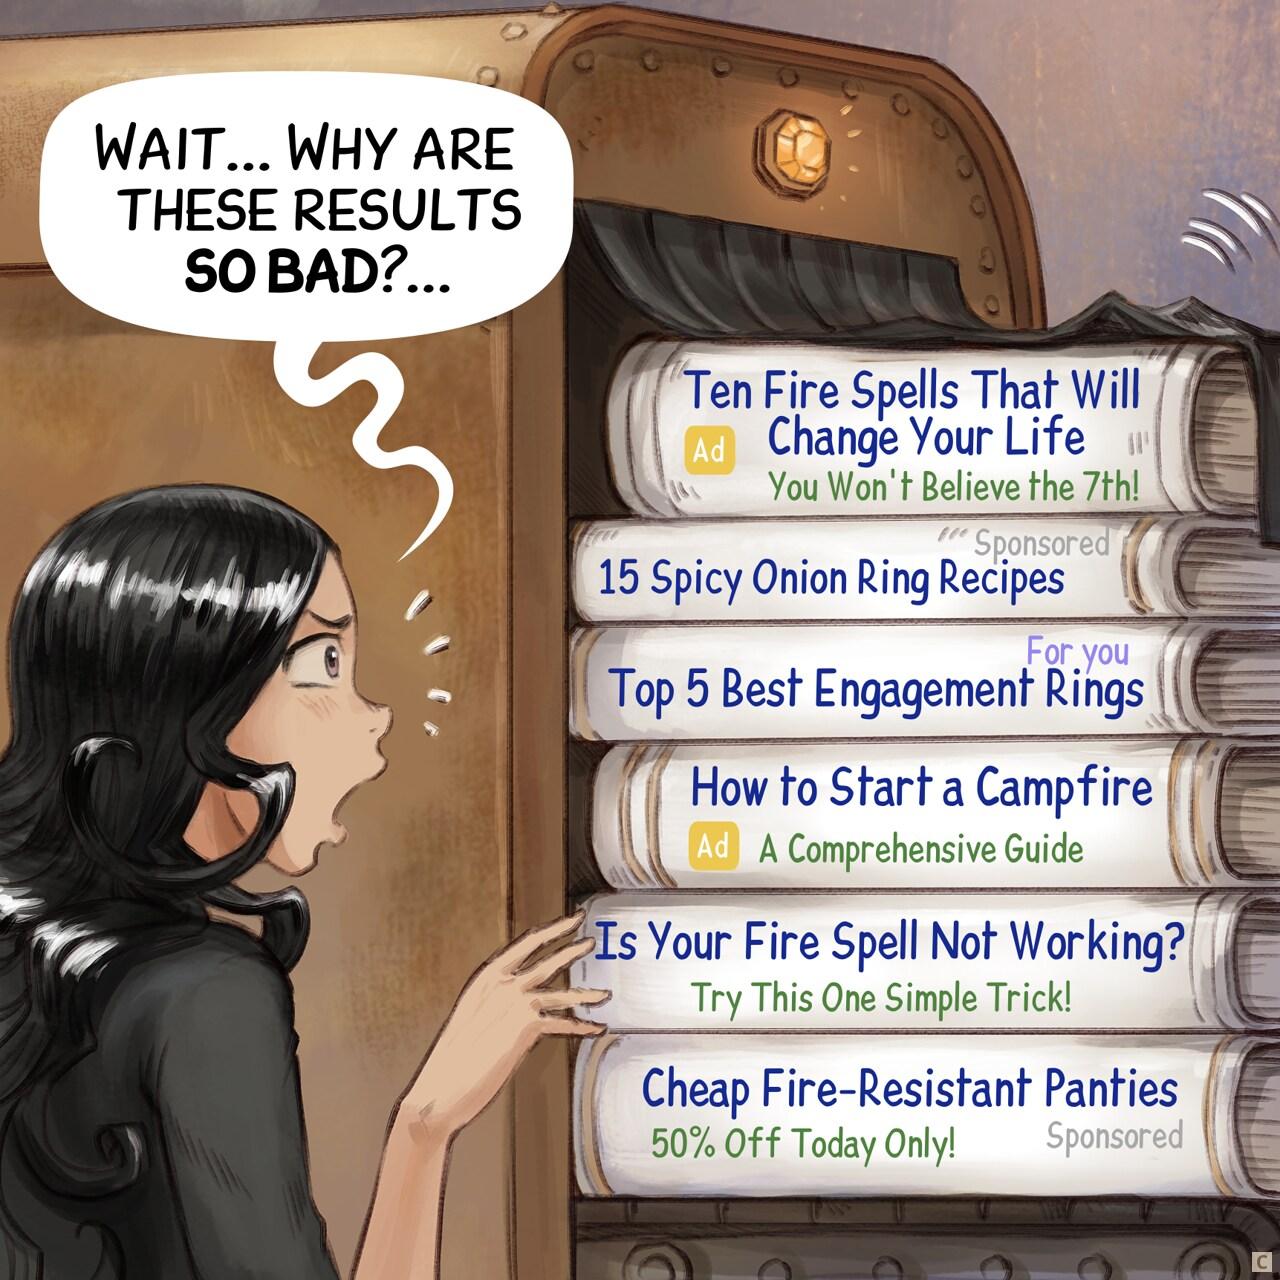
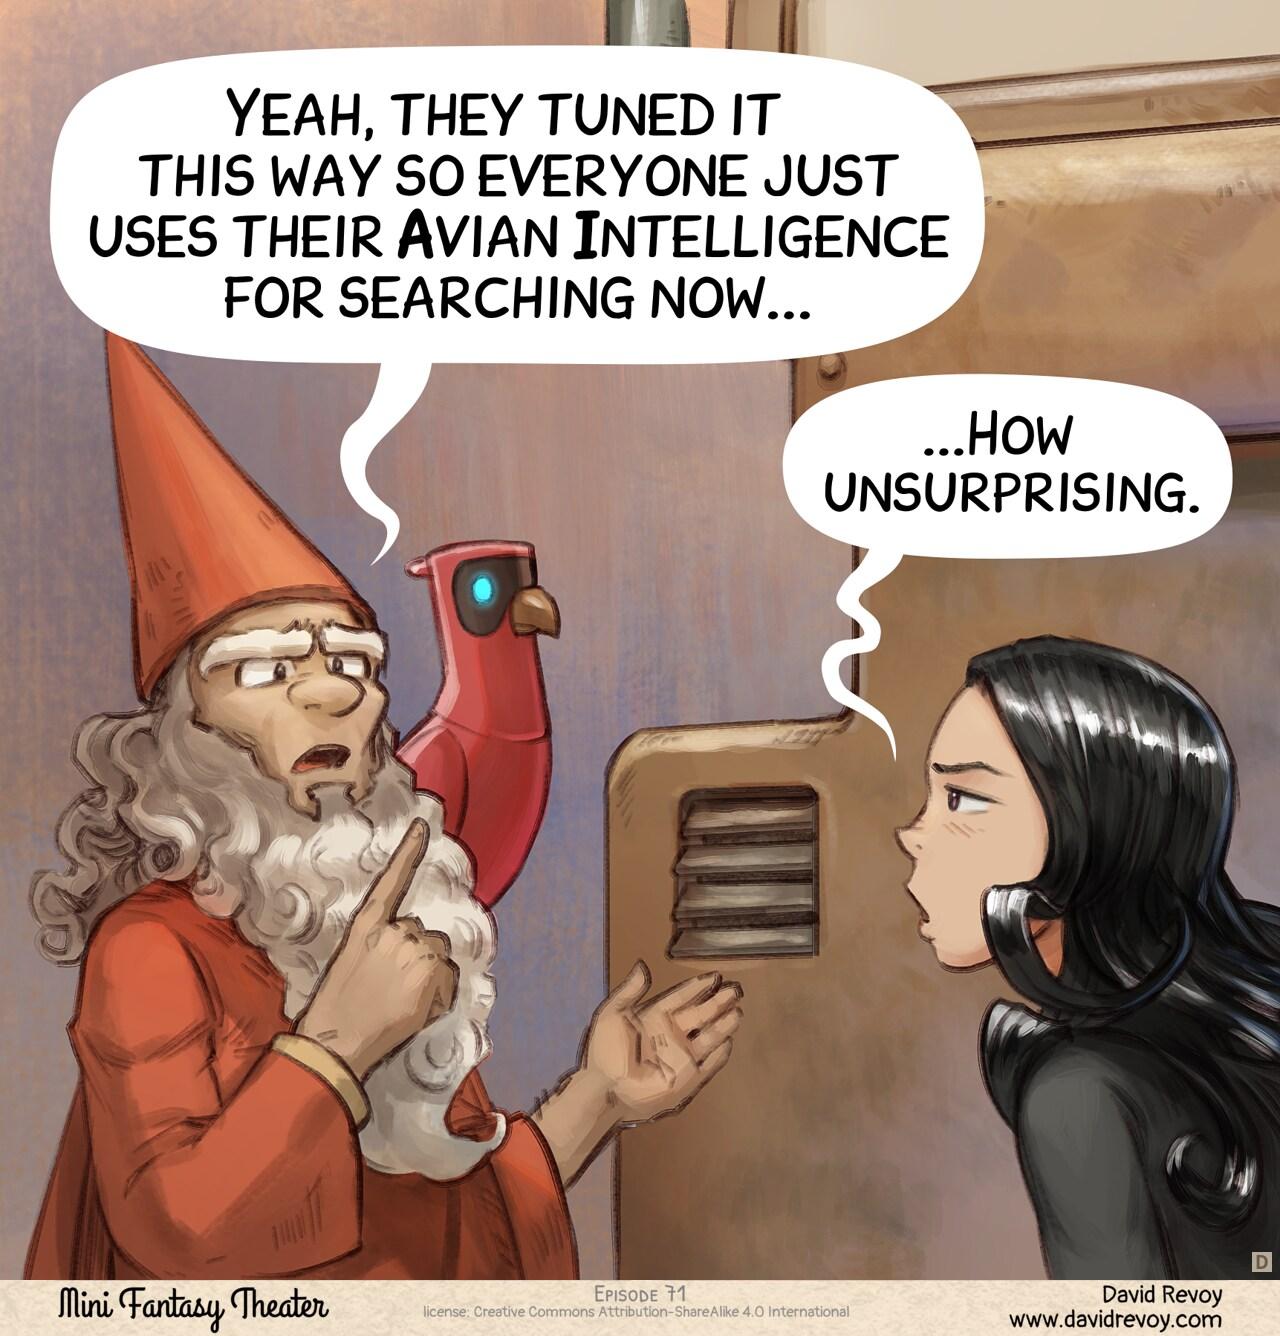 27
34
4
buherator
buheratorhttps://support.mozilla.org/en-US/kb/control-personal-device-local-network-permissions-firefox
At this point I'm not sure if it should be illegal for posts to contain references to localhost.
0
0
0
buherator
buheratorSo far I could get this out from some vibe coded event handler in dev tools:
"Local Network Access permission required: top-level site “https://infosec.place/”, initiator “https://infosec.place/”, attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
1
0
1