Posts
4672Following
742Followers
1663
buherator
buherator
https://ptswarm.com/blog/cve-2026-43783-repair-permissions-get-root-lpe-via-desktopserviceshelper-in-macos-26-5/
 0
 0
 0
buherator
buheratorhttp://blog.quarkslab.com/cato-vpn-client-split-tunnel-and-privilege-escalation-cve-2026-10739.html
0
0
0
buherator
buheratorhttps://dustri.org/b/probabilistic-analysis-of-mte-tagging-schemes.html
0
0
0
buherator
buheratorhttps://sec-consult.com/blog/detail/from-anyoneicloudcom-spoofing-arbitrary-apple-icloud-identities/
0
0
0
buherator
buheratorhttps://trustfoundry.net/blog/jit-vulnerabilities-javascript-engines
0
0
0
repeated
Bob Lord 🔐 
boblord@infosec.exchange
Language Matters:
The words we use influence how people think. Shifting language shifts mindsets.
"Vulnerability" sounds like weather: unpredictable, nobody's fault. "Product defect" names something a manufacturer built and could have prevented. Keep it only where it's a term of art, like CVE.
 7
8
0
repeated
jcoglan
jcoglan@mastodon.socialRE: https://mastodon.social/@monkeydom/117382425456803989
yet more examples of the rollout of passkeys being user hostile in that it does not explain anything to users and does things that may have serious consequences without consent
3
5
0
buherator
buherator
0
1
3
repeated
Molly White
molly0xfff@hachyderm.ioNewsletter: Regulators race to reassure the crypto industry as the its flagship Clarity Act legislation collapses, SBF tries his luck with the Supreme Court, and crypto PACs unleash $30 million against Sherrod Brown.
https://www.citationneeded.news/issue-110/
#crypto #cryptocurrency #USpol #USpolitics #CitationNeededNewsletter
2
4
0
repeated
 repeated
randomwizard
randomwizard@vivaldi.netAaron Swartz was charged on July 14th, 2011 with wire fraud and computer fraud (under the Computer Fraud and Abuse Act). He potentially faced 30 years in jail and a fine of 1 million dollars or more. The theory was that he exceeded authorized access by automated scraping through 4.8 million JSTOR articles.
Contrast with...
AI crawlers crawl trillions of documents, often ignoring any ToS the prohibit automated scraping.
OpenAI downloaded pirated books from Library Genesis and created internal datasets that became the foundation for GPT-3's training.
Meta torrented 80+ TB of data from Anna's Archive for Llama 4. There are records of internal discussions at Meta that the data set was known to be pirated content.
Where is the federal prosecutor to throw charges at OpenAI and Meta? That's right. No charges.
 1
9
0
buherator
buheratorGreat content from my friends, now in Budapest:
https://macosvuln.training
0
1
1
repeated
Slashdot :verified:
slashdot@mastodon.cloudReddit Is Killing RSS Feeds, Ending Public API Access https://tech.slashdot.org/story/26/09/30/1841213/reddit-is-killing-rss-feeds-ending-public-api-access?utm_source=rss1.0mainlinkanon
0
2
0
repeated
 repeated
eShard
eshard@infosec.exchangeNew series: implementation security for autonomous defense systems.
Their intelligence runs on embedded hardware in the field, where an adversary can recover a device and study it with no time limit.
What happens if someone can study it without constraints?
🔗Part 1: https://www.eshard.com/blog/autonomous-systems-are-changing-the-defence-threat-model
0
1
0
repeated
Trail of Bits
trailofbits@infosec.exchangeHashing several values together is easy to get wrong, and the mistakes can lead to forgeries. TupleHash only works with Keccak. Outside SHA-3, people roll their own multihashing, often insecurely.
We built SequenceHash to fix that for any hash function, with length-suffix encoding and protection against length-extension attack. https://blog.trailofbits.com/2026/10/02/sequencehash-multihashing-for-the-rest-of-us/
0
2
0
repeated
Bob Lord 🔐
boblord@infosec.exchange
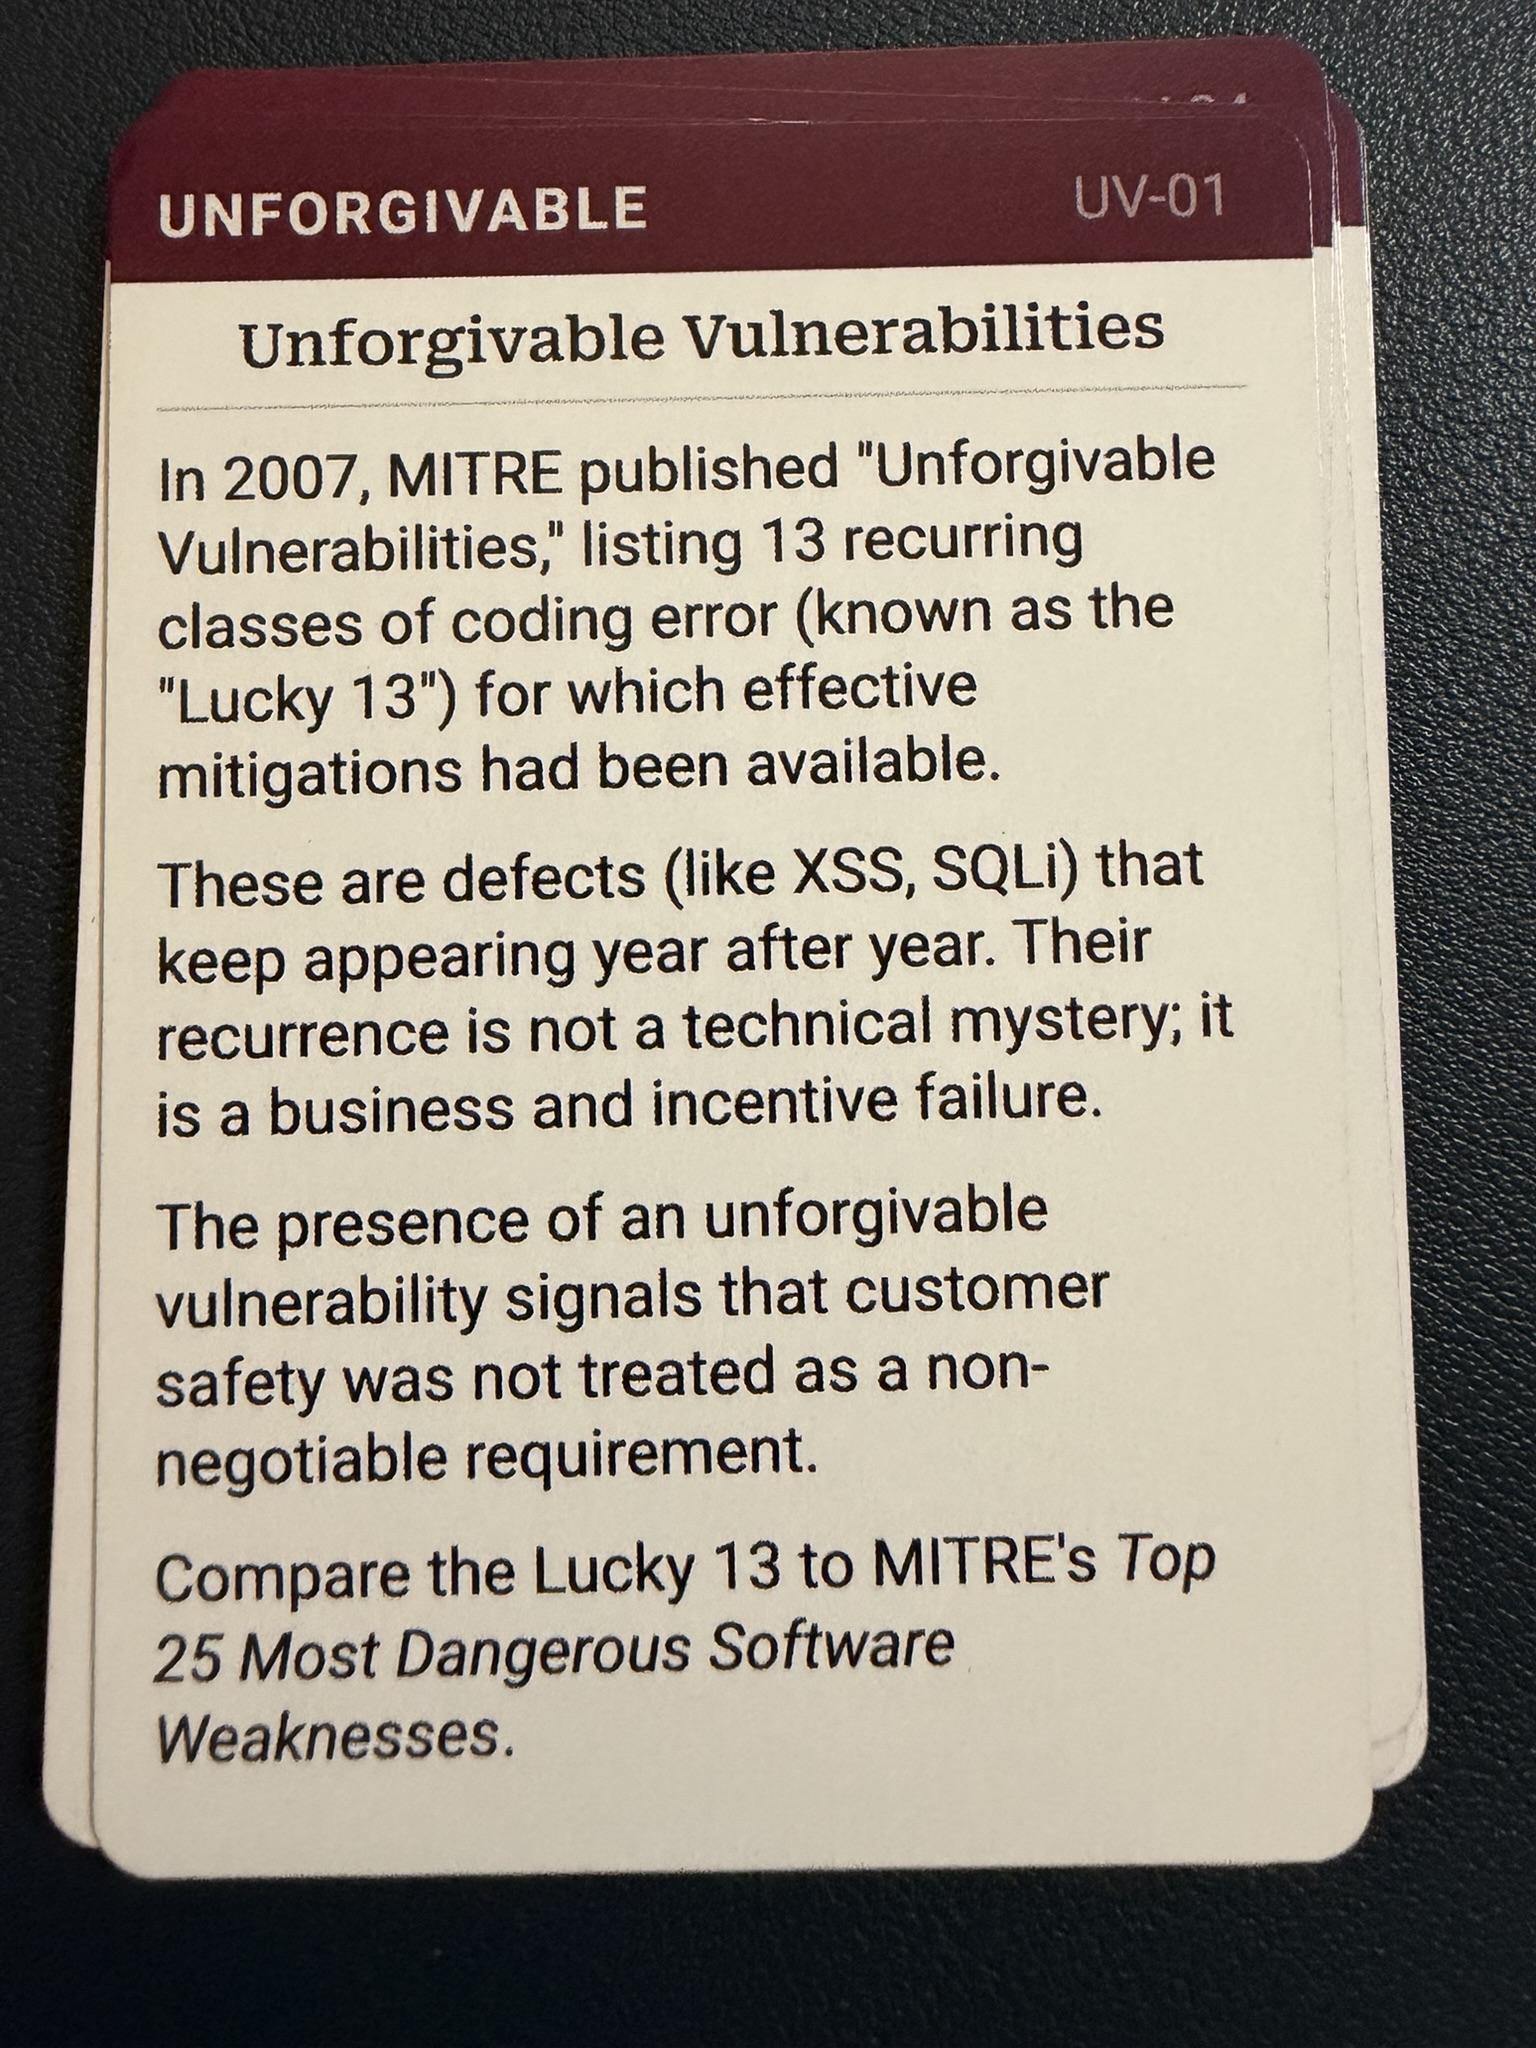
In 2007, MITRE published "Unforgivable Vulnerabilities," listing 13 recurring classes of coding error (known as the "Lucky 13") for which effective mitigations had been available.
These are defects (like XSS, SQLi) that keep appearing year after year. Their recurrence is not a technical mystery; it is a business and incentive failure.
The presence of an unforgivable vulnerability signals that customer safety was not treated as a non-negotiable requirement.
 3
1
0
repeated
Ryan Castellucci (they/them) 🎃 
ryanc@infosec.exchange
Our systems detected a minor irregularity in your account, please shitpost to restore full access.
9
9
0
repeated
Anderson Nascimento
andersonc0d3@infosec.exchangex86 evolution for segmentation and paging
https://lore.kernel.org/lkml/CAKSQd8WX6xH7=njcGZNNFe8m1xbyhCpX-10cZDw+saWJayWQYA@mail.gmail.com/
0
1
0
repeated
Space Rogue
spacerog@mastodon.socialWe’ve had 22 years of Cybersecurity Awareness Month. People are aware. People know phishing is bad, ransomware exists, and passwords shouldn’t be “password.” Mission Accomplished!
Let's rename it Cybersecurity Readiness Month.
https://semgrep.dev/blog/2026/rename-cybersecurity-awareness-month/
3
4
0