Posts
4648Following
742Followers
1662
 repeated
abadidea
0xabad1dea@infosec.exchangePostmortem of a little community hobby wiki struggling to survive an extinction-event-tier DDOS purely because they banned one guy for using Claude on the wiki https://blog.xkeeper.net/the-cutting-room-floor/tcrf-2026-ddos-postmortem/
 5
8
 0
repeated
Romain THOMAS
rh0main@infosec.exchangeRethinking Reverse Engineering for the AI Era:
https://www.romainthomas.fr/publication/26-rethinking-reverse-engineering-for-the-ai-era/
0
1
0
repeated
lcamtuf 
lcamtuf@infosec.exchange
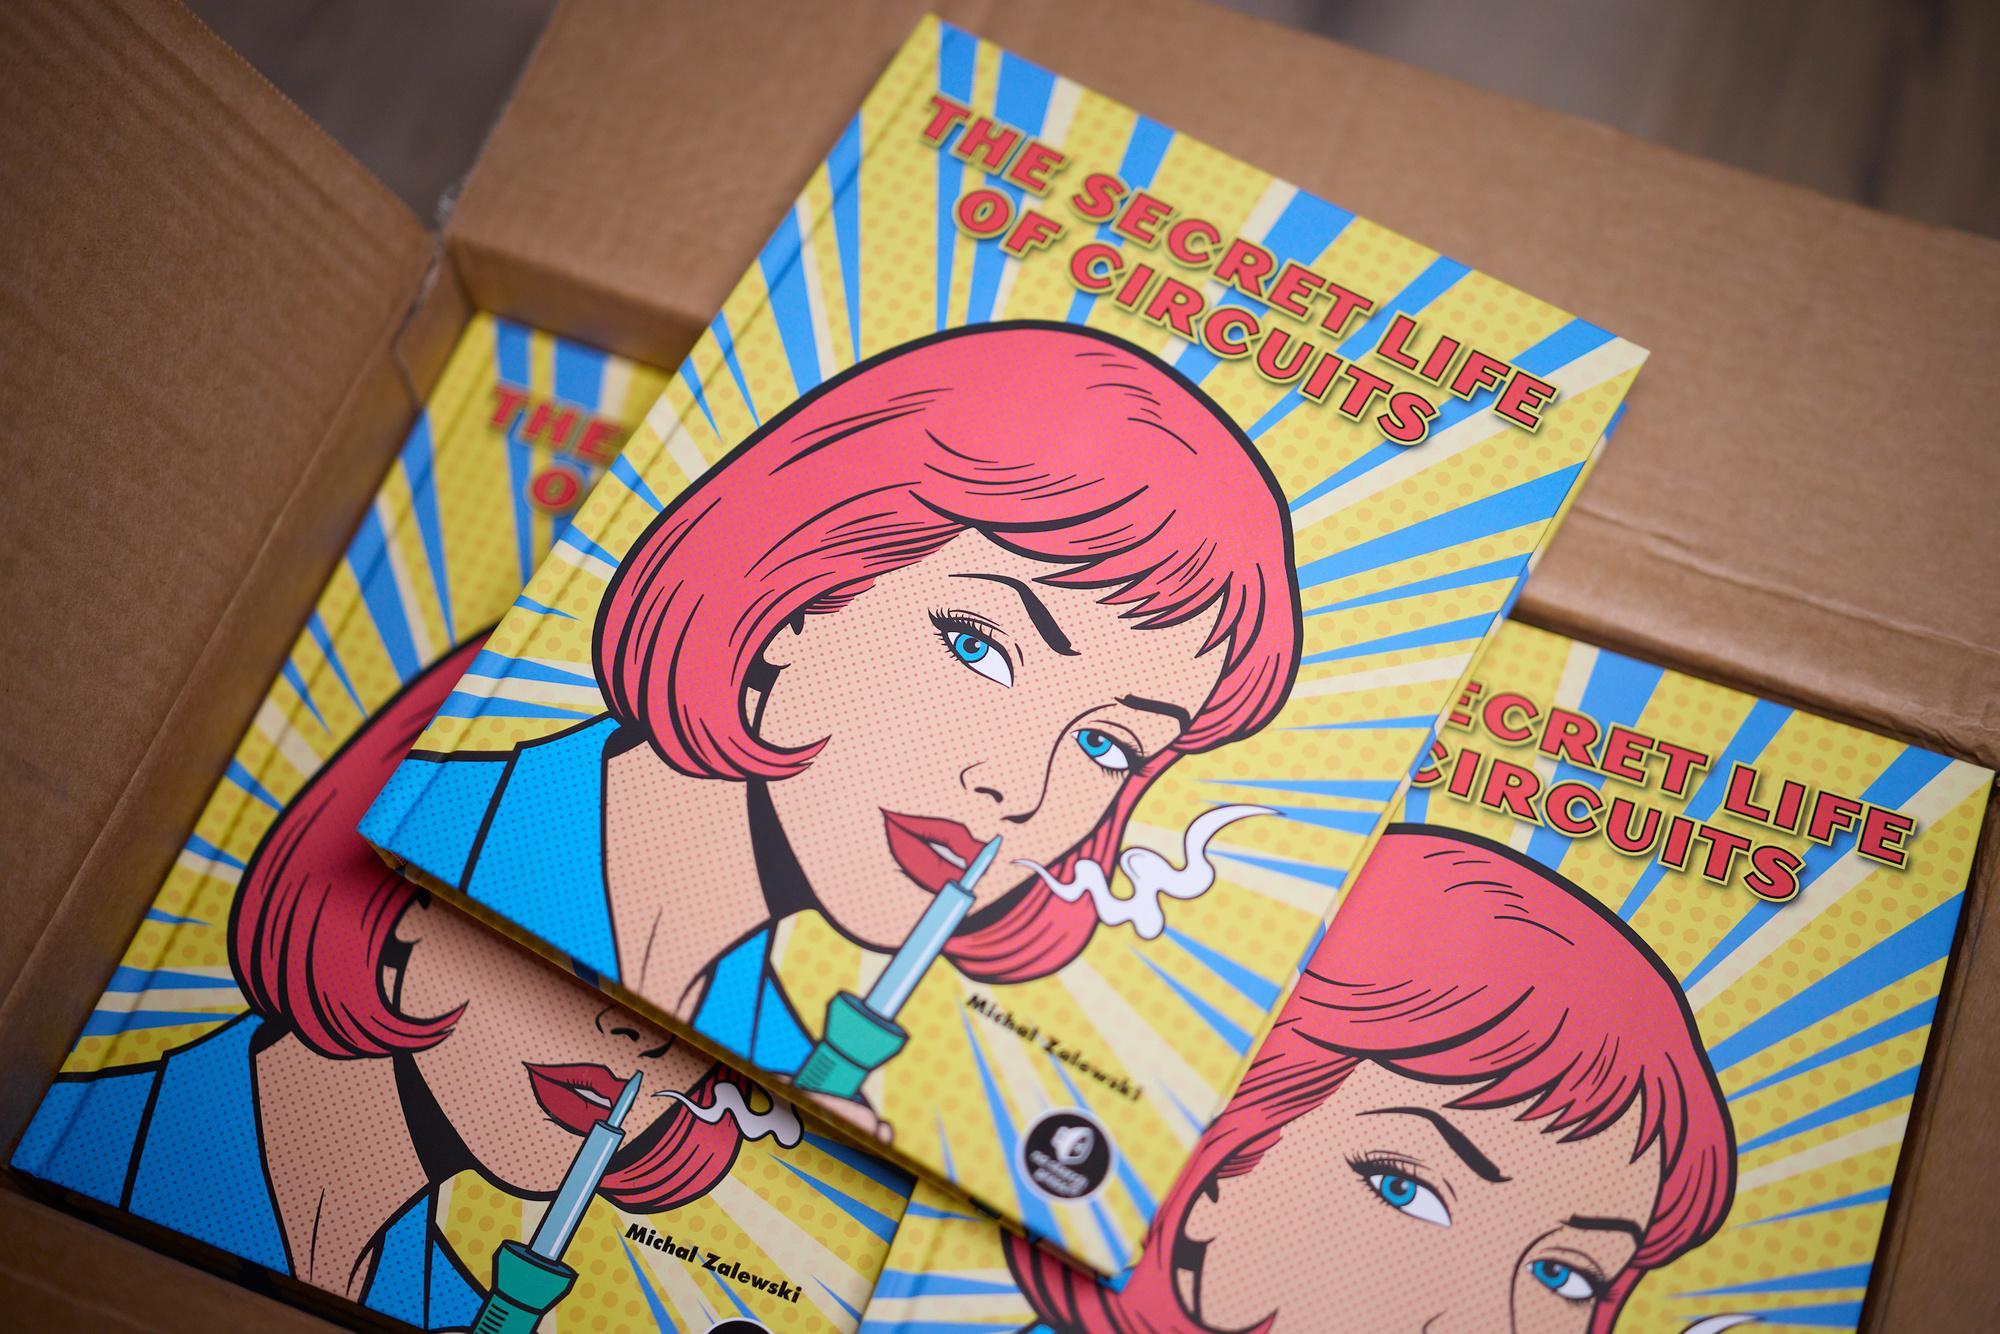
I tempted to do a small giveaway: reply with your best success *or* horror story related to electronics. I'll pick ~3 winners around EOW and send them a copy of The Secret Life of Circuits.
Plz no AI slop. Won't ship to Russia.
 9
3
0
repeated
InfoCon
InfoCon@defcon.socialWebseeds should be working again for https://infocon.org/ #InfoCon.
There was a problem with http range requests that should now be fixed. Please let us know if you see a difference!
 0
1
0
repeated
4Dgifts
4Dgifts@mastodon.socialAny pentesting firm behaving like OpenAI would be shutting down and counting lawsuits within a couple of months.
This new rera of Big AI doing cyber surely feels like the late 1980s/early 1990s of the Internet Wild West
1
2
0
repeated
Paul Cantrell
inthehands@hachyderm.ioRE: https://cosocial.ca/@mhoye/117326705107715161
That last paragraph is a compelling point that runs deep.
0
5
0
repeated
Alesandro Ortiz 🇵🇷🏳️🌈
AlesandroOrtiz@infosec.exchange@xssfox More interesting technical details here (I can't vouch for accuracy):
https://collusion.wiki/
https://transluce.org/agent-activity
0
2
0
repeated
Hanno Zulla
hzulla@infosec.exchangeRE: https://neuromatch.social/@jonny/117324790823856750
This thread is incredibly funny.
Apparently, any user can ask Meta's brand new chatbot Muse to zip and send its whole server-side VM OS filesystem system to the user.
@jonny is going live through the intestines of the filesystem right now.
He reports extremely shoddy work while also a lot of malovent instructions by Meta to the chatbot against the user.
1
3
0
repeated
Hanno Zulla
hzulla@infosec.exchangeWe're big fans of Muse (the band) in this household and it's incredibly ironic that Muse (the chatbot) forcibly took the social media handles of Muse (the band). Because what're Muse (the band)'s lyrics often about? Sci Fi and techno dystopia.
1
3
0
repeated
K. Ryabitsev-Prime 🍁
monsieuricon@social.kernel.orghttps://people.kernel.org/monsieuricon/using-shallow-git-tarballs-for-ci
1
4
0
repeated
phrack@bird.makeup
phrack@bird.makeup
Your weekend reading assignment has arrived early.
A first taste of the upcoming, still-under-wraps Phrack 73: “THE PROXY THAT MADE NO SENSE” by @mikko.
https://archives.phrack.org/dl/73/the-proxy-that-made-no-sense.pdf
 0
4
0
repeated
Talos Vulnerability Reports
talosvulnsApple macOS CoreWLAN information disclosure vulnerability
https://talosintelligence.com/vulnerability_reports/TALOS-2026-2376
0
1
1
buherator
buheratorhttps://labs.watchtowr.com/is-this-a-joke-in-the-auth-header-f5-big-ip-unauth-heap-overflow-to-rce-cve-2026-94127/
1
1
2
buherator
buheratorhttps://www.thezdi.com/blog/2026/9/23/cve-2024-0244-a-heap-buffer-overflow-in-the-canon-mf753cdw-printer
0
0
1
buherator
buheratorhttps://bughunters.google.com/blog/pagebreak-real-world-findings
0
0
1
repeated
Adam 'pi3' Zabrocki
adam_pi3@bird.makeupI'm hiring an exceptional Offensive Security Researcher for my team at NVIDIA (Offensive Security Research - OSR).
Firmware, microcode, RISC-V, hypervisors, and shipping mitigations like HW CFI, Memory Tagging, and Pointer Masking from the ground up.
0
3
0