
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator that is a fine question. I will have to check why
 1
 1
 0
Scary "Grampus" Jerry 👻
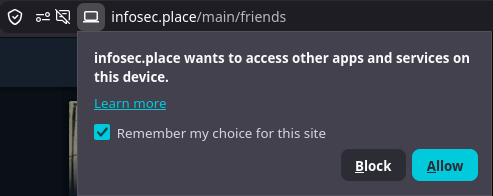
jerry@infosec.exchange@buherator thanks - what browser is that? I am trying to replicate it.
1
1
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator if you scroll back to where you were last night (if you know where that was), do you get another pop-up like that? I am wondering if it;s some sort of xss in a post that akkoma isn't handling.
1
1
0
buherator
buheratorSo far I could get this out from some vibe coded event handler in dev tools:
"Local Network Access permission required: top-level site “https://infosec.place/”, initiator “https://infosec.place/”, attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
1
0
1
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator oh interesting. Something is borked. That is very very interesting. if you have any ability to play with it to narrow down which posts it might be, I (and other akkoma users) would be grateful
2
1
0
DEY!
dey@mastodon.social@buherator @jerry i found it. :) Its the web url trying to access the apps to find if you have the mastodon app and then try and trigger to open it. :-) Had me curious too :D :D
Nothing too bad.
2
0
0
buherator
buheratorhttps://support.mozilla.org/en-US/kb/control-personal-device-local-network-permissions-firefox
At this point I'm not sure if it should be illegal for posts to contain references to localhost.
0
0
0
DEY!
dey@mastodon.social@buherator @jerry So you know how certain sites have their web app for mobile devices too. Usually facebook or instagram they want to switch to the app. In this case Mastodon is trying to see if the app is installed in the computer (in case of MAC even windows) or the phone. Its not specific to infosec.place (or maybe it is I am not on that instance)
1
0
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@dey @buherator I also think this is happening due to another instance referencing an in image embed with that URL, and akkoma is passing it on to the web browser to try to fetch, which is causing the issue. That http://localhost:3000, btw, is the default port that the mastodon app server works from. 99.5% this is a badly configured mastodon instance + some issue with akkoma.
1
1
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator @dey it's giving you that address to fetch like any other image that appears in your timeline. localhost links shouldn't be sent and I need to figure out if akkoma has a way to prevent that.
2
1
0
sclaw
sclaw@activitypub.ro
1
0
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@sclaw I did not set up the proxy. I do think that might solve it. it would just present a broken image, I suspect, in this instance.
1
1
0
Viss
Viss@mastodon.social@jerry @dey @buherator i've been seeing this popup too - not on here, but elsewhere, which tells me if i went to go to inspector, i would also probably see some kinda 'call to localhost', which firefox is now throwing alerts for.
iiiiiiinteresting
0
0
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator @dey there's no code, it's just in the body. I am working on setting up the proxy which will hopefully fix that
1
1
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@buherator @dey fair. after far too many typos, the local media proxy is up and running, so with any luck, you won't see that any more.
2
0
0
DEY!
dey@mastodon.social@jerry @buherator wow you are good at computer have you considered doing it professionally?
1
0
0
Scary "Grampus" Jerry 👻
jerry@infosec.exchange@dey @buherator See, if I were good at computers this wouldn't have been an issue. I think i should have set up the media proxy from the start, but I was cheap and trying to save bandwidth
0
0
0
sclaw
sclaw@activitypub.ro
1
0
0
buherator
buherator#Firefox
RE: https://infosec.place/objects/c55e1bcb-86a9-4d16-b9fb-83dccaeb4dad
2
2
3
Frederik Braun �
freddy@security.plumbing@buherator can you (privately) share what devtools is logging? Is this reproducible?
1
0
0
buherator
buherator"Local Network Access permission required: top-level site “https://infosec.place/”, initiator “https://infosec.place/”, attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
I could reproduce it by scrolling a shit ton in my timeline (won't do again), but I think a minimal test case would be a simple `img src="http://localhost...` served from a non-local origin.
In that case though the source would be there in Inspector, but in case of Akkoma infinite scroll does some magic that prevents me from simply looking up the tag by URL, that's why I'm thinking if some kind of "stack trace" is available for network events that would lead me to the offending element?
1
0
0
Frederik Braun �
freddy@security.plumbing@buherator og-card in the URL? looks pretty much like you're black holing some social networking to 127.0.0.1 and therefore blocking some preview image
2
0
0
Frederik Braun �
freddy@security.plumbing@buherator You could also log to a file with about:logging (select "Network") or use the Firefox Profiler (https://profiler.firefox.com/). - All of this will stay local, unless you share the log / profile (May contain cookies and other substances)
0
0
1
Frederik Braun �
freddy@security.plumbing@buherator Huh....now I _really_ want to see a log file. :) You should try to find the toot that caused this first.
1
0
0
buherator
buheratorBut I have an idea for a repro, adding then deleting an <img> to the document. I guess what makes debugging this difficult is that you need a point-in-time document snapshot to see the true source. Even seeing the <img> may not be meaningful without e.g. it's surrounding <div> with the post content.
0
0
0