Posts
4665Following
742Followers
1662
 repeated
Lukasz Olejnik
LukaszOlejnik@mastodon.social
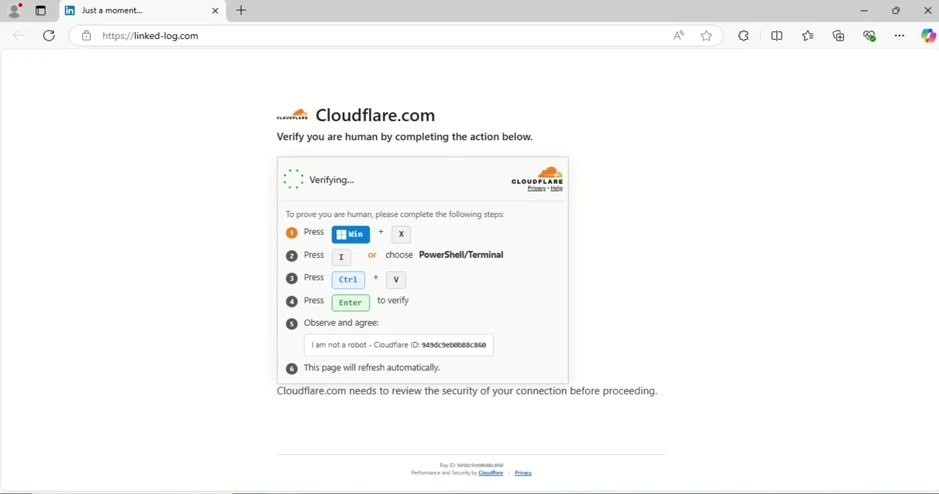
Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
 6
4
 0
repeated
SSD Secure Disclosure
SSDSecureDisclosure@infosec.exchange🚨 New advisory was just published!
A heap buffer overflow in a Windows DCOM service can be leveraged to escalate privileges from a Medium IL standard user to SYSTEM IL, an issue that occurs when attacker-controlled Power Setting data and length are passed to the PSM callback.
This vulnerability earned 3rd place in the Windows LPE category at TyphoonPWN 2026. Read all the details at: https://ssd-disclosure.com/dcom-service-psmserviceexthost-lpe/
0
2
0
repeated
 repeated
James Kettle
albinowax@infosec.exchangeTwo hours till my HTTP Terminator talk kicks off at SEC-T! You can catch the livestream at 9:15 UTC:
https://www.youtube.com/watch?v=S6R7cBZDdK4
0
3
0
buherator
buheratorhttps://github.com/v-p-b/mdsrv
Static webserver that renders #Markdown files and #MermaidJS diagrams for your viewing pleasure. With live updates!
#python #llm
0
1
4
repeated
Hackaday
hackaday@robot.villasReverse Engineering The Philips PM5139
https://hackaday.com/2026/09/09/reverse-engineering-the-philips-pm5139/
0
2
0
repeated
CISA KEV Tracker
cisakevtracker@mastodon.socialCVE ID: CVE-2026-20079
Vendor: Cisco
Product: Secure Firewall Management Center (FMC) and Security Cloud Control (SCC) Firewall Management
Date Added: 2026-09-09
CVE URL: https://nvd.nist.gov/vuln/detail/CVE-2026-20079
0
1
0
repeated
CISA KEV Tracker
cisakevtracker@mastodon.socialCVE ID: CVE-2026-87491
Vendor: Google
Product: Chromium V8
Date Added: 2026-09-09
CVE URL: https://nvd.nist.gov/vuln/detail/CVE-2026-87491
0
1
0
repeated
blacktop
blacktop@mastodon.socialHigh level diff of iOS 27 beta8 vs. iOS 27 RC 🎉
https://github.com/blacktop/ipsw-diffs/tree/main/27_0_24A5430a_vs_27_0_24A435/README.md
0
1
0
repeated
Volexity 
volexity@infosec.exchange
Earlier this month, @volexity detected multiple Chinese threat actors launching attacks against its customers using chained 0-day exploits in Google Chrome (CVE-2026-85046 & CVE-2026-87491) and Microsoft Windows (CVE-2026-85880). Volexity observed threat actors it tracks as UTA0560 and JungleBamboo using variations of the same exploits to deliver different malware implants. These implants ranged from a JScript backdoor (GRIMWEDGE) to a fake Google Gemini Chrome extension (LONGTALE).
Read the full analysis of the exploit chain and post-exploitation tradecraft here: https://www.volexity.com/blog/2026/09/09/mind-the-patch-gap-multiple-chinese-threat-actors-chain-0-day-exploits-in-chrome-windows/
#DFIR #threatintel
 0
2
0
buherator
buheratorHeat.
Heat.
[Music]
1-2-3
0
0
1
repeated
kaaswe
kaaswe@swecyb.comRE: https://mstdn.social/@jukkan/117240247968300759
I just love this:
”Feature #23 is worth noting in isolation. LinkedIn collects the user’s Do Not Track preference, then excludes it from the fingerprint hash (line 9512, excludes: { doNotTrack: true }). They record that you asked not to be tracked. Then they track you.”
1
2
0
repeated
 repeated
Frederik Braun �
freddy@security.plumbingEdit: resolved
Hey, I am an old school vanilla JS person and want to learn what frontend frameworks do people use these days.
Are there any statistics I could look into? Not looking for engineering advice or suggestions what to use.
I hope to get a better understanding of the engineering practices & workflows and security needs to ensure that our security work in web standards can actually land with the users.
Edit: Specifically, I am interested how people modify/insert HTML :)
1
2
0
repeated
J. L. Westover
MrLovenstein@mastodon.socialSecret Panel HERE 🧠 https://patreon.com/mrlovenstein/posts/mind-body-84972760
 5
8
0
repeated
Google Chrome #zeroday
Google is aware that an exploit for CVE-2026-87491 exists in the wild.
https://chromereleases.googleblog.com/2026/09/stable-channel-update-for-desktop_0808145027.html
0
2
0
repeated
Eniko Fox
eniko@mastodon.gamedev.placebear with you? dude that sounds dangerous get out of there
2
4
0
buherator
buherator- #FOSS drops, everyone happy
- #FOSS bugs surface, bitrot needs handling
- Instead of contributing fixes, users use #LLM to solve their specific issues
- #FOSS never gets fixed
Bonus: bugs accumulate so much that the project eventually dies, while everyone regenerates parts of it from scratch on-demand with LLM.
1
1
5
repeated
RE//verse Conference
REverseConf@infosec.exchangeTickets are live and trainings are up too! Round 1 pricing is happening and won’t last long. Now’s the time to grab your ticket: https://re-verse.io
0
2
0