Posts
4665Following
742Followers
1662
 repeated
Ivan Ožić Bebek
obivan@infosec.exchange
CVE-2026-83991: Windows Cloud Files access-check bypass https://github.com/karollooool/CVE-2026-83991-writeup-and-poc
 0
3
 0
buherator
buheratorhttps://capnproto.org/
1) Why didn't I know about this??
2) Why did I have to learn about this because of an article about the authors gamer/geek mansion?
1
1
4
buherator
buheratorNow my muscles are so tense I can barely use vim.
0
0
2
repeated
Trail of Bits
trailofbits@infosec.exchangeAnthropic formalized Fermat's Last Theorem in 13M lines of Lean. We "proved" it in 20 lines by exploiting a bug we found in Lean.
Root cause: Lean's string slicing has two implementations, the logical definition and the compiled C++. At position 2^63 they disagree: one returns "", the other the whole input. This bug causes Lean to accept two contradictory facts, which then lets you "prove" anything, including FLT. https://blog.trailofbits.com/2026/09/09/a-proof-of-fermats-last-theorem-that-fits-the-margin/
0
5
0
buherator
buheratorhttps://blog.scrt.ch/2026/09/08/hp-one-agent-local-privilege-escalation-through-race-condition-cve-2026-5064/
0
1
0
repeated
 repeated
Alex Plaskett
alexjplaskett@bird.makeup
Another 3 Windows LPE's I found just patched in September patch Tuesday!
CVE-2026-68839 - https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-68839
CVE-2026-69720 - https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-69720
CVE-2026-69571 - https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-69571
0
4
0
repeated
natashenka@bird.makeup
natashenka@bird.makeupToday, Project Zero is releasing MAccConc, a tool by @tehjh that enables deterministic testing of race conditions on Linux. It can be used for fuzzing, ad-hoc exploration, regression tests and more!
https://projectzero.google/2026/09/maccconc-race-condition.html
0
6
0
repeated

 repeated
stephenfewer@bird.makeup
stephenfewer@bird.makeupWhile researching last months N-able N-central exploit (CVE-2026-18577, on KEV), we found and reported a new authentication bypass chain (CVE-2026-86206 and CVE-2026-86207). Patched and disclosed by the vendor over the weekend, we have published full details on the @rapid7 blog: https://www.rapid7.com/blog/post/ve-cve-2026-86206-cve-2026-86207-n-able-n-central-authentication-bypass-fixed/
0
1
0
repeated
abadidea
0xabad1dea@infosec.exchangeProject Glasswing:
Claiming to have found 26 thousand real vulnerabilities but only 0.8% of them have resulted in a real fix in a real project after five months is dire. They blame it on the human independent review bottleneck, but human experts being paid for their time definitely have a higher throughput than that when working with data that’s actually actionable.
The assigned-at-Claude severity ratings are also dire. It assigns “high” or “critical” to 91% of findings. Most findings in the real world are low or medium. This should be especially true when using a magic machine to shake out every last little issue that was overlooked by humans focused on the biggest risks.
[Edit: I should be more careful and note that this figure is calculated only from findings which have received a second opinion from project maintainers, which is much higher than the 0.8% fixed rate but much less than the entire dataset, so there’s probably bias towards reviewing those with critical ratings first. However, the maintainers found the high/critical rate to be quite inflated.]
Together this implies it’s generating thousands of trivial or nonsensical findings and labeling them HIGH DANGER CRITICAL MUST FIX, and the human independent verifiers are sifting for the rare needle in this haystack worth passing on. This isn’t really an improvement over the high-noise automated scanners we already had
(This is a corporate blog of someone with their own vulnerability management services to sell, so apply an appropriate number of grains of salt to their analysis. Filter keywords: AI LLM Anthropic)
https://www.vulncheck.com/blog/anthropic-glasswing-receipts
13
13
0
repeated
Xamanismo Coletivo
eliasulrich@hachyderm.io"One guy in #Sweden built a #searchengine to fight Google, and it works.
It's called #MarginaliaSearch.
It runs its own #crawler and builds its own #index instead of borrowing Bing's. It has no ads, no investors, and no loans.
What it does differently: it ranks for text-heavy, non-commercial pages. Personal blogs. Old university pages.
The weird corners SEO strangled. Every result tells you whether the page uses affiliate links and JavaScript, and you can filter them out.
There's an "explore" mode that just shows you random sites from the index. It's open source under AGPL, so you can host your own copy.
It's keyword-based, so don't type a full question at it. Type two nouns and see where you land. Every #searchengine now shows you the same twelve #monetizedpages."
https://marginalia-search.com/
12
48
0
repeated
laluka
laluka@infosec.exchangeHey everyone! 🌹
> Lalu here: Openly sharing @entrypoint_fr 's open CFP & registration to help them kick-start nicely this new cool and red-focused event!
> Finding the right speakers and audience is hard, even more now that AI makes things feel "less special",. But some people are still making this happen, let's join forces! 🍀
---
Join & Apply to Entrypoint by @synacktiv a conference entirely dedicated to **Red Teaming**, coming to Paris on March 19–20, 2027 at Le Dernier Étage.
Expecting 500 attendees from around the world, all talks will be delivered in **English** to bring together as many international profiles as possible 👌
📍 Venue & Details:
- Event page: https://entrypoint.fr/
- Location: https://ledernieretage.paris/
🎤 Call for Papers
If you have a compelling topic to share, we'd love to hear from you. Submissions are open on the following tracks:
- Advanced Pentesting & Red Teaming : ActiveDirectory, Cloud (AWS/Azure/GCP) exploitation, container escapes, lessons learned (full scenario analysis).
- Supply Chain Attacks : Attacks targeting dependency managers (npm, pip, composer), secrets leaked on public platforms (GitHub).
- CI/CD : Advanced pipeline exploitation, loot techniques.
- Physical Intrusion : Methodologies to reach internal networks / target companies physically.
- Malware & C2 : Evasion techniques, obfuscation, custom C2 infrastructure, implant development.
- Post-Mortem Analysis : Analysis of threat actor exploitation methodologies, complex compromise chains.
- AI-assisted offensive security : Offensive use of AI including agentic red teaming, model-assisted vulnerability research, and AI-driven exploitation in real operations.
🎓 Training Days
4 days of hands-on training (Monday, March 15 – Thursday, March 18) covering the same themes.
🎁 Speaker Perks
To make it as smooth as possible for speakers, here's what is covered:
- Travel expenses
- Accommodation : hotel booked for the duration of the conference
- Speaker dinner : a dedicated evening to hang out with fellow speakers
⁉️ Questions
Feel free to ping @_remsio_ on X/discord or official @entrypoint_fr accounts directly if you have any questions or need more details!
See you in Paris! 🇫🇷✌️
0
2
0
repeated
Russia-Ukraine Daily News
rvps2001@mastodon.social🇭🇺 #Hungary has expelled 10 Russian diplomats who "were engaged in activities in Hungary that are unacceptable for diplomats under the Vienna Convention," Foreign Minister Anita Orbán said in a statement on Tuesday.
https://tvpworld.com/95280737/hungary-expels-10-russian-diplomats-foreign-minister-says
0
2
0
repeated
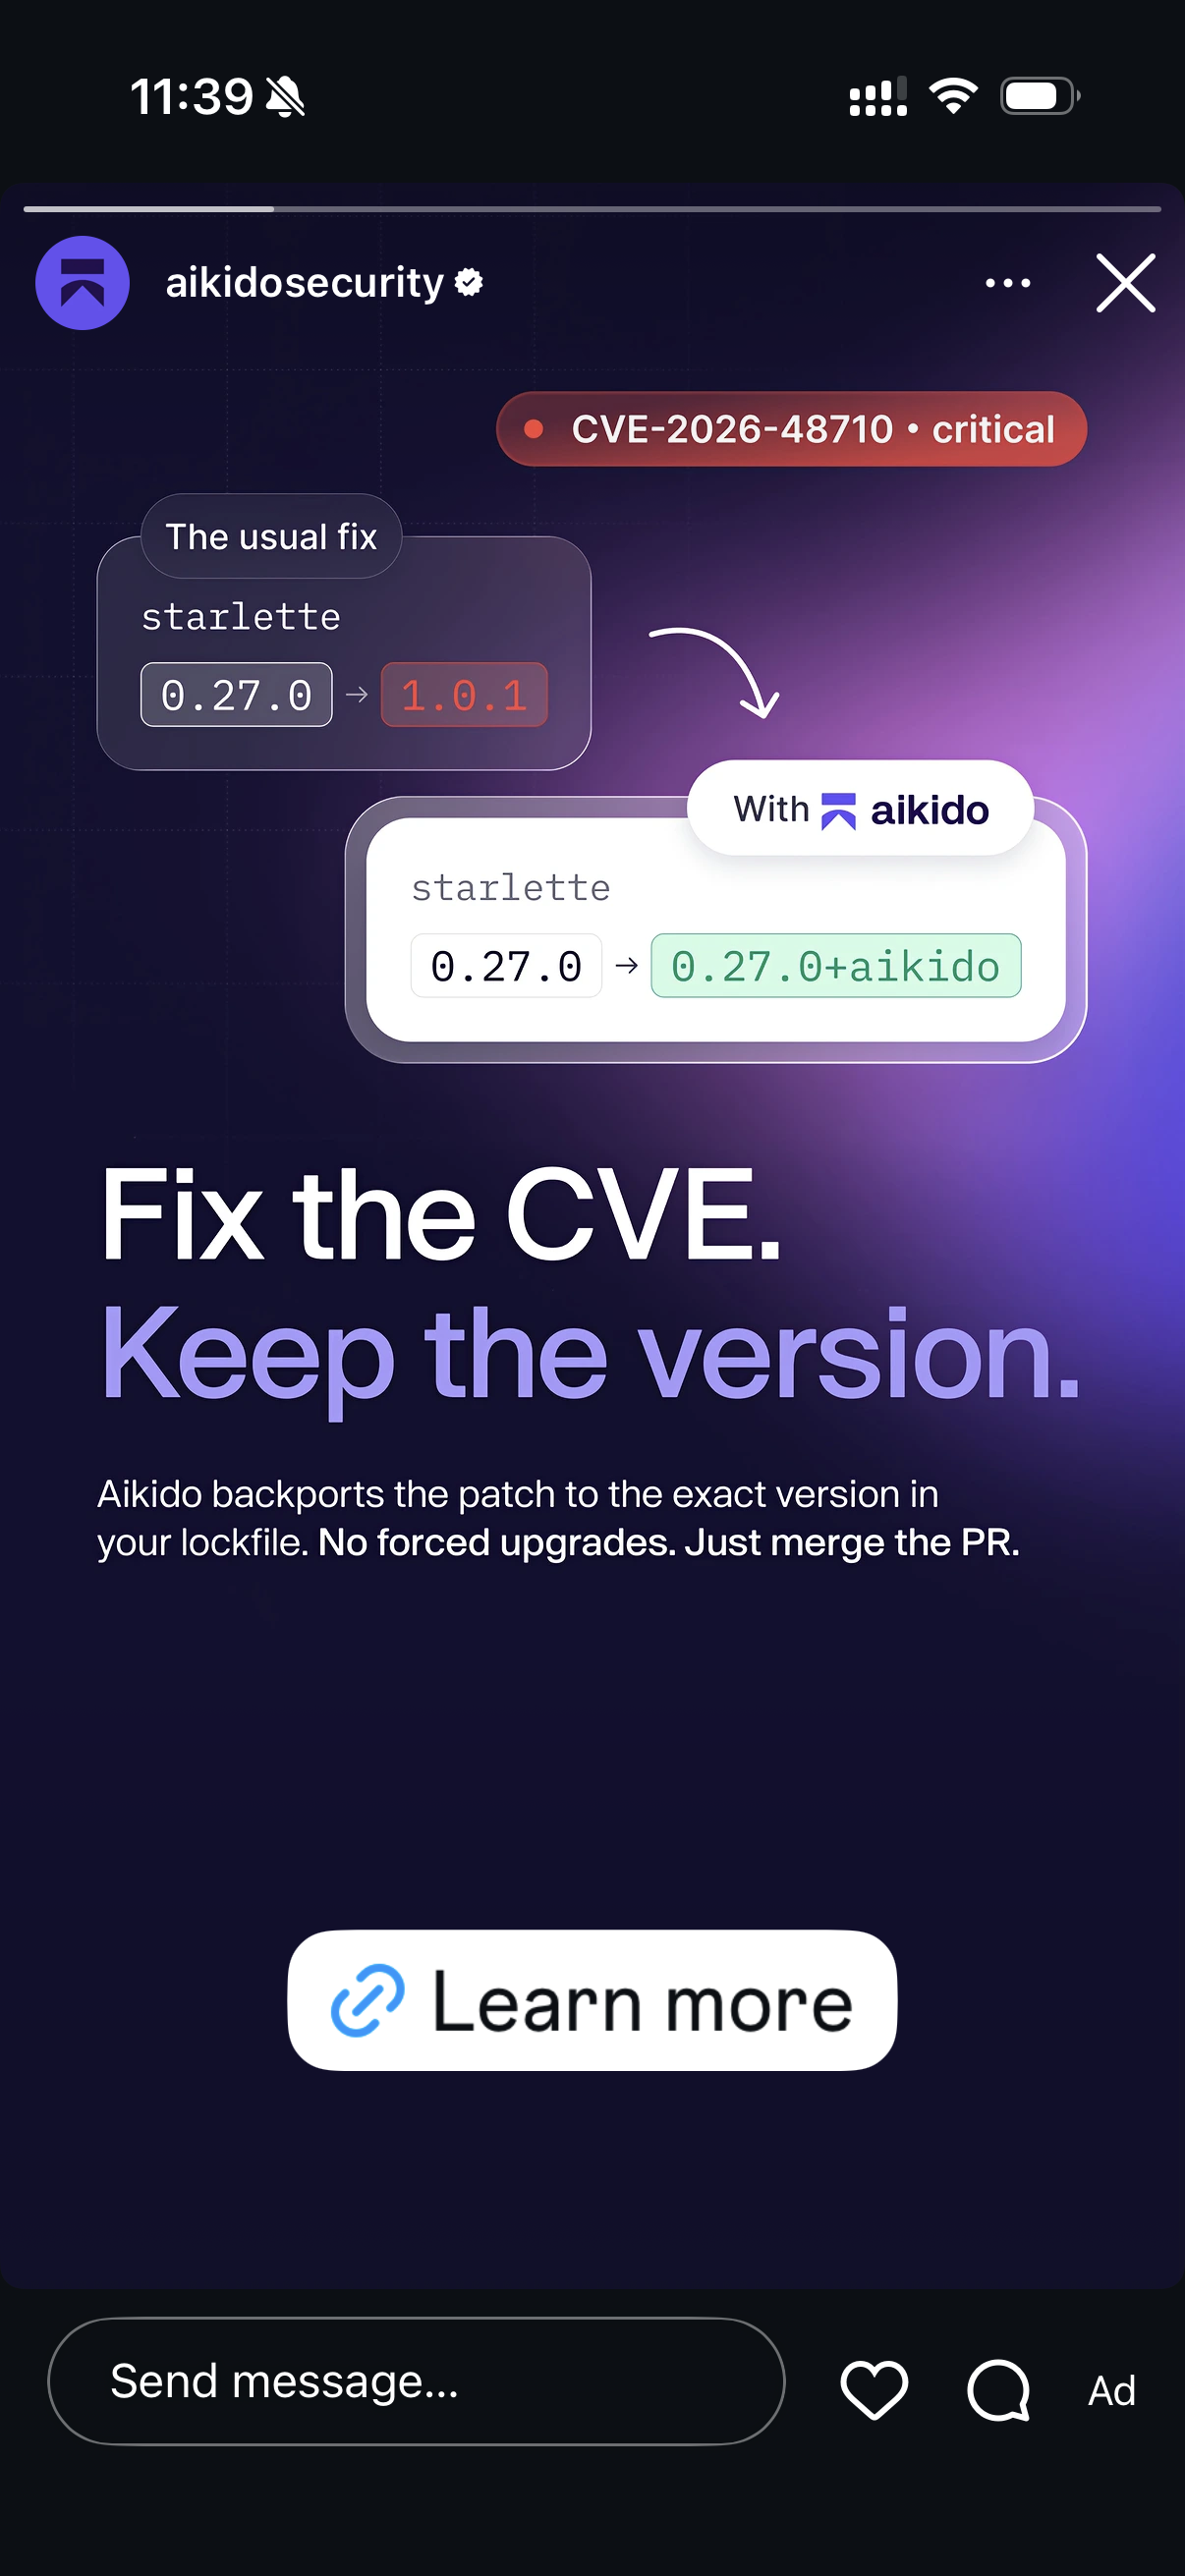
almost every idea i’ve had in my life is better than this can i get a few million dollars of investment (also wtf is wrong with my instagram ads)
 1
1
0
repeated
Angela Miller
Alternatecelt@mastodon.scotPlease boost this for as much reach as possible.
Parton Kirk, where #physics genius James Clerk Maxwell is buried, is being put up for sale. The community is attempting a buy out to save this kirk for science and the local community. They have until 31st of October to secure the funds.
Here's the crowd funder link. You can help prevent this kirk from falling into private hands.
https://www.justgiving.com/crowdfunding/savepartonkirk
#jcmkirk #science #jamesclerkmaxwell #scotland #history
2
4
0
repeated
Phrack
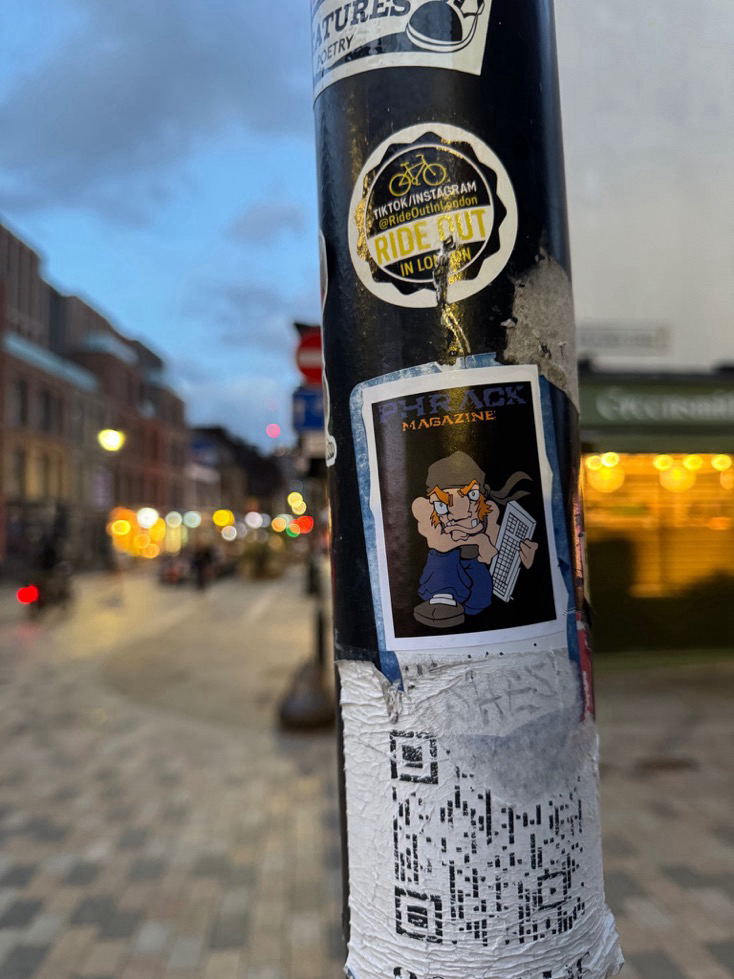
phrack@haunted.computerHello London 🇬🇧
The Phrack team is here and we left our mark around the city.
If you can find any of these stickers, email us for a chance of getting a physical copy of Phrack 73 delivered to your doorstep.
Send proof to hunt@phrack.org and have fun!
 0
6
0
repeated
Matthew McPherrin
mattm@infosec.exchangeI’ve factored the RSA keys of a Certificate Authority...
… from the 90s.
https://mcpherrin.ca/2026/09/07/rsa.html
1
4
0
repeated
docker compose up up down down left right left right b a start
5
12
2