Posts
4645Following
742Followers
1662
 repeated
Kevin Beaumont
GossiTheDog@cyberplace.social
BBC News has 4 YouTube videos up in the past day about OpenAI hacking “governments”, with approaching a million views.
If you want to know the technical details of this elite frontier AI hacking - these are examples of the actual OpenAI agent requests.
It’s really dumb shit. The story here is OpenAI are utterly incompetent at cybersecurity, as are their victims.

 5
5
 0
buherator
buherator#Firefox
RE: https://infosec.place/objects/c55e1bcb-86a9-4d16-b9fb-83dccaeb4dad
2
2
4
repeated
 repeated
David Revoy
davidrevoy@framapiaf.orgThe Degraded Search Engine
Bonus speedpaint: https://www.peppercarrot.com/en/miniFantasyTheater/071.html#bonus
#webcomic #krita #miniFantasyTheater
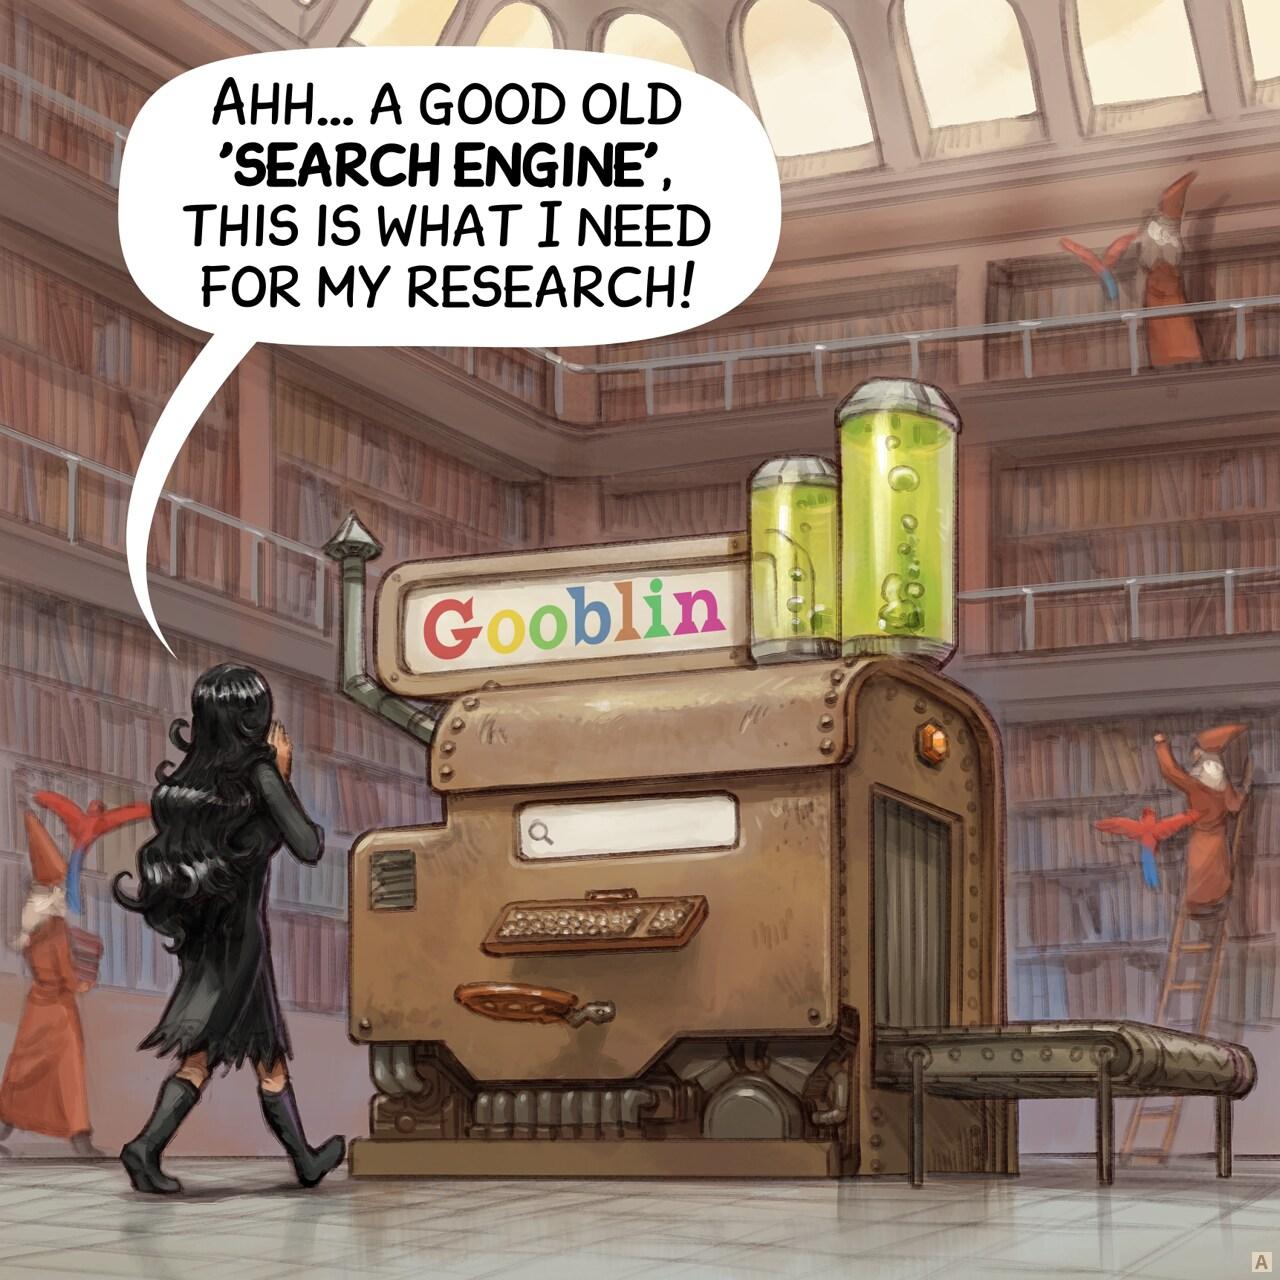
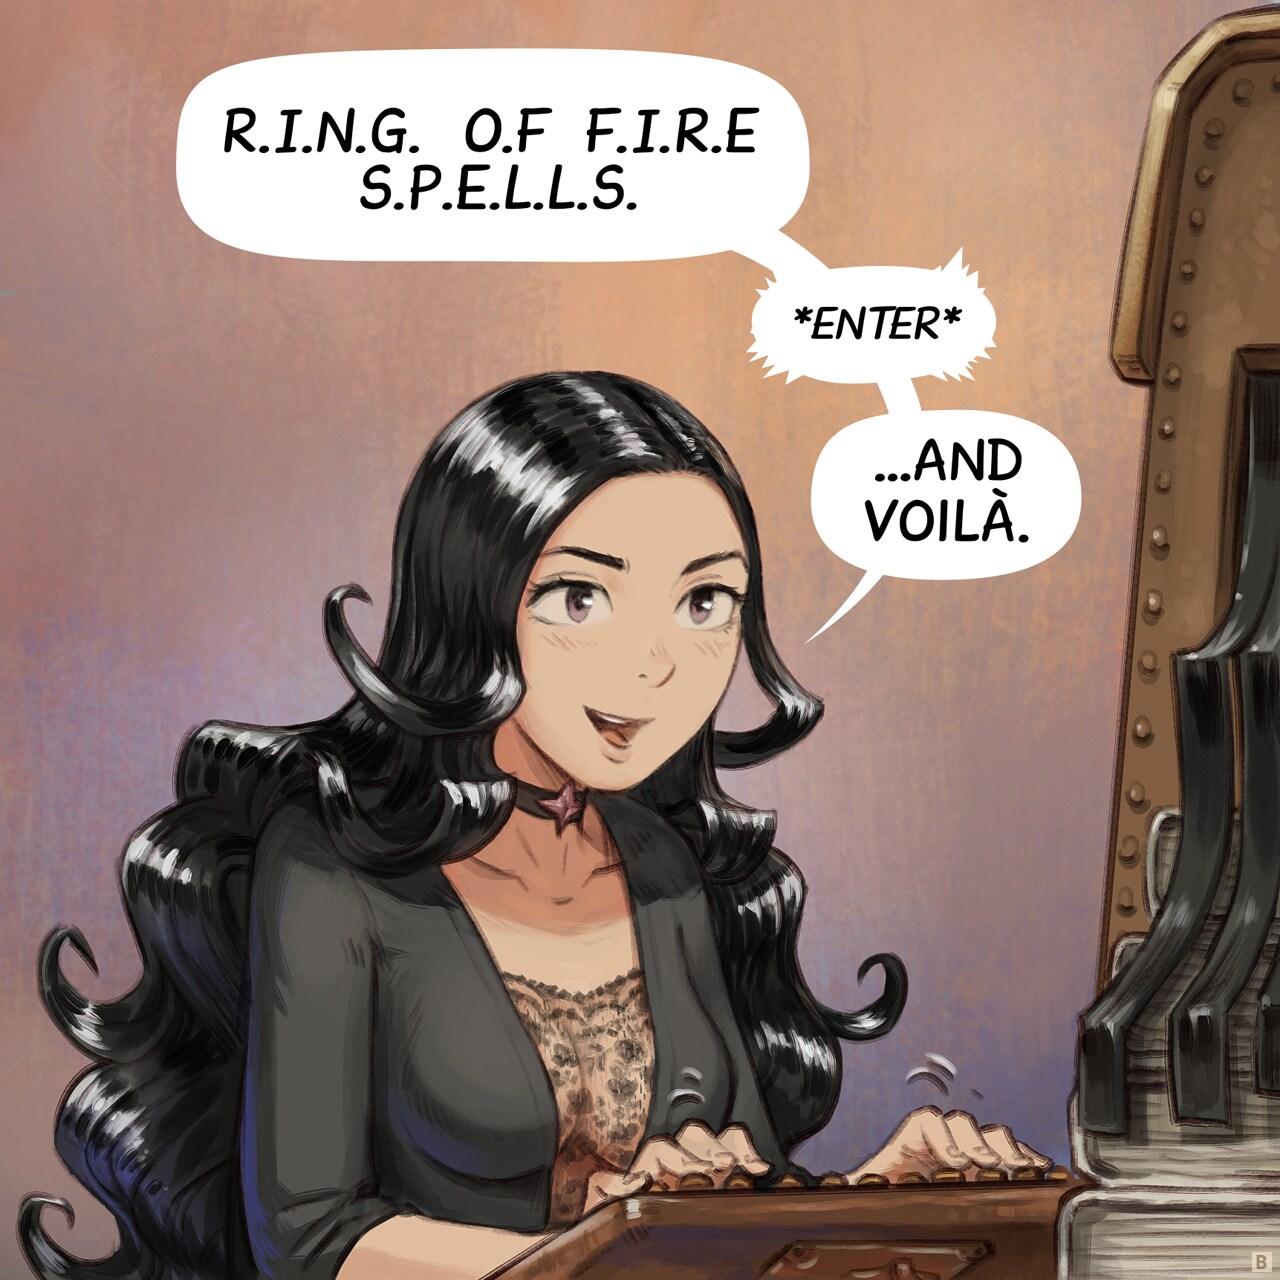
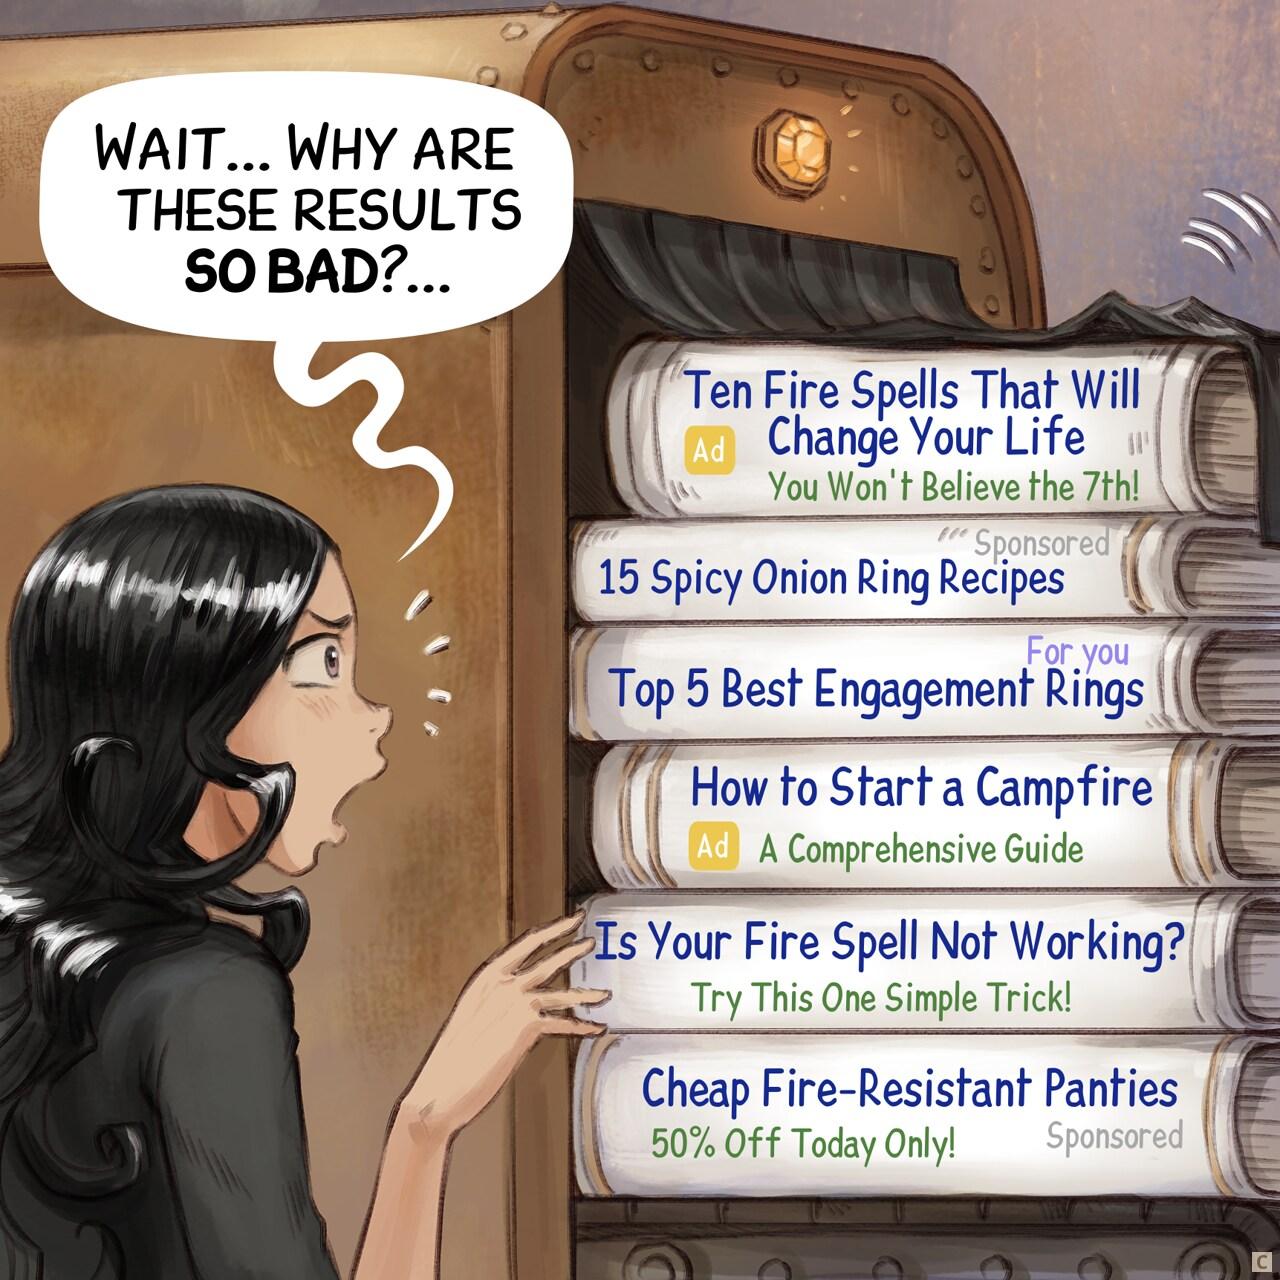
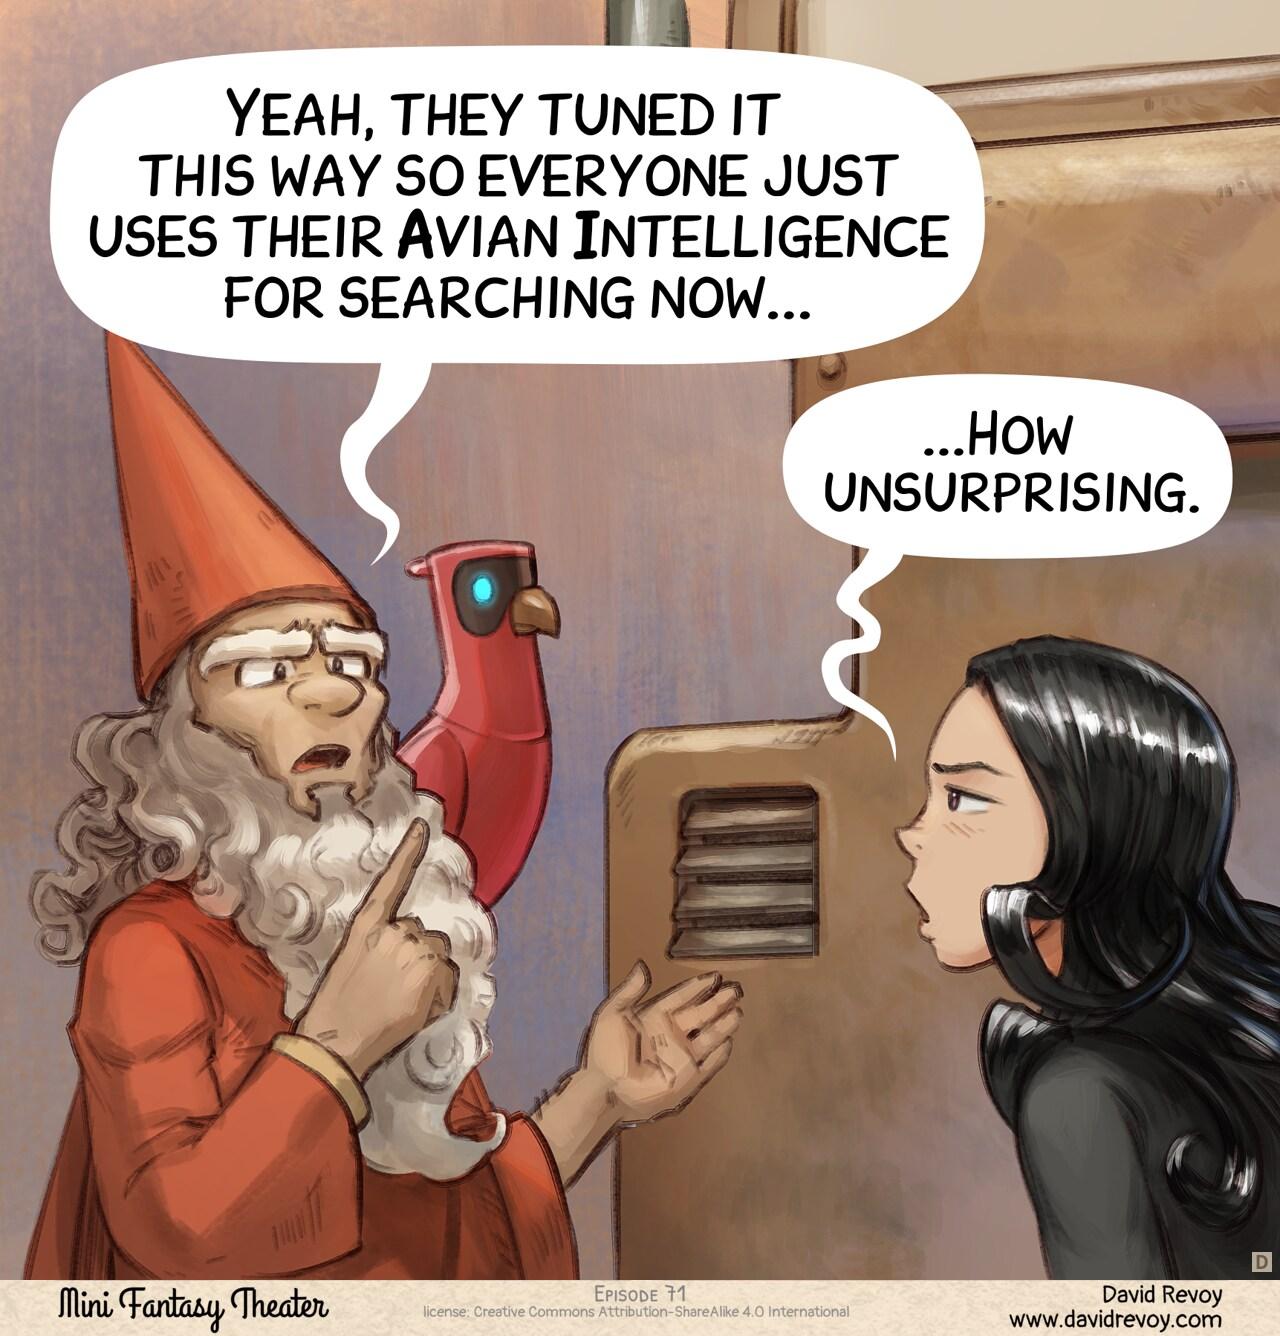 27
34
4
buherator
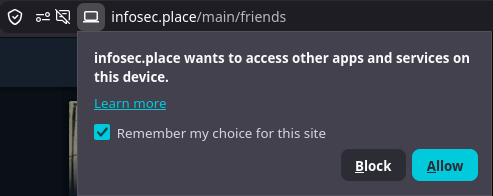
buheratorhttps://support.mozilla.org/en-US/kb/control-personal-device-local-network-permissions-firefox
At this point I'm not sure if it should be illegal for posts to contain references to localhost.
0
0
0
buherator
buheratorSo far I could get this out from some vibe coded event handler in dev tools:
"Local Network Access permission required: top-level site “https://infosec.place/”, initiator “https://infosec.place/”, attempting to access target “http://localhost:3000/assets/images/og-card.png” (127.0.0.1:3000) via http. Secure context: True"
1
0
1
 repeated
abadidea
0xabad1dea@infosec.exchangePostmortem of a little community hobby wiki struggling to survive an extinction-event-tier DDOS purely because they banned one guy for using Claude on the wiki https://blog.xkeeper.net/the-cutting-room-floor/tcrf-2026-ddos-postmortem/
5
8
0
repeated
Romain THOMAS
rh0main@infosec.exchangeRethinking Reverse Engineering for the AI Era:
https://www.romainthomas.fr/publication/26-rethinking-reverse-engineering-for-the-ai-era/
0
1
0
repeated
lcamtuf 
lcamtuf@infosec.exchange
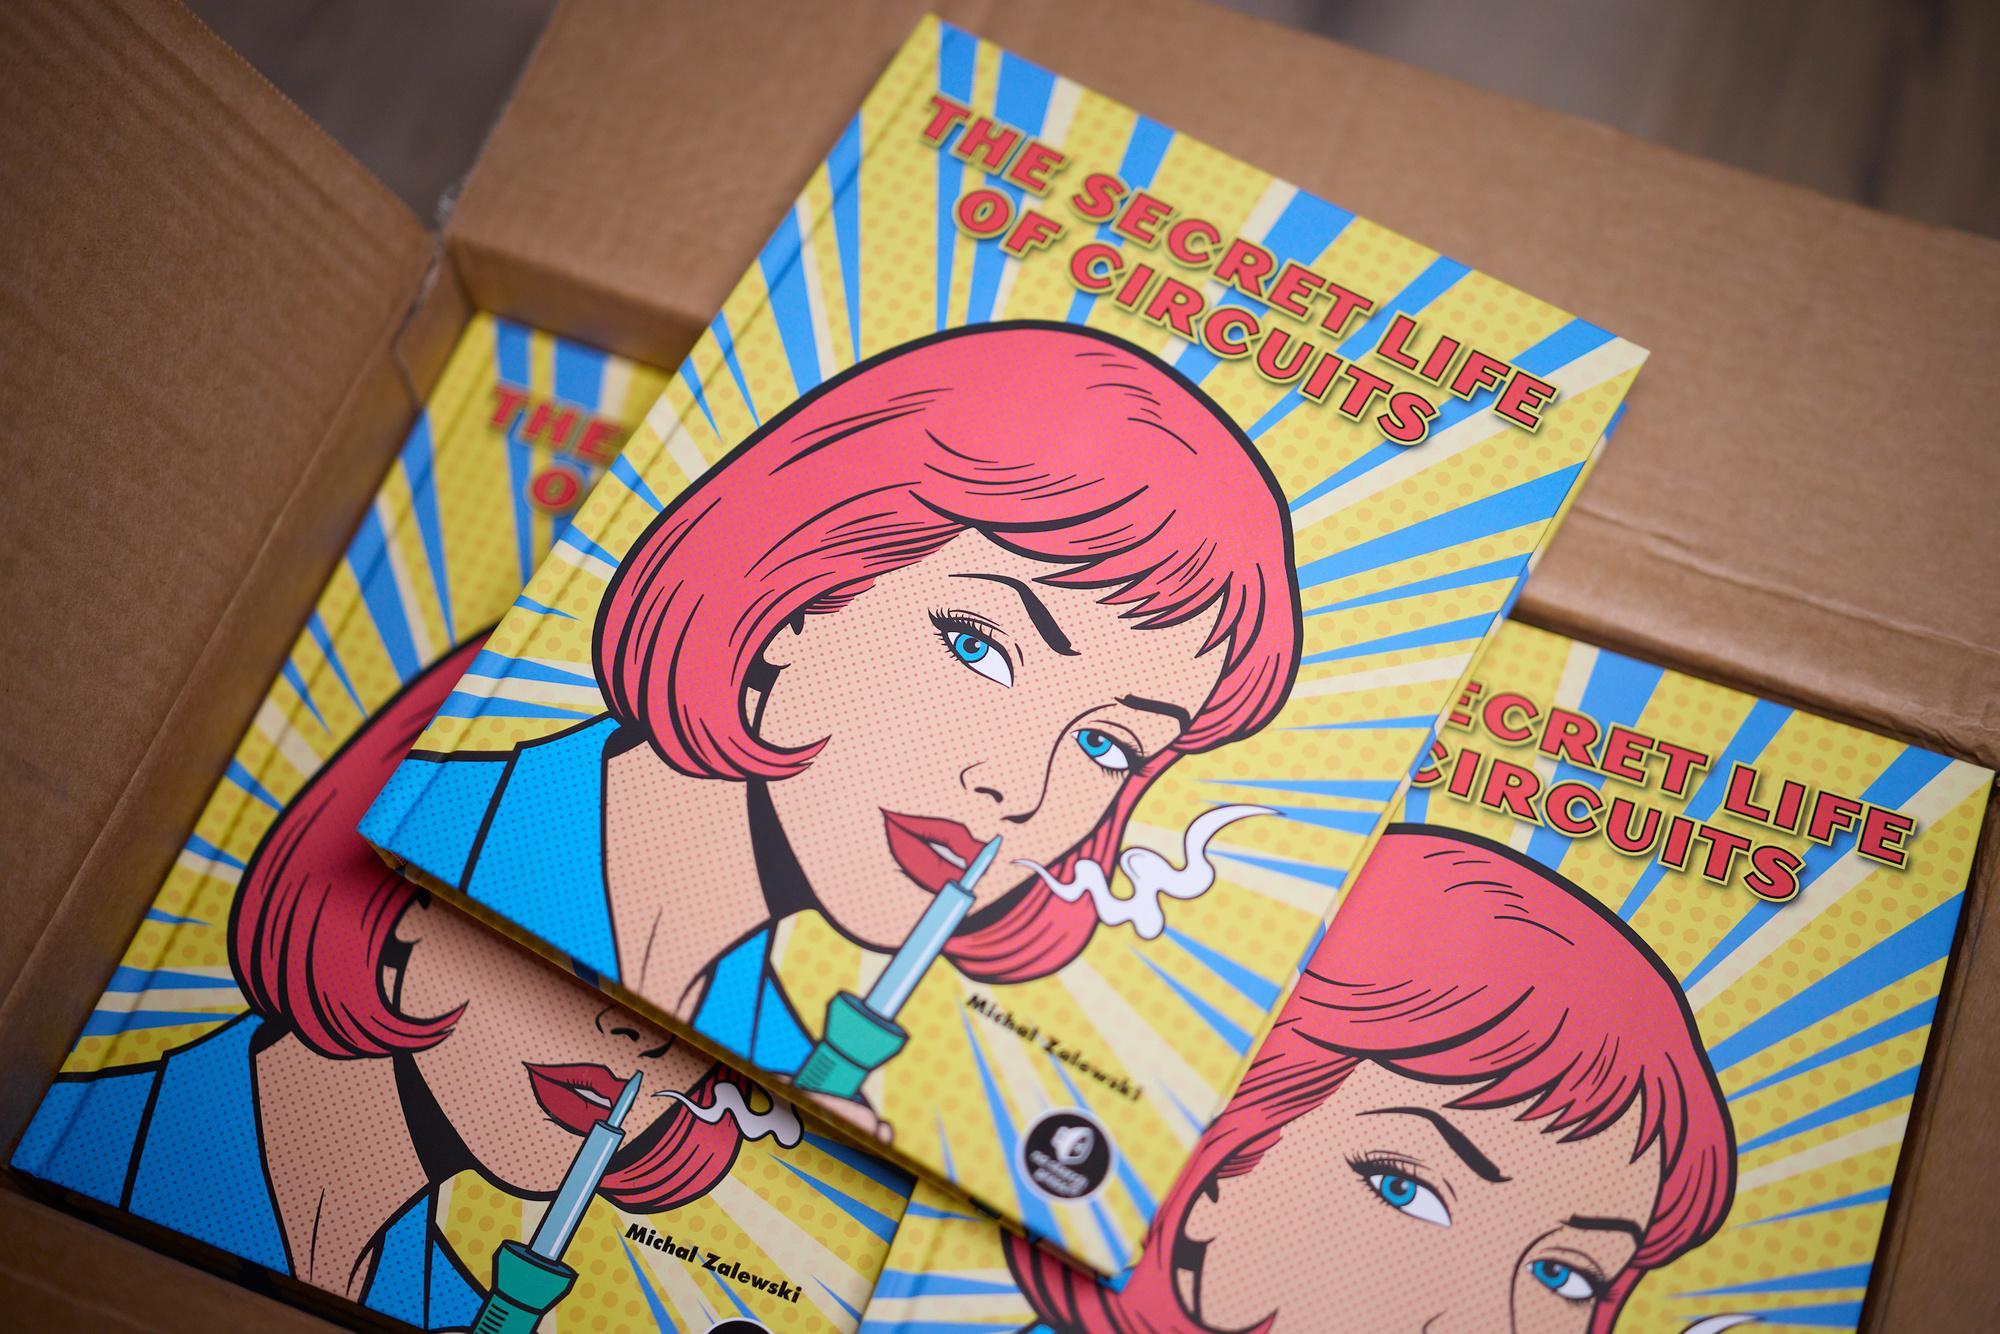
I tempted to do a small giveaway: reply with your best success *or* horror story related to electronics. I'll pick ~3 winners around EOW and send them a copy of The Secret Life of Circuits.
Plz no AI slop. Won't ship to Russia.
 9
3
0
repeated
InfoCon
InfoCon@defcon.socialWebseeds should be working again for https://infocon.org/ #InfoCon.
There was a problem with http range requests that should now be fixed. Please let us know if you see a difference!
 0
1
0
repeated
4Dgifts
4Dgifts@mastodon.socialAny pentesting firm behaving like OpenAI would be shutting down and counting lawsuits within a couple of months.
This new rera of Big AI doing cyber surely feels like the late 1980s/early 1990s of the Internet Wild West
1
2
0