Posts
4665Following
742Followers
1661
 repeated
lcamtuf 
lcamtuf@infosec.exchange

But I gotta hand it to AI labs that "WE MUST BE STOPPED AT ANY COST OR WE'RE GOING TO KILL YOU ALL" is one of the most original marketing pitches I've heard in my life
 4
11
 0
repeated
pancake 
pancake@infosec.exchange
The #Chiptune scene is growing back in Barcelona! https://filedn.eu/lhG9NwEl2KwykI9ctSv7Uqf/8bitnit/index.html
0
1
1
repeated
Jan Wildeboer 😷
jwildeboer@social.wildeboer.net
When I drive a car without a valid driver's license, proof of insurance or tag/license plate, I get stopped by the police, my car will be towed and I can either walk home or might end up in jail and face severe fines, a probation period and loss of my driver's license.
When Microsoft runs 45 gas turbines without a state permit, they get 45 days to fix it and a $1.07M fine (which is petty cash for an operation this size) and don't even have to power down the turbines.
3
18
0
repeated
Dark Web Informer 
DarkWebInformer@infosec.exchange
🚨 Companies are being urged to shut down their NetScaler instances immediately due to multiple unpatched Citrix NetScaler RCE vulnerabilities.
Source: https://x.com/watchtowrcyber/status/2103891689857228803
0
4
0
buherator
buheratorFrom my professional experience I know this means the network is probably fucked. It was.
But why is it so hard to put `error("network is fucked");` in #systemd?
https://blog.netherlabs.nl/articles/2006/09/08/the-perfect-error-message
0
0
1
repeated
raptor
raptor@infosec.exchangeAn official #MCP for #IDA was released by @HexRaysSA
https://hex-rays.com/blog/hex-rays-ida-mcp-server
0
3
0
buherator
buheratorAt first I find this a pretty good use case for language models.
3
0
2
repeated

buherator
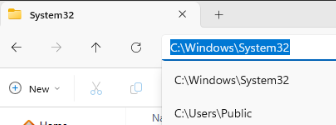
buheratorBy first pressing the down arrow you remove the selection (which you didn't put there) from the address bar text. The two downs are needed to reach C:\Users\Public.
"2 or 3" would be also acceptable, because if you don't just click the address bar, but start to type in it, there is no selection to remove.
https://infosec.place/objects/85dfac07-d1d6-412b-832c-897be5be860b
 0
0
1
repeated
OpenSecurityTraining2
OpenSecurityTraining2@infosec.exchangeWe have posted the YouTube playlist for Trusted Computing 1103: Advanced TPM Usage by Dimi Tomov in partnership with the TCG. Now anyone wishing to download the videos for offline viewing can find all their URLs here:
https://www.youtube.com/playlist?list=PLUFkSN0XLZ-l-hmC2f0f0WHh5tm76LyTj
But as always the best experience is at the full class at https://ost2.fyi/TC1103
0
2
0
repeated
Wladimir Palant
WPalant@infosec.exchangeIt seems that Avast managed to settle the lawsuits related to their data abuse in both US and UK. While in the former they agreed to pay a fairly moderate fine, UK let them off the hook even easier. They are offering two years of free software to eligible UK users which is, quite frankly, a joke. It costs Avast exactly nothing, it allows them to email past users on a legal basis and gives them a chance to win them back. Really, who agreed to that?
0
3
0
repeated
Tim (Wadhwa-)Brown 
timb_machine@infosec.exchange
Interesting Git repos of the week:
Strategy:
* https://github.com/SoShinySoChrome/human-incident-response-framework - tackling the human side of IR
Threats:
* https://github.com/Mickinthemiddle/CLOAK - deception techniques used by operators
Detection:
* https://github.com/Chick3nHawk01/Open_Source-CTI-Tooling - open source CTI tooling
Bugs:
* https://github.com/suce0155/CVE-2026-32996 - a backup route for LPE
Exploitation:
* https://github.com/cloudflare/security-audit-skill - more skills for your 🤖
* https://github.com/almounah/silph - another tool to steal your memories
* https://github.com/TheZeroSlave/WPE - like Burp but for non-HTTP Windows traffic (HT @Ichinin for the reminder)
* https://github.com/interference-security/echomirage - if you remember shade/DOA... someone has saved a copy of Echo Mirage, another Windows MITM testing tool
* https://github.com/Mafifrizi/ARES - someone has been going through adding my AD attacks (credited nicely :)) on Linux to its repertoire
* https://github.com/IoTS-P/Akiba - batch processing Ghidra
* https://github.com/vulncheck-oss/initial-access-community - some nice ideas on initial access from @albinolobster and friends
Hard hacks:
* https://github.com/GlasgowEmbedded/glasgow - it's always nice in Glasgow with @whitequark
* https://github.com/xiaobor123/vuls-find-VxWorks - VxWorks until it doesn't
* https://github.com/xiaobor123/vul-finds - more cute bugs
Data:
* https://github.com/cisco-ai-defense/aibom - AI usage needs to be transparent... and if not, well, some of us will be looking for it in any event 🤖
Cryptography:
* https://github.com/nationwide-group-oss/cryptoptic - time to start taking PQC seriously
Development:
* https://github.com/ItzLevvie/dind - HT to @GossiTheDog for pointing it out, but run Windows inside of GitHub
Nerd:
* https://github.com/sure-fire/derbypi - some neat extensions for Pis from @surefire
0
4
0
repeated
Rebane
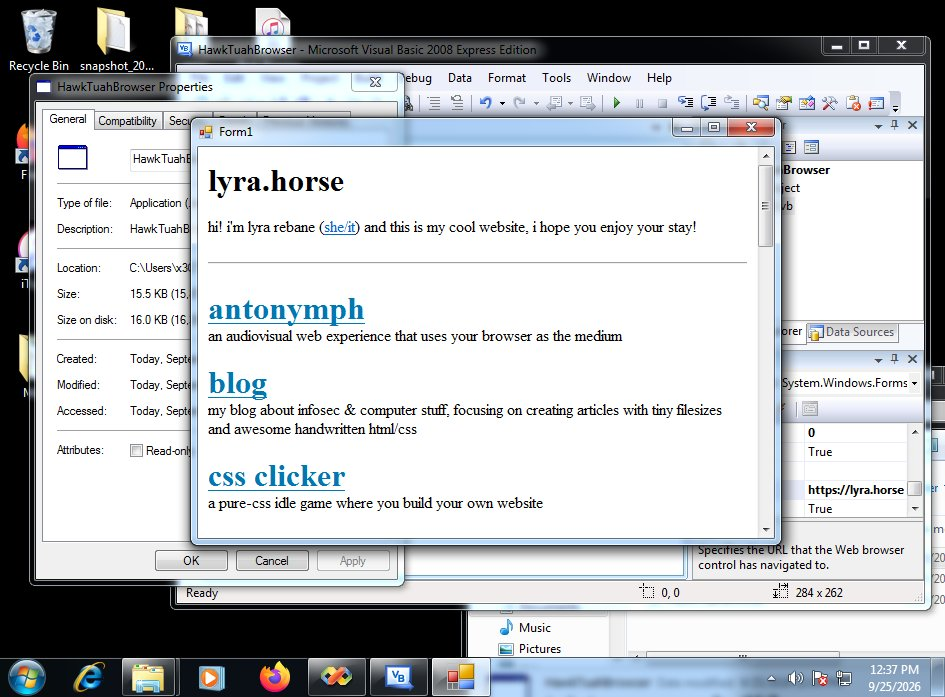
rebane2001@infosec.exchangeIntroducing 𝙷𝚊𝚠𝚔𝚃𝚞𝚊𝚑𝙱𝚛𝚘𝚠𝚜𝚎𝚛.𝚎𝚡𝚎
- 15 KB native web browser
- 6 MB of RAM for the host
- 0 lines of Visual Basic (no C# cuz idk how to write it)
- no URL bar because surfing through 88x31s is more fun
- title bar kept cuz then u can close it and minimize buttons
 3
3
0
buherator
buheratorWhen booking for events it *always* takes *days* to get from registering for an event and getting there to show your QR or whatever. And while an attacker who hijacks your session has 0 benefit from accessing it for a prolonged time, somehow #security finds it crucial that users are auto logged-out after 30mins.
It would take just a *tiny* bit of thinking to avoid making things worse for everyone.
[1] https://wstg.owasp.org/latest/4-Web_Application_Security_Testing/06-Session_Management/07-Session_Timeout/ (congrats to #OWASP for breaking all your indexed links in search engines, also very helpful!)
0
1
3
repeated
Kevin Beaumont
GossiTheDog@cyberplace.socialBBC News has 4 YouTube videos up in the past day about OpenAI hacking “governments”, with approaching a million views.
If you want to know the technical details of this elite frontier AI hacking - these are examples of the actual OpenAI agent requests.
It’s really dumb shit. The story here is OpenAI are utterly incompetent at cybersecurity, as are their victims.
 5
5
0
buherator
buherator#Firefox
RE: https://infosec.place/objects/c55e1bcb-86a9-4d16-b9fb-83dccaeb4dad
2
2
4
repeated
 repeated
David Revoy
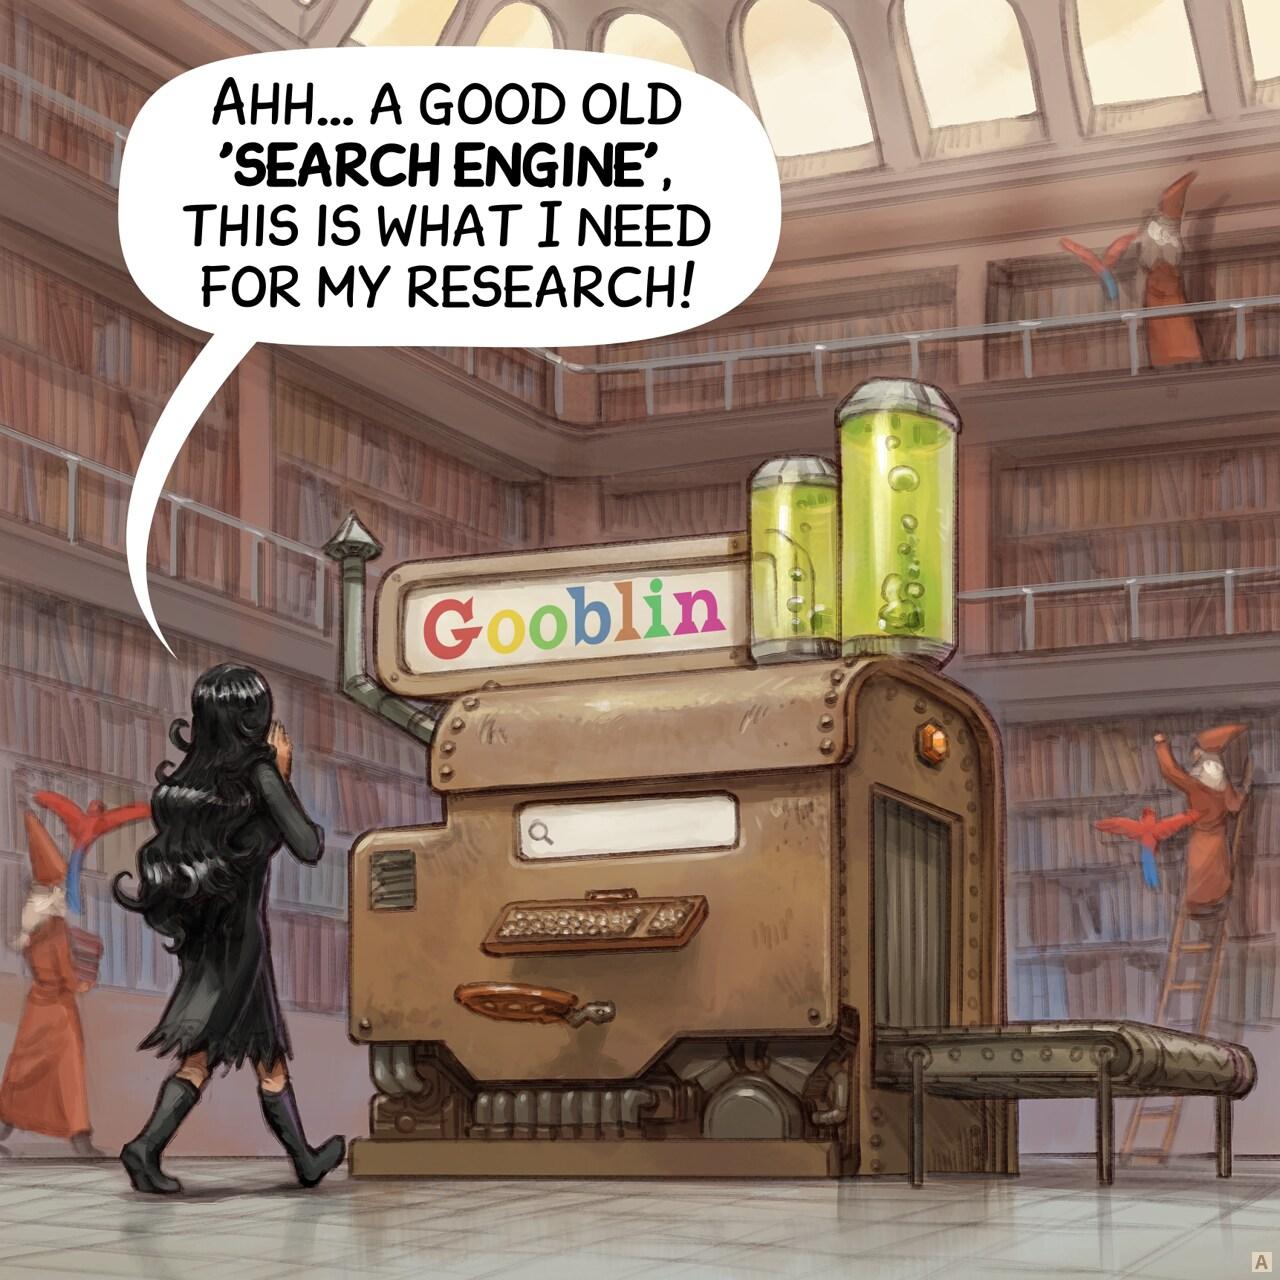
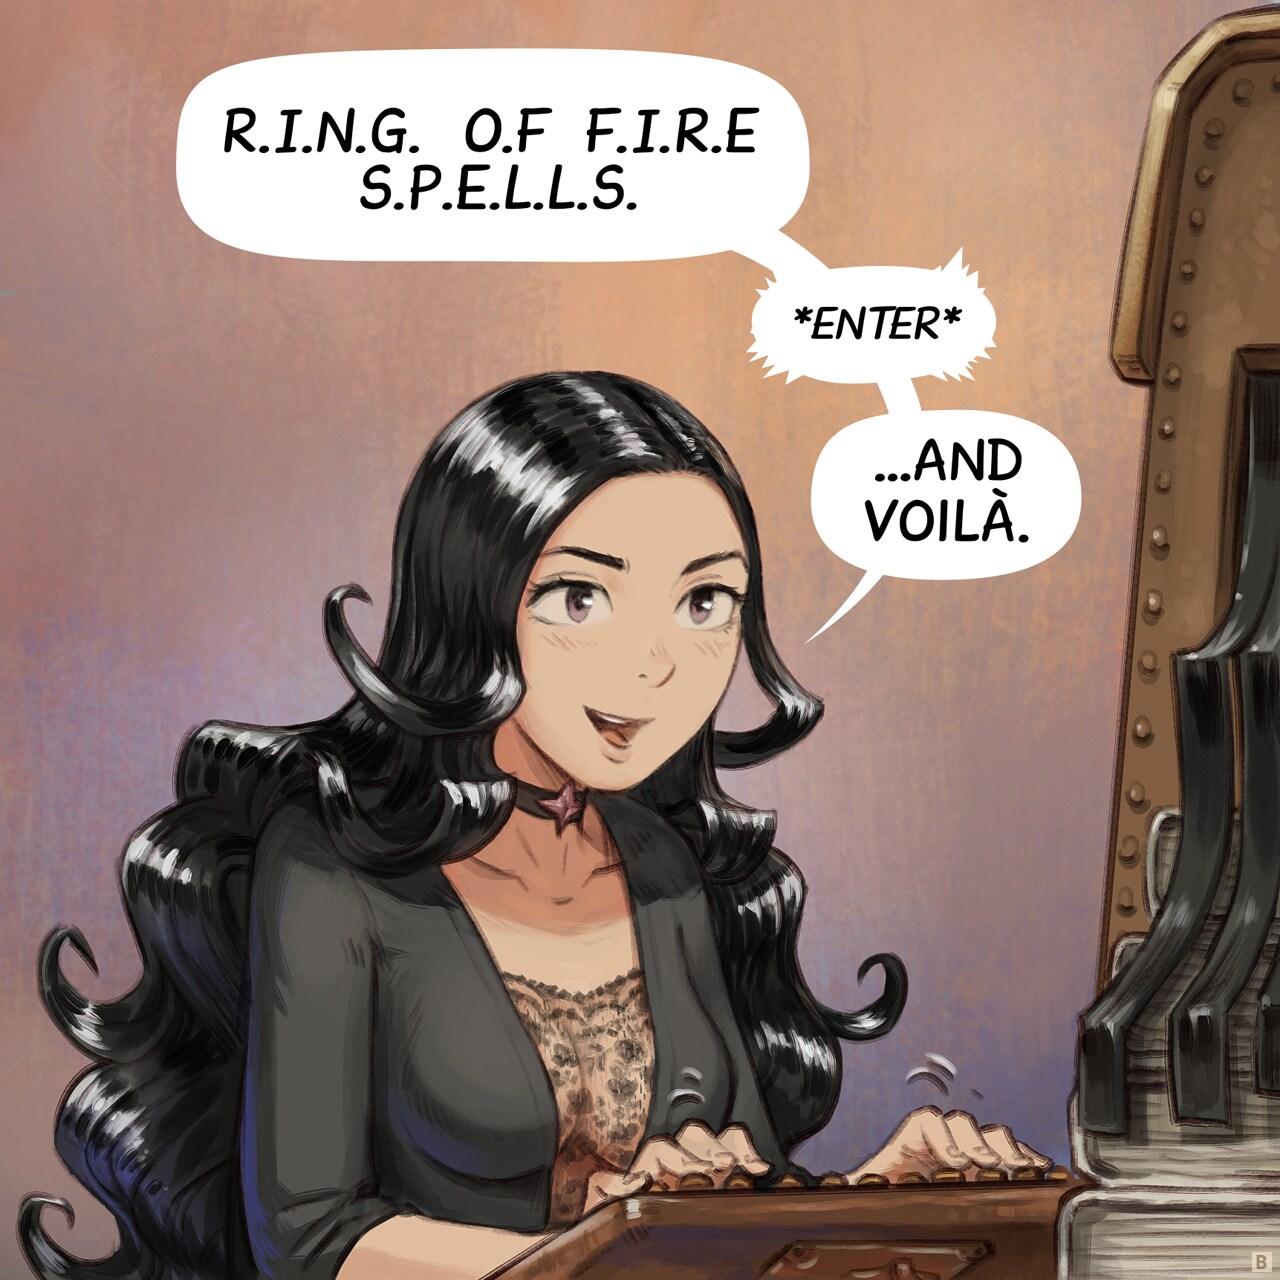
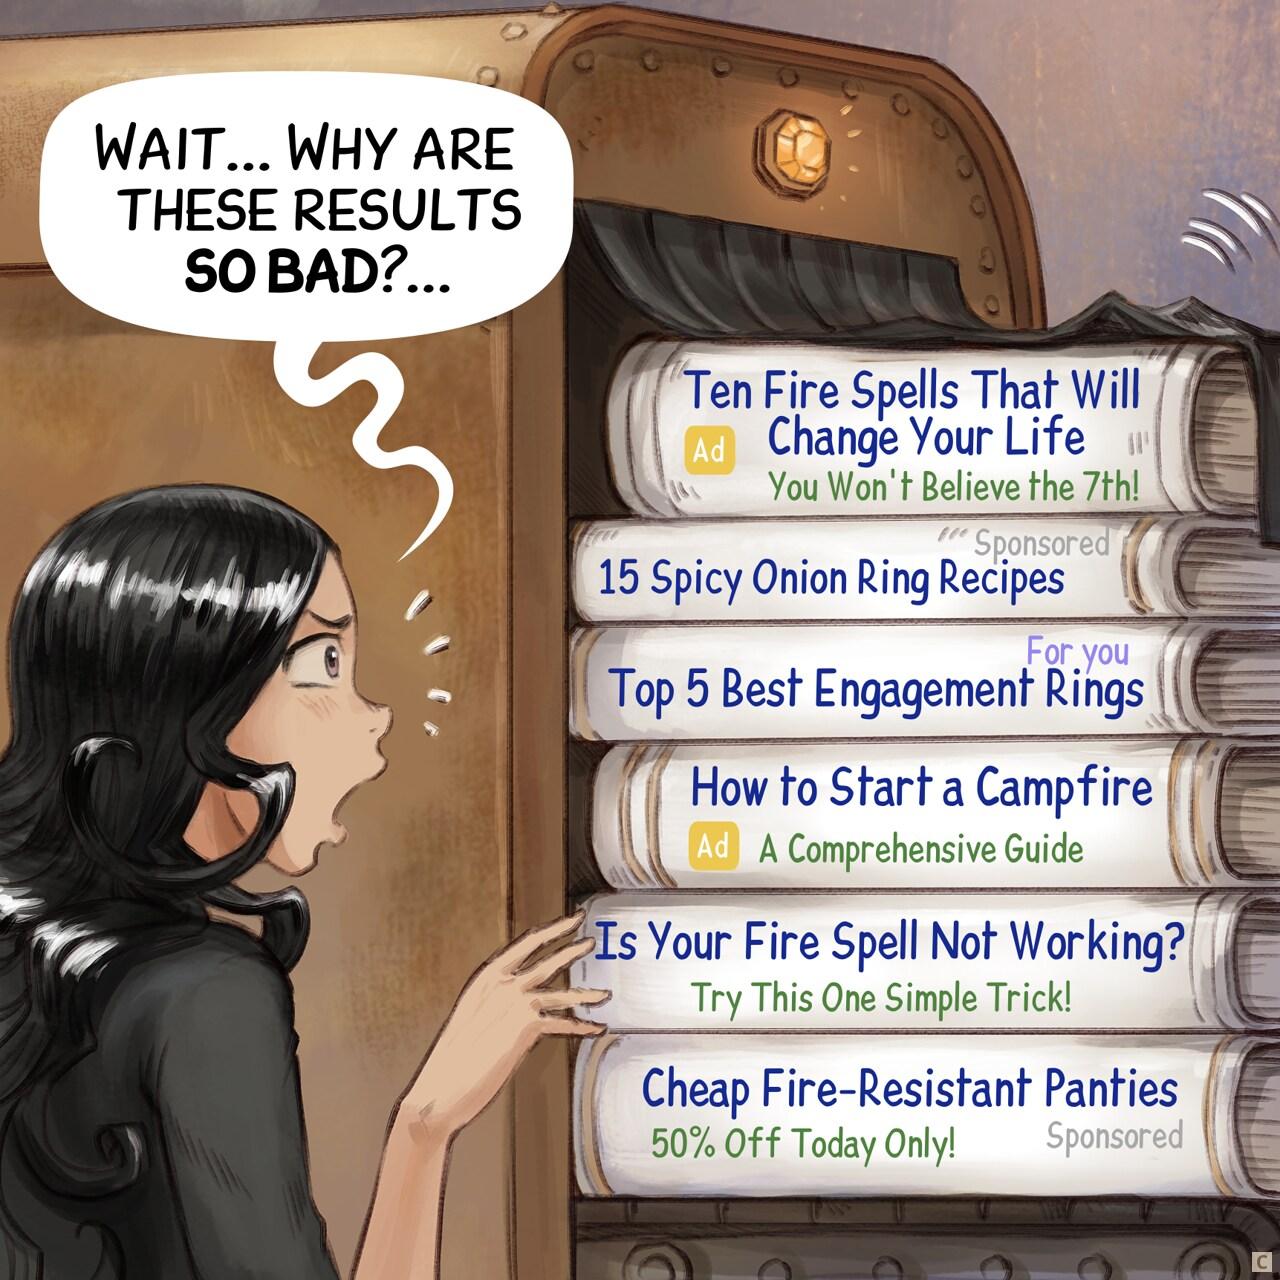
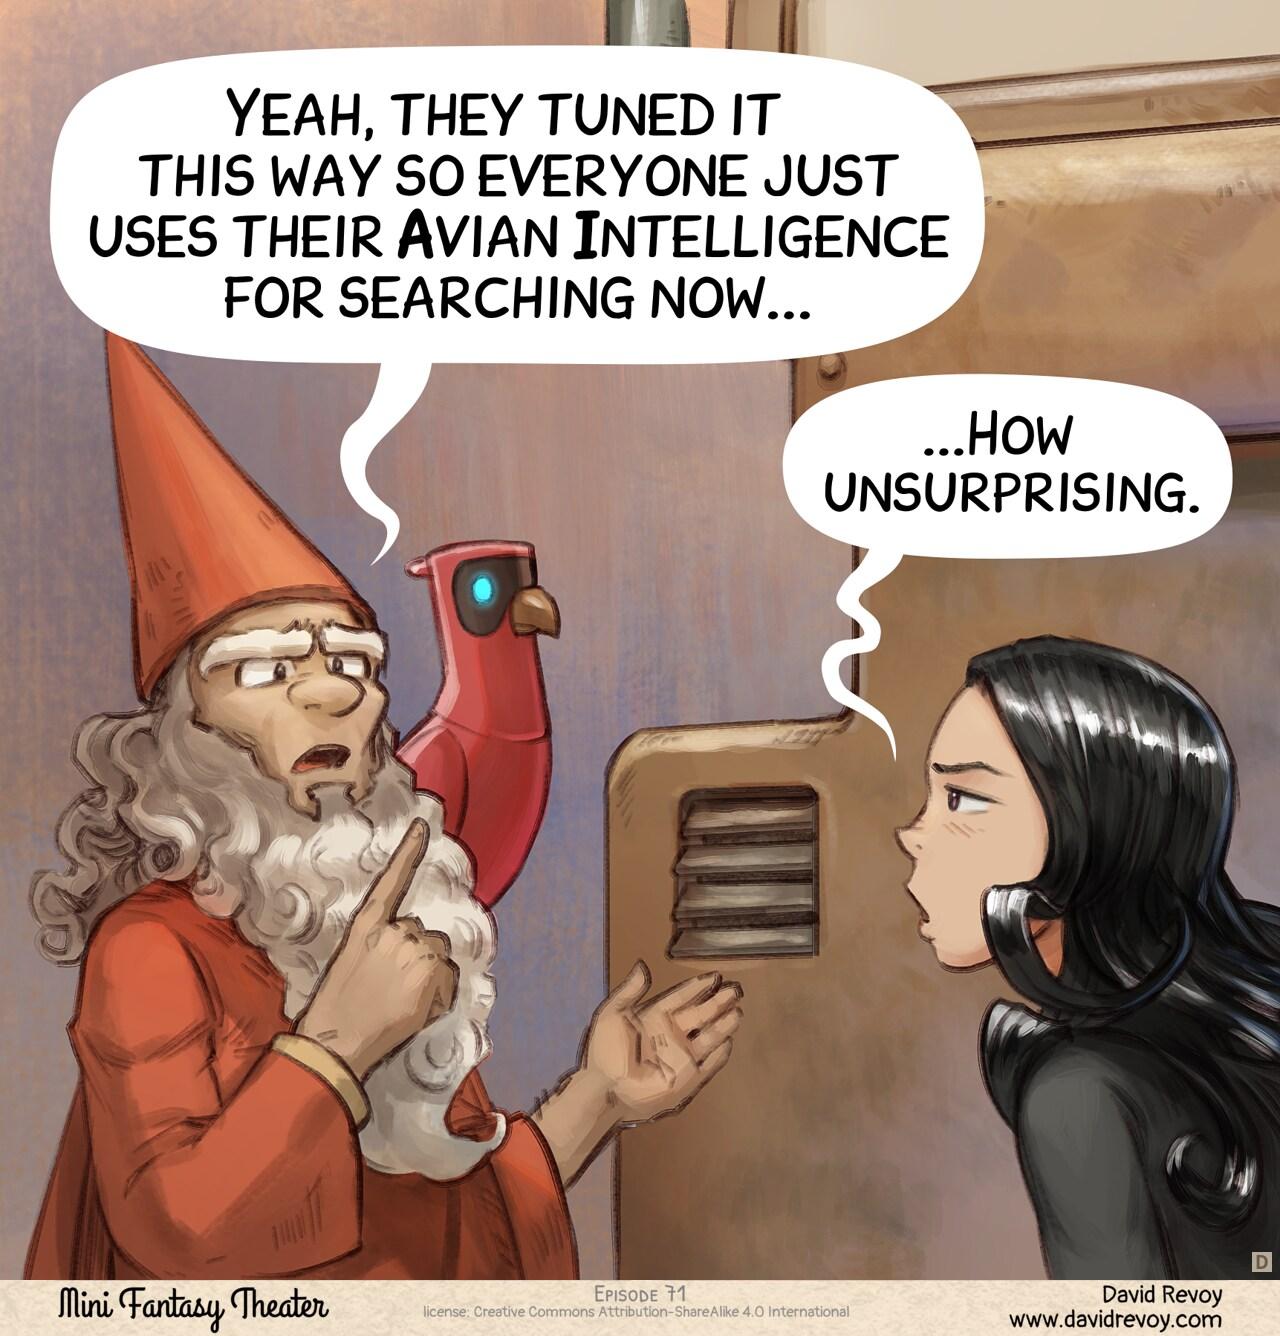
davidrevoy@framapiaf.orgThe Degraded Search Engine
Bonus speedpaint: https://www.peppercarrot.com/en/miniFantasyTheater/071.html#bonus
#webcomic #krita #miniFantasyTheater
 27
33
4