Posts
4557Following
741Followers
1654
 repeated
CFG Bot 🤖
cfgbot@mastodon.social
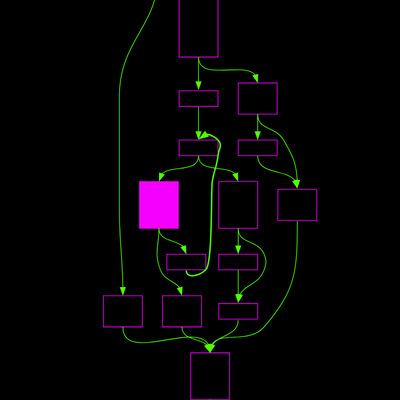
Project: microsoft/TypeScript https://github.com/microsoft/TypeScript
File: src/compiler/utilities.ts:4463 https://github.com/microsoft/TypeScript/blob/cbac1ddfc73ca3b9d8741c1b51b74663a0f24695/src/compiler/utilities.ts#L4463
function canHaveJSDoc(node: Node): node is HasJSDoc
SVG:
dark https://tmr232.github.io/function-graph-overview/render/?github=https%3A%2F%2Fgithub.com%2Fmicrosoft%2FTypeScript%2Fblob%2Fcbac1ddfc73ca3b9d8741c1b51b74663a0f24695%2Fsrc%2Fcompiler%2Futilities.ts%23L4463&colors=dark
light https://tmr232.github.io/function-graph-overview/render/?github=https%3A%2F%2Fgithub.com%2Fmicrosoft%2FTypeScript%2Fblob%2Fcbac1ddfc73ca3b9d8741c1b51b74663a0f24695%2Fsrc%2Fcompiler%2Futilities.ts%23L4463&colors=light
 0
1
 0
repeated

 repeated
screaminggoat
screaminggoat@infosec.exchangeSonicWall exploited zero-day: SMA1000 Pre-Authentication Remote Command Execution Vulnerability
CVE-2025-23006 (9.8 critical) Pre-authentication deserialization of untrusted data vulnerability has been identified in the SMA1000 Appliance Management Console (AMC) and Central Management Console (CMC), which in specific conditions could potentially enable a remote unauthenticated attacker to execute arbitrary OS commands.
IMPORTANT: SonicWall PSIRT has been notified of possible active exploitation of the referenced vulnerability by threat actors
cc: @goatyell @cR0w @GossiTheDog @briankrebs
#zeroday #CVE_2025_23006 #sonicwall #vulnerability #CVE #infosec #cybersecurity #eitw #activeexploitation
4
7
0
repeated
 repeated
CFG Bot 🤖
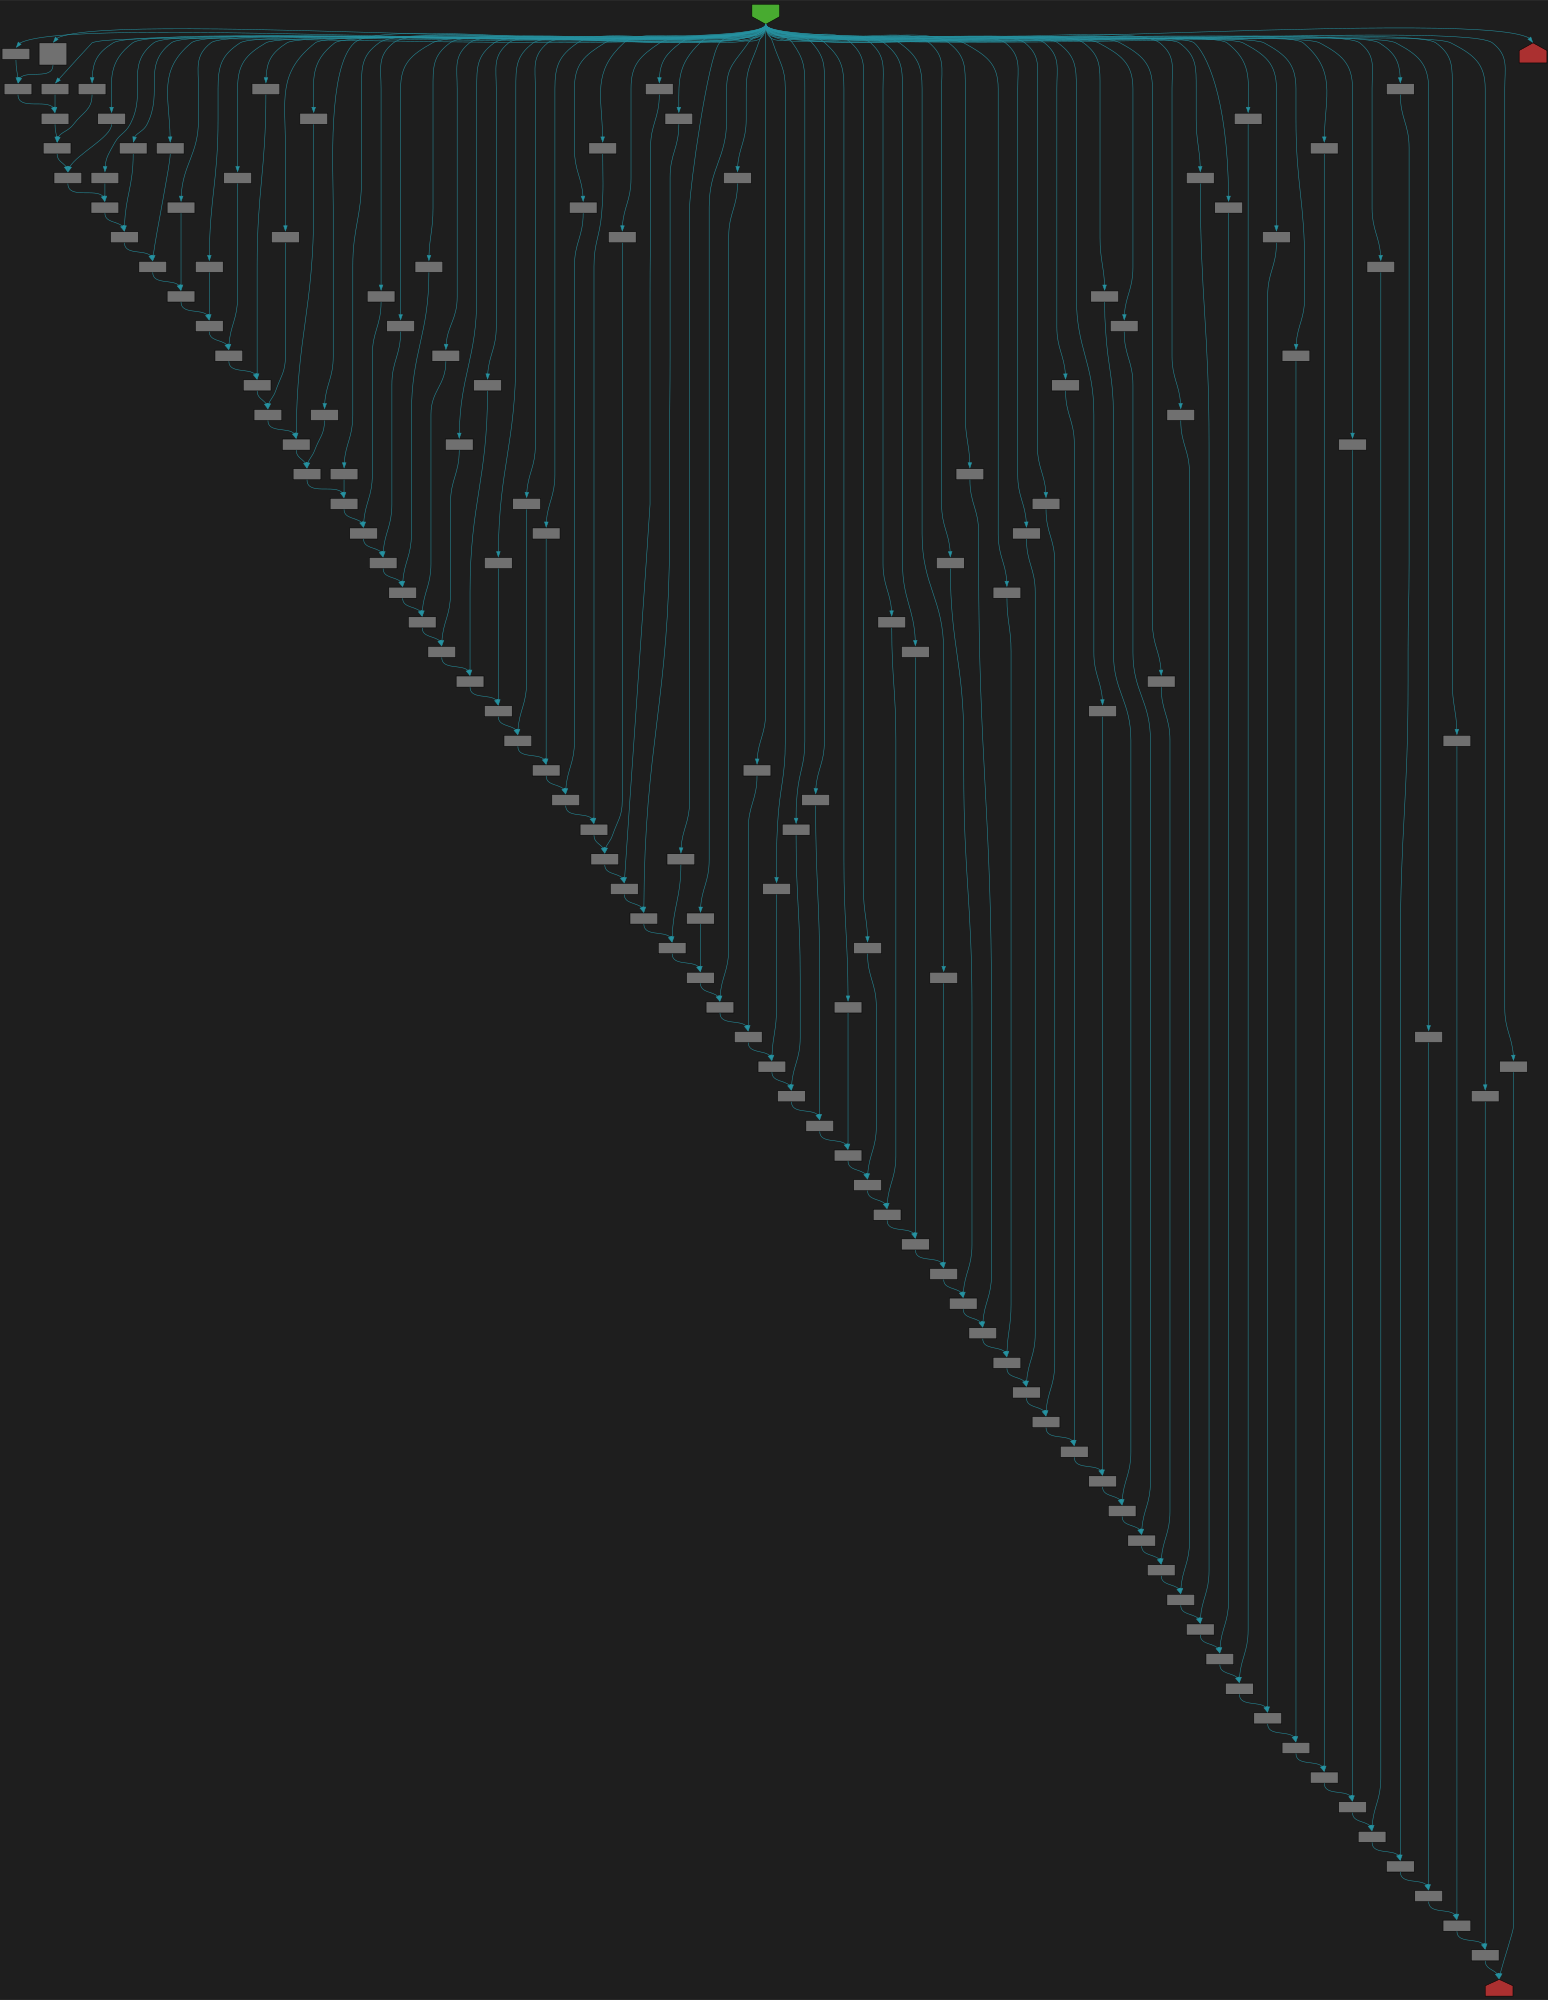
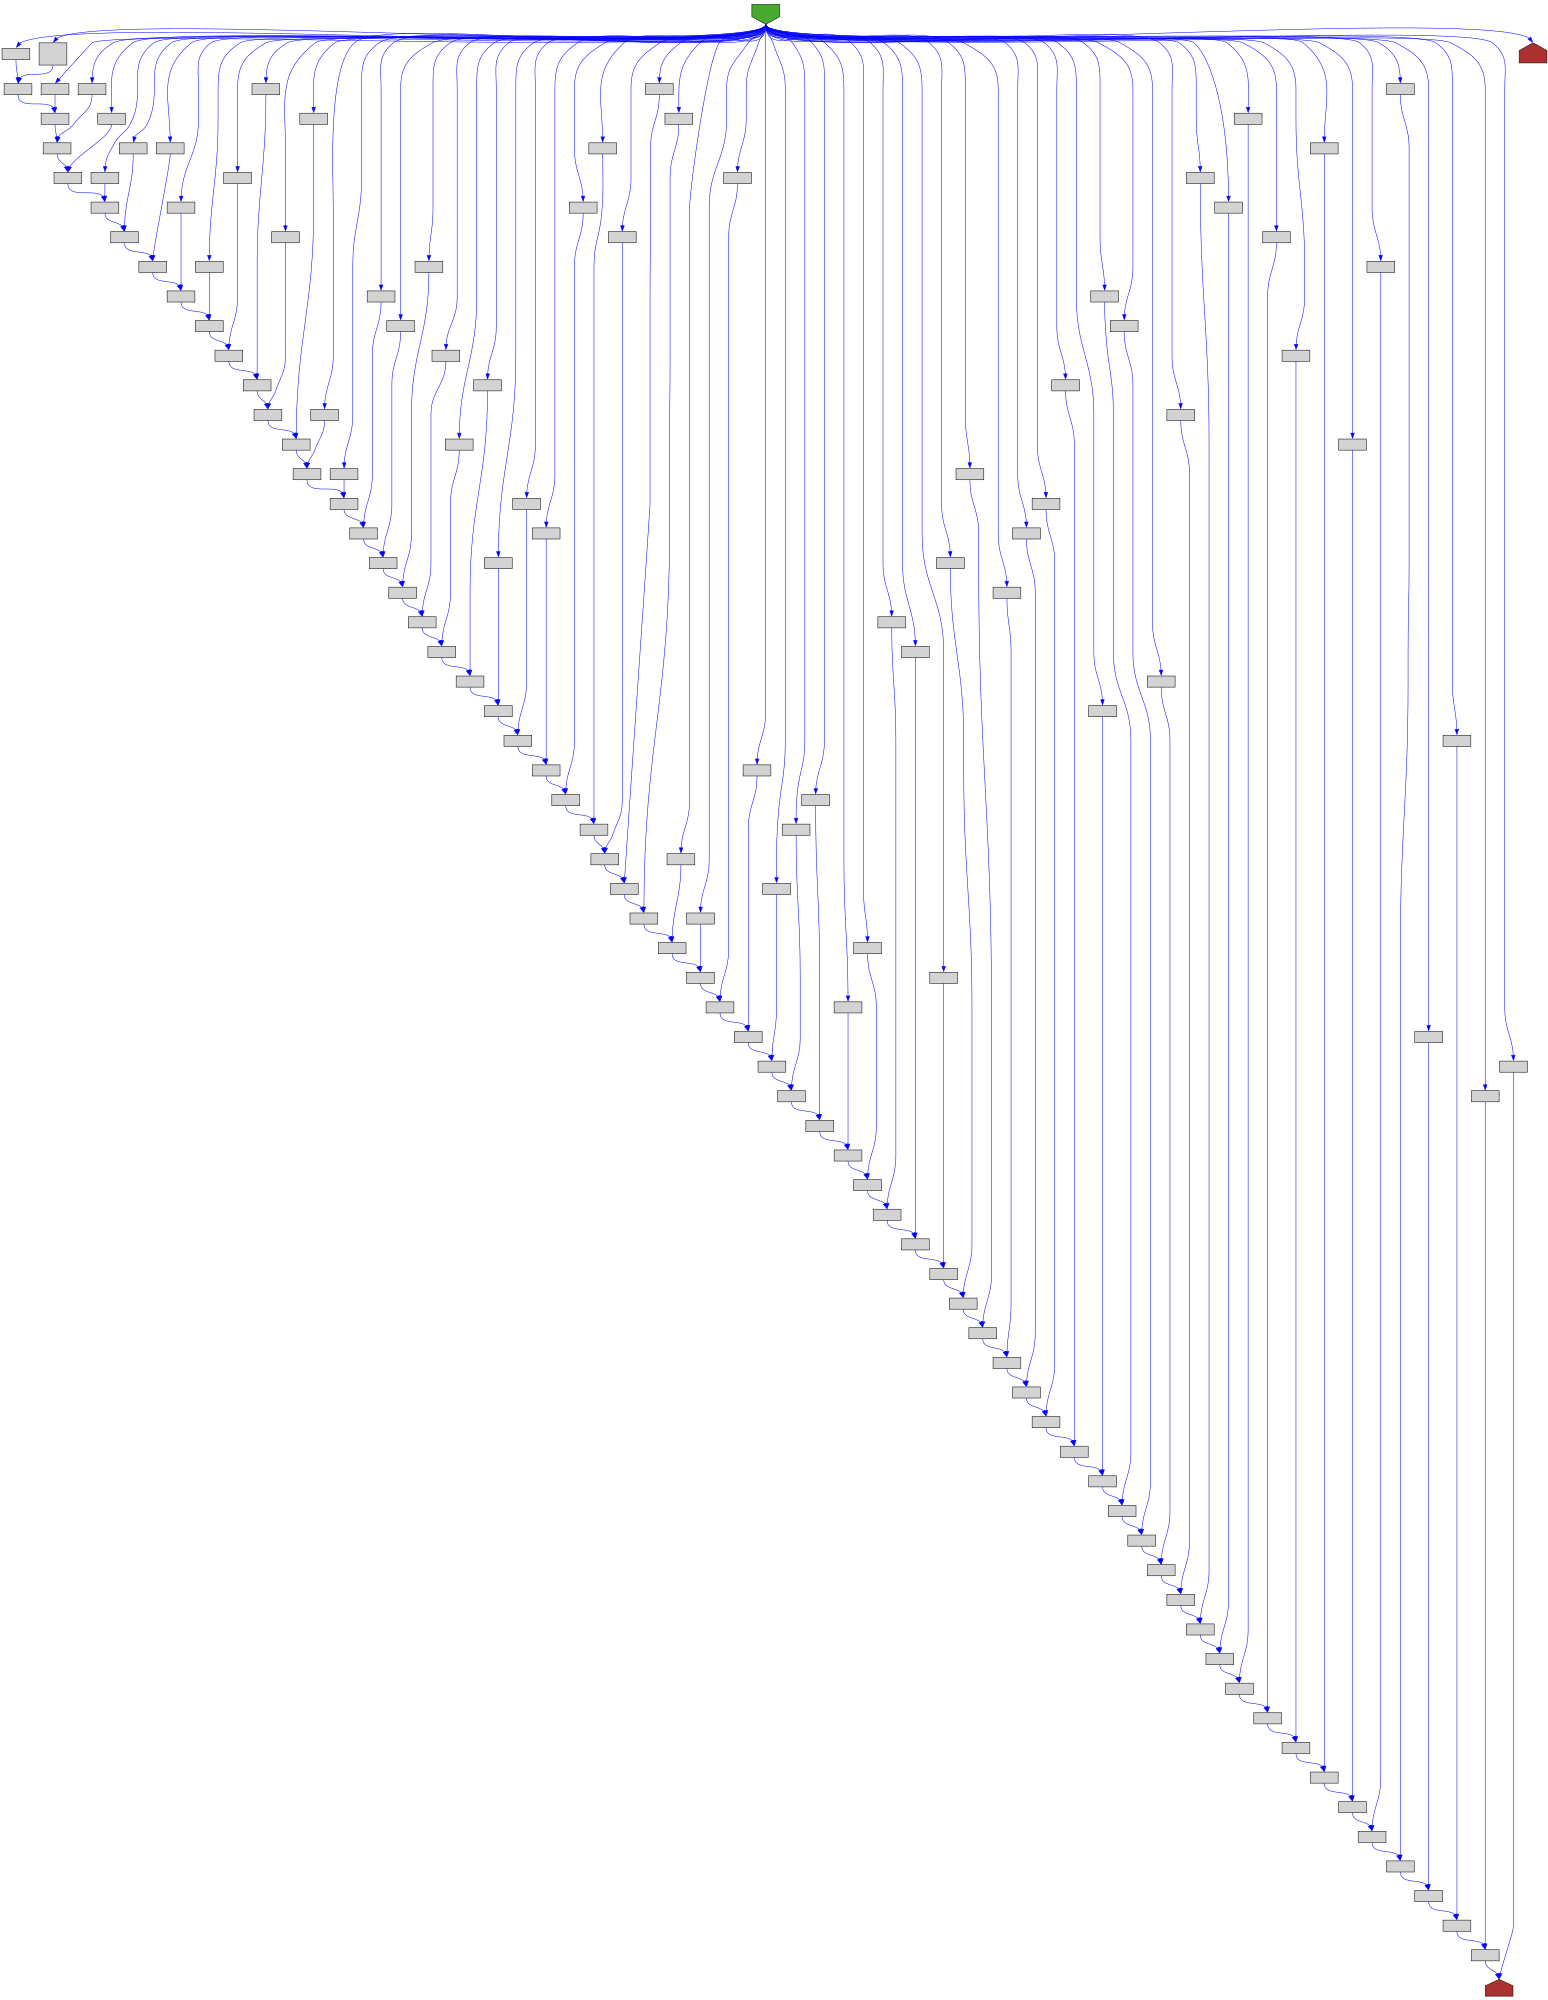
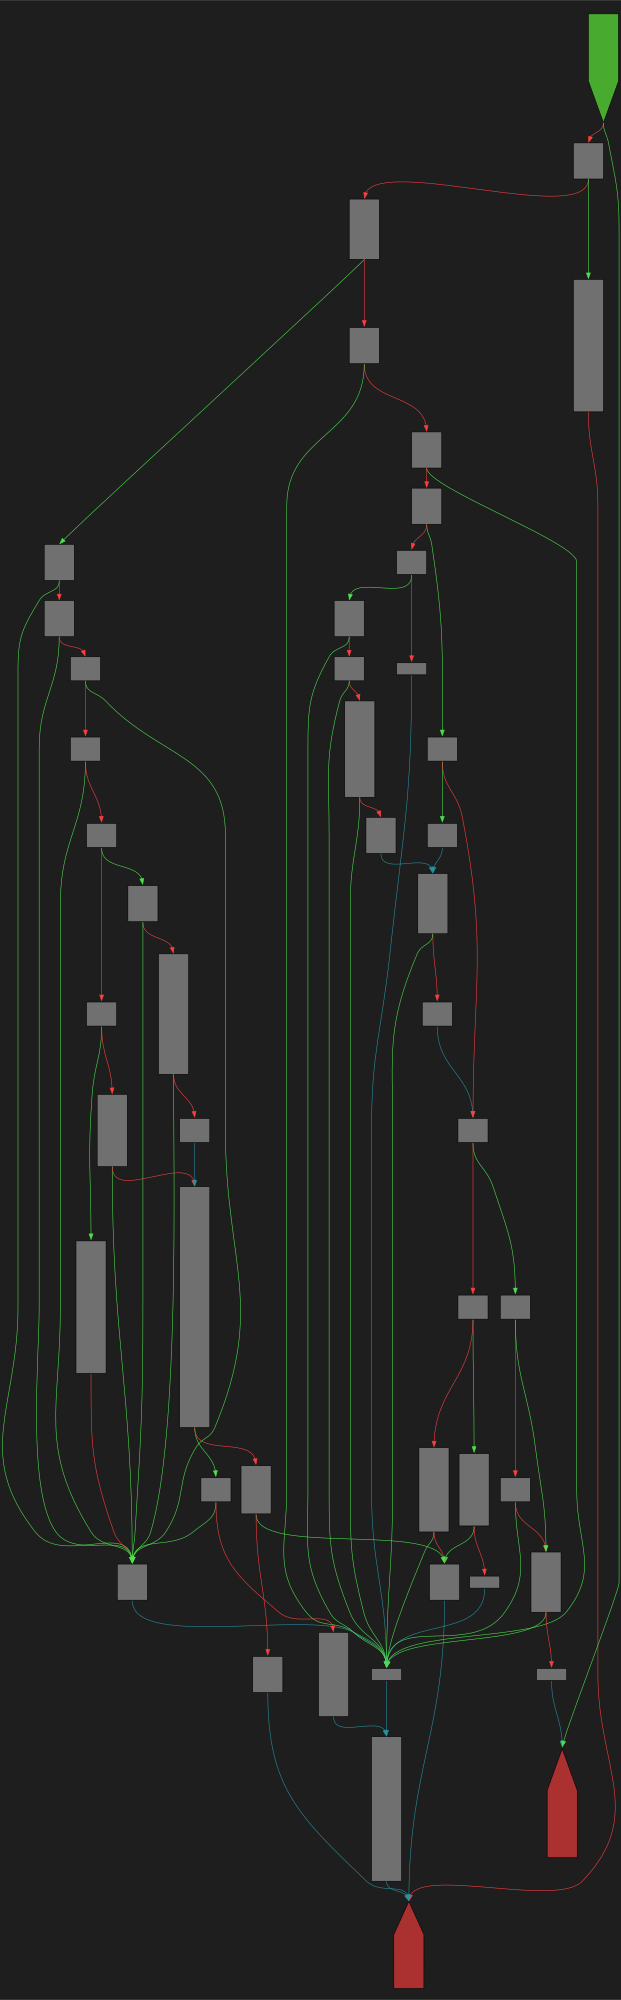
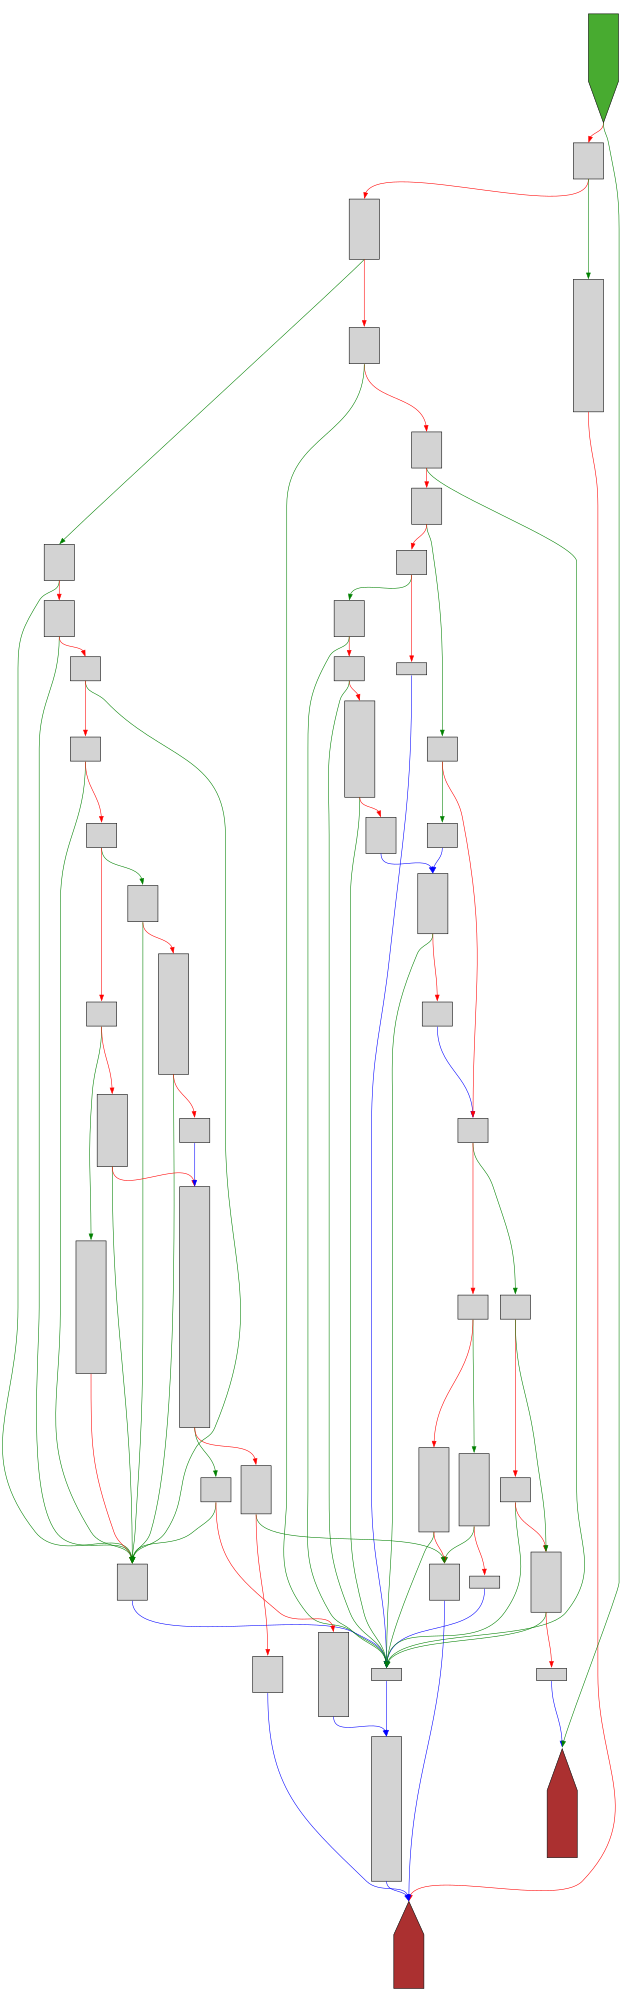
cfgbot@mastodon.socialProject: openssl-static-gcc-dwarf 3.4.0
File: openssl
Address: 007060c0
ossl_gcm_stream_update
SVG:
dark https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fopenssl-static-gcc-dwarf%2F007060c0.json&colors=dark
light https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fopenssl-static-gcc-dwarf%2F007060c0.json&colors=light
 0
1
0
repeated
screaminggoat
screaminggoat@infosec.exchangeGoogle Chrome security advisory: Stable Channel Update for Desktop
New version 132.0.6834.110/111 for Windows, Mac and 132.0.6834.110 for Linux includes 3 security fixes, 2 were externally reported. CVE-2025-0611 (high severity) Object corruption in V8 and CVE-2025-0612 (high) Out of bounds memory access in V8. No mention of exploitation.
#google #chrome #chromium #vulnerability #cve #infosec #cybersecurity
0
2
0
repeated
comex
comex@mas.to“Clang will now more aggressively use undefined behavior on pointer addition overflow for optimization purposes.” https://github.com/llvm/llvm-project/commit/c2979c58d49b
A whole lot of non-exploitable bugs may become exploitable pretty soon.
2
7
0
repeated

Taggart 
mttaggart@infosec.exchange
Here's a video overview of Venture, the cross-platform Windows Event Viewer. Version 0.2.0 now has the ability to join multiple .evtx files into a single view!
https://www.youtube.com/watch?v=LSobpAWwNV8
Grab Venture here: https://github.com/mttaggart/venture/releases/
0
3
0
repeated
"CrowdStrike, Fortinet Get Price Target Hikes Amid Booming Cybersecurity Market"
Clearly the Clownstrike "incident" doom is already behind, and Fortinet product security is irrelevant to stock price :X
0
1
0
repeated


 repeated
screaminggoat
screaminggoat@infosec.exchangeCisco Zero-Day: ClamAV OLE2 File Format Decryption Denial of Service Vulnerability
CVE-2025-20128 (5.3 medium) A vulnerability in the Object Linking and Embedding 2 (OLE2) decryption routine of ClamAV could allow an unauthenticated, remote attacker to cause a denial of service (DoS) condition on an affected device. This vulnerability is due to an integer underflow in a bounds check that allows for a heap buffer overflow read.
The Cisco PSIRT is aware that proof-of-concept exploit code is available for the vulnerabilities that are described in this advisory.
The Cisco PSIRT is not aware of any malicious use of the vulnerabilities that are described in this advisory.
Two more Cisco security advisories:
- Cisco Meeting Management REST API Privilege Escalation Vulnerability CVE-2025-20156 (9.9 critical)
- Cisco BroadWorks SIP Denial of Service Vulnerability CVE-2025-20165 (7.5 high)
These two do not mention proof of concept or exploitation.
1
2
0
repeated

BleepingComputer
BleepingComputer@infosec.exchangeSouth Korean VPN provider IPany was breached in a supply chain attack by the "PlushDaemon" China-aligned hacking group, who compromised the company's VPN installer to deploy the custom 'SlowStepper' malware.
1
3
0
repeated
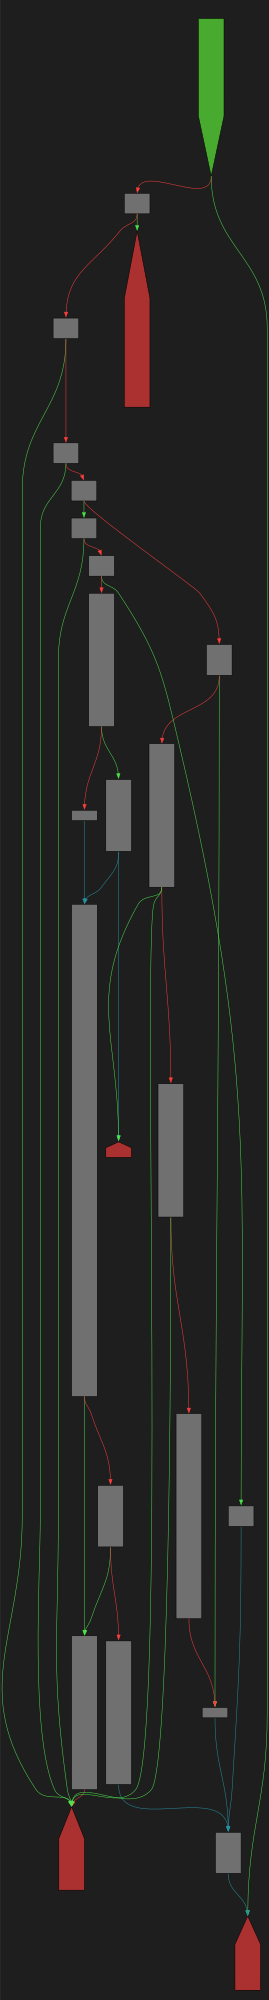
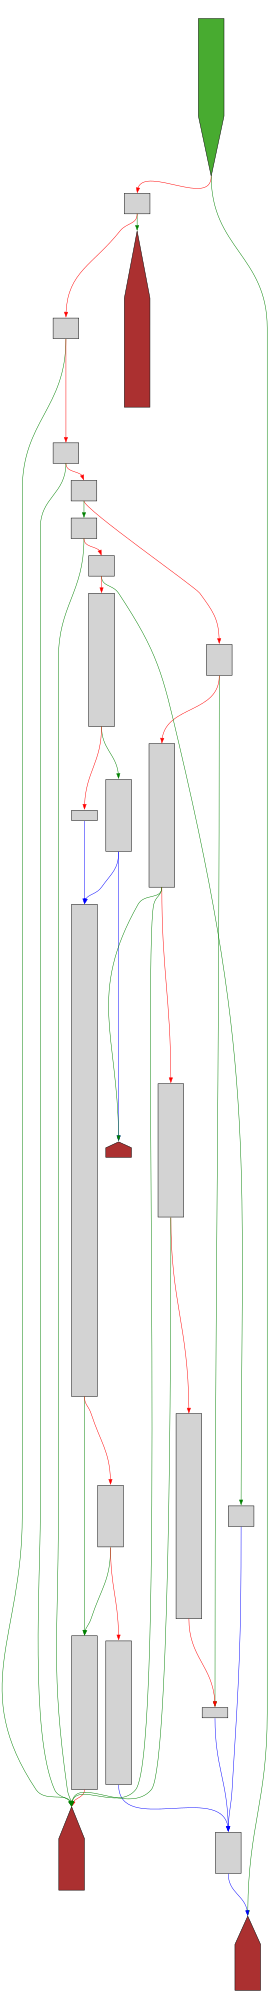
CFG Bot 🤖
cfgbot@mastodon.socialProject: openssl-static-gcc-dwarf 3.4.0
File: openssl
Address: 006a55e0
tdes_wrap_cipher
SVG:
dark https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fopenssl-static-gcc-dwarf%2F006a55e0.json&colors=dark
light https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fopenssl-static-gcc-dwarf%2F006a55e0.json&colors=light
 0
1
0
buherator
buheratorhttps://www.drawio.com/about
These people are pretty cool!
0
3
5
repeated
buherator
buheratorI'll reshare the original instead: https://blog.silentsignal.eu/2025/01/21/ibm-acs-password-dump/
(If you want to pull your hair out: https://cybersecuritynews[.]com/ibm-i-access-client-vulnerability-exposed/)
0
0
3
repeated

Anderson Nascimento
andersonc0d3@infosec.exchangeCVE-2025-0395: Buffer overflow in the GNU C Library's assert()
0
3
0
repeated
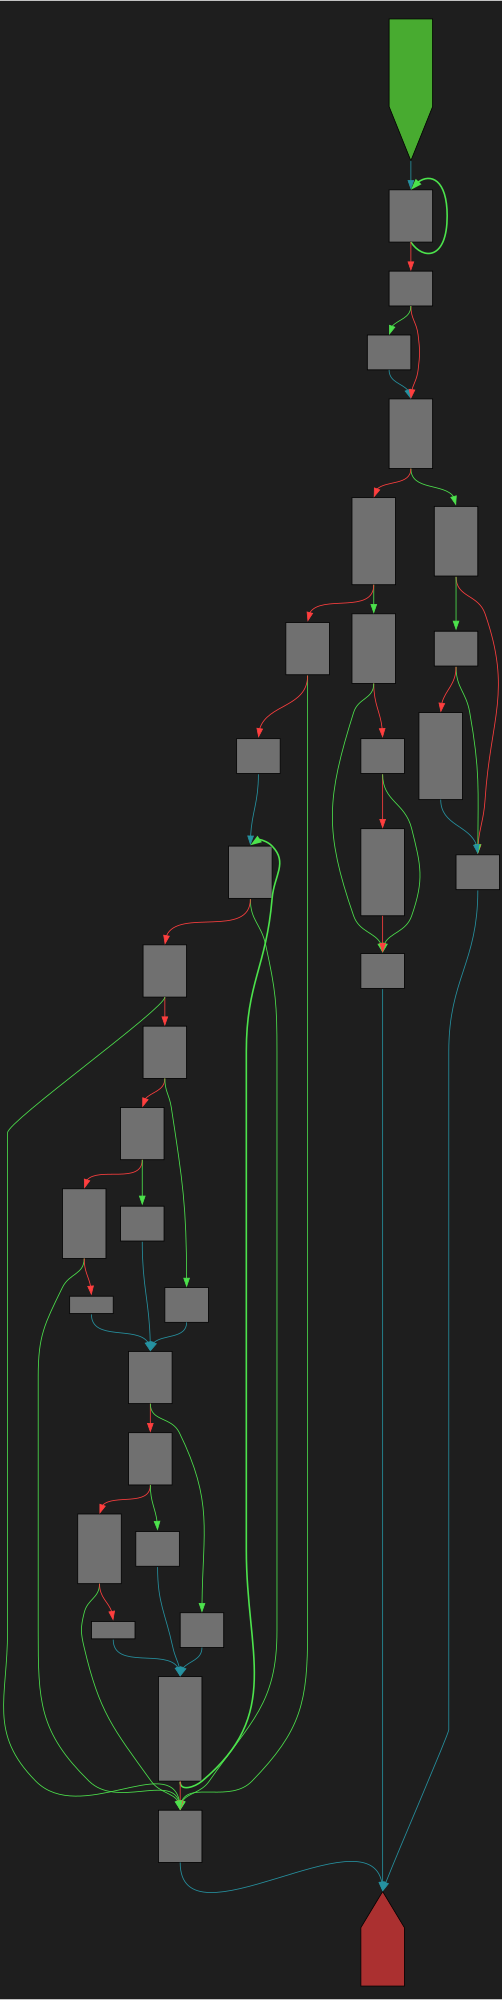
CFG Bot 🤖
cfgbot@mastodon.socialProject: mpengine-x64-pdb 1.1.24090.11
File: mpengine.dll
Address: 75a1ff7cc
GetTrackingContextFromBase64String
SVG:
dark https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fmpengine-x64-pdb%2F75a1ff7cc.json&colors=dark
light https://tmr232.github.io/function-graph-overview/render/?graph=https%3A%2F%2Fraw.githubusercontent.com%2Fv-p-b%2Fghidra-function-graph-datasets%2Frefs%2Fheads%2Fmain%2F%2Fmpengine-x64-pdb%2F75a1ff7cc.json&colors=light
 0
1
0