Posts
4665Following
742Followers
1662
 repeated
Zalka Csenge Virág, PhD
TarkabarkaHolgy@ohai.social
Today is the Day of the Hungarian Folktale. So your quest, should you choose to accept it, is to go find a Hungarian folktale a read it / listen to it.
😊
 2
1
 1
buherator
buheratorhttps://idov31.github.io/posts/paint-it-blue-reverse-win32k
0
0
2
repeated
qualia
qualia@floofy.techfucked up that computers don't look like this anymore. tell me you wouldn't live here if you were a one or a zero

 3
7
0
buherator
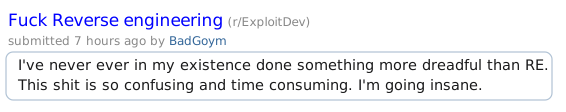
buheratorhttps://github.com/v-p-b/dreadful-reversing/blob/main/fuck-reverse-engineering.svg
Go nuts!
 0
0
0
buherator
buheratorShow content
Then I got recommended hate5six on the sidebar so Escuela Grind it is:
https://www.youtube.com/watch?v=jXaUUvOEQ7E
0
1
1
repeated
Kevin Beaumont
GossiTheDog@cyberplace.socialThe Dutch government has shut down all Citrix Netscalers and is asking every gov org to perform incident response
HT @bert_hubert
https://berthub.eu/tkconv/document.html?nummer=2026D47262
1
5
0
repeated
Catalin Cimpanu
campuscodi@mastodon.socialKiteworks patches the vulnerability law enforcement warned it about last week and revokes its "take server offline" recommendation
https://www.kiteworks.com/company/press-releases/kiteworks-restores-systems-credible-threat/
1
1
0
repeated
 repeated
buherator
buheratorhttps://ptswarm.com/blog/cve-2026-43783-repair-permissions-get-root-lpe-via-desktopserviceshelper-in-macos-26-5/
0
0
0
buherator
buheratorhttps://alonsovidales.github.io/protonmail-sender-spoofing/
0
0
1
buherator
buheratorLater we agreed in mutual disarmament with my toy soldiers.
0
1
4
repeated
Peter Lowe
pgl@infosec.exchangeI made a thing: it's called the DNS Museum, and it's because I kept joking at the start of my talk, "Bizarre and Unusual Uses of DNS" that a lot of the things weren't alive anymore - so it was more like a museum of DNS and I was the curator. Anyway, I'm on holiday right now so I finally got around to doing something about that joke.
Consider this a first draft, I have way more notes about other things to add at some point. It's also a little bland, but one thing I'm not is a designer. Let me know about any issues - AI was used to help create the site, but of course I'm responsible for any mistakes. It's on GitHub too, so PRs are welcome.
18
11
0
repeated
mahaloz
mahaloz@infosec.exchangeSome brief thoughts on AI in hacking and optimizing for speed:
https://mahaloz.re/2026/09/28/hack-race.html
A bit is also a response to Flare-On 13.
0
1
0
repeated
RE//verse Conference
REverseConf@infosec.exchangeRE//verse 2027 is on the way, and you should probably be there! If you know, you know. If you don’t, this is a very good year to fix that. https://re-verse.io/
 0
1
0
repeated
blacktop
blacktop@mastodon.socialHigh level diff of iOS 27.0 vs. iOS 27.0.1 🎉
https://github.com/blacktop/ipsw-diffs/blob/main/27_0_24A437_vs_27_0_1_24A446/README.md
0
1
0
repeated
Daphne Preston-Kendal
dpk@swhack.com
We trust you have received the usual lecture from the local System Administrator.
pagliacci.jpg
0
7
1
 repeated
robinhouston
robinhouston@mathstodon.xyzFor my birthday, my brother-in-law gave me a 4992-digit hex number that, when used as a seed for Python’s random number generator, makes it so that printing a sequence of “random” ASCII characters actually prints a birthday greeting.
I find it rather amazing that this is possible!
This is the program he sent with the seed:
with open("seed.txt", encoding="ascii") as handle:
seed = int(handle.read().strip(), 0)
r = random.Random(seed)
pending = ""
while True:
character = chr(r.randrange(128))
if pending + character == "\x1e\x1f":
break
print(pending, end="")
pending = character
print()
2
10
0
repeated
watchTowr
watchTowr@infosec.exchangeCVE-2026-88771 - the loaded Citrix footgun went off again, and the screaming noise is back in our ear.
You knew it was coming - enjoy the latest watchTowr Labs blogpost.
1
10
0