Posts
4621Following
742Followers
1659
 repeated

frycos
frycos@infosec.exchange
Happy announcement: My colleague and me will present a talk at hardwear.io NL 2026, "Vulnerabilities That Get Under Your Skin: Targeting the World’s Best-Selling Infusion Pumps". 100% human-brain VR 😛
 1
3
 1
repeated
Nαtαshα 
Natasha_Jay@tech.lgbt
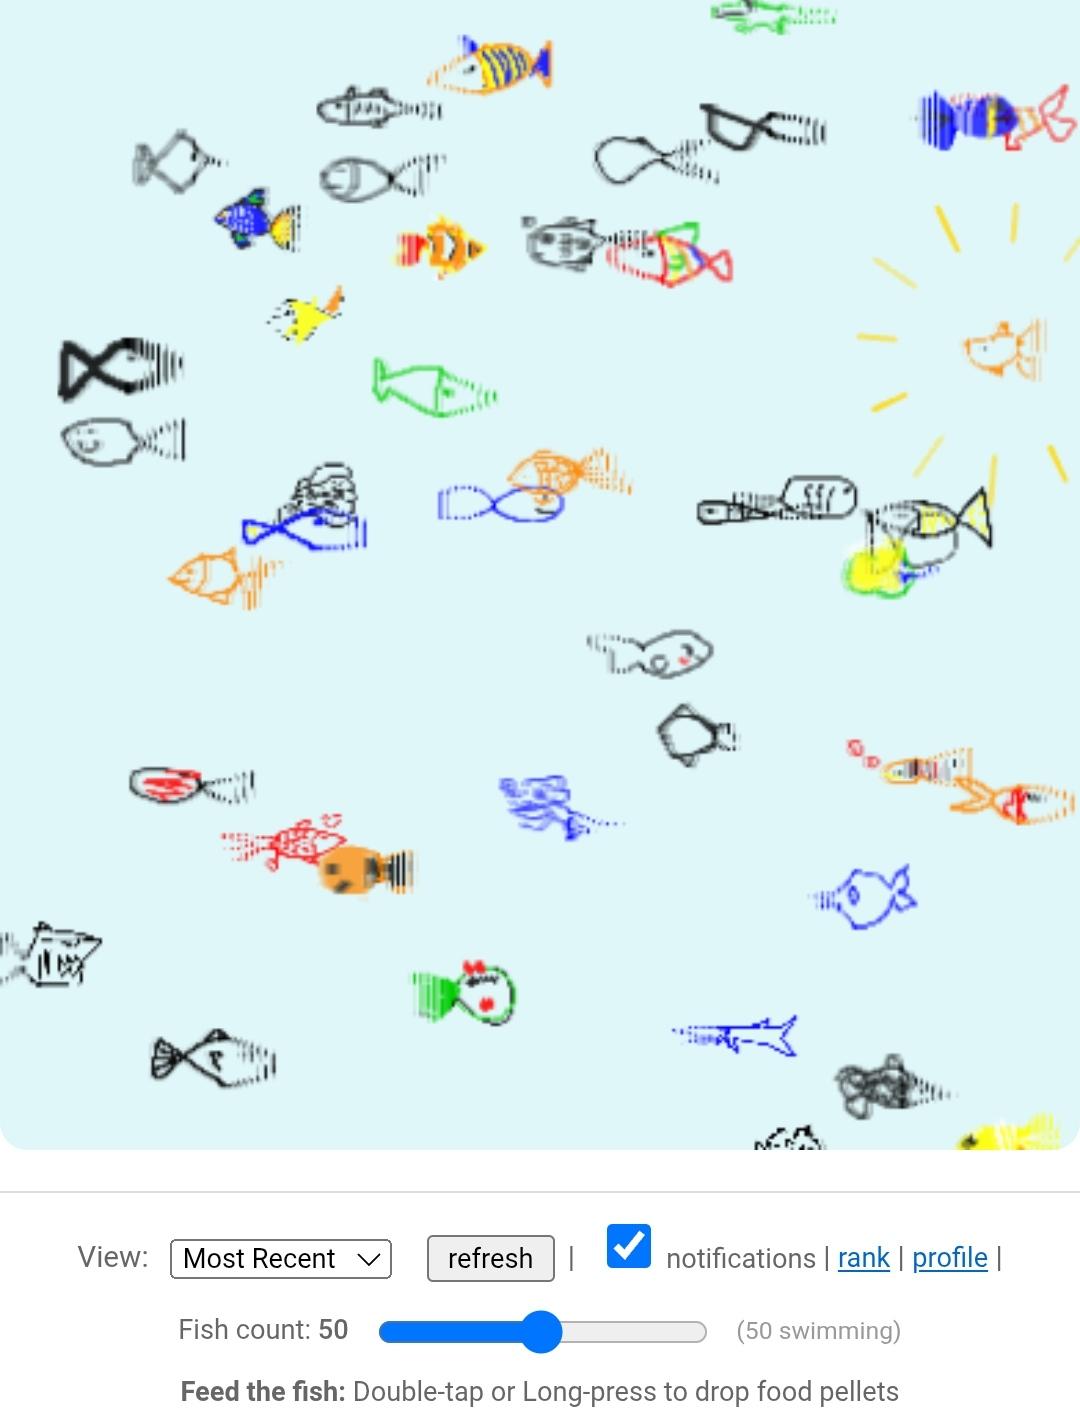
Draw a fish and watch it swim in a tank with everyone else who's drawing them too 🐠🐟🐡
Silly, but also lovely
 2
6
0
buherator
buherator
1
0
0
repeated
hrbrmstr 🇺🇦 🇬🇱 🇨🇦🇧🇪
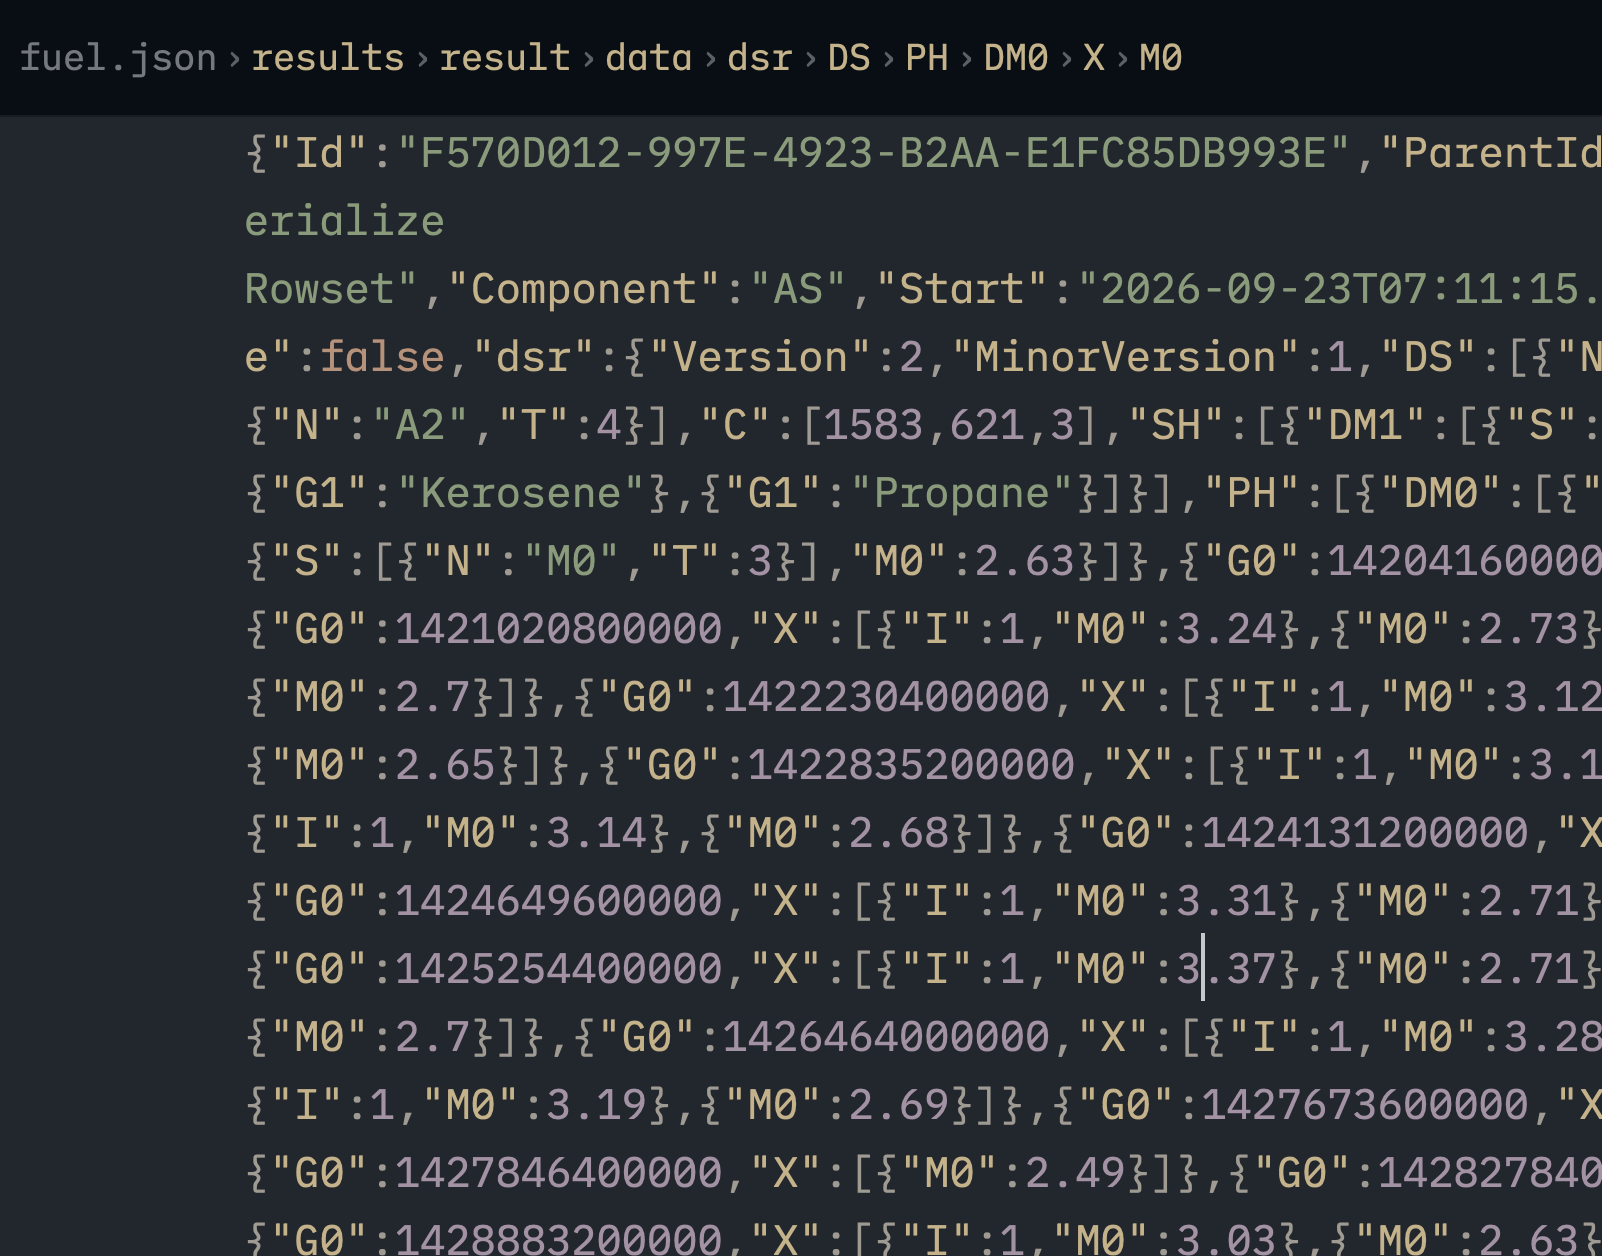
hrbrmstr@mastodon.socialTIL a recent? Zed update shows you the JSON path to the item you have the cursor at.
 0
3
0
repeated
Julia Evans
b0rk@jvns.capoll: in Git, do you ever use any of the references `MERGE_HEAD`, `REBASE_HEAD`, `CHERRY_PICK_HEAD`, `ORIG_HEAD`, `FETCH_HEAD`, or `REVERT_HEAD` etc? (and if so, what do you use them for?)
7
3
0
repeated

Ivan Ožić Bebek
obivan@infosec.exchangeSharePoint CVE-2026-65660: From Anonymous Access to Pre-Auth RCE via EditingPageParser Type-Check Bypass https://blog.viettelcybersecurity.com/sharepoint_cve-2026-65660/
0
3
0
repeated

 repeated
buherator
buheratorhttps://www.elttam.com/blog/att-cking-tacacs-to-pwn-your-network-via-a-pre-auth-rce
2
4
6
repeated
Julia Evans
b0rk@jvns.caperiodic reminder that Wizard Zines has an educational use policy if you want to use them in your university courses! https://wizardzines.com/education/
0
2
0
repeated
RE: https://infosec.exchange/@cR0w/117315299719177302
Important: We have learned that this vulnerability has been exploited.
0
4
0
repeated
Catalin Cimpanu
campuscodi@mastodon.socialPoland's CERT has published its report on MikroTrik, the zero-day campaign that targeted MikroTik routers earlier this month
Praises LLM agents for helping with the research
https://cert.pl/en/posts/2026/09/mikrotrick-technical-analysis/
0
4
0
buherator
buherator
2
0
1
repeated
It's so good to see this in the MIT Tech Review. Let's hope the message gets through. 🤞Big props to @timnitGebru & @emilymbender for putting such a fine point on things!
"Instead of OpenAI being prosecuted for creating malware that hacked another company, press releases, news outlets, media personalities, and lawmakers refer to “rogue models” as if they acted on their own. Instead of researchers being questioned about their companies’ habit of plagiarizing academics’ work or using customer data to train models without consent, the public’s imagination is redirected to fears about what the future might hold upon the arrival of fictional superintelligent machines."
https://www.technologyreview.com/2026/09/22/1144867/dont-be-fooled-summer-ai-hype/
2
8
0