Posts
4641Following
742Followers
1661

 repeated
Tim (Wadhwa-)Brown 
timb_machine@infosec.exchange
 0
4
 0
repeated
eShard
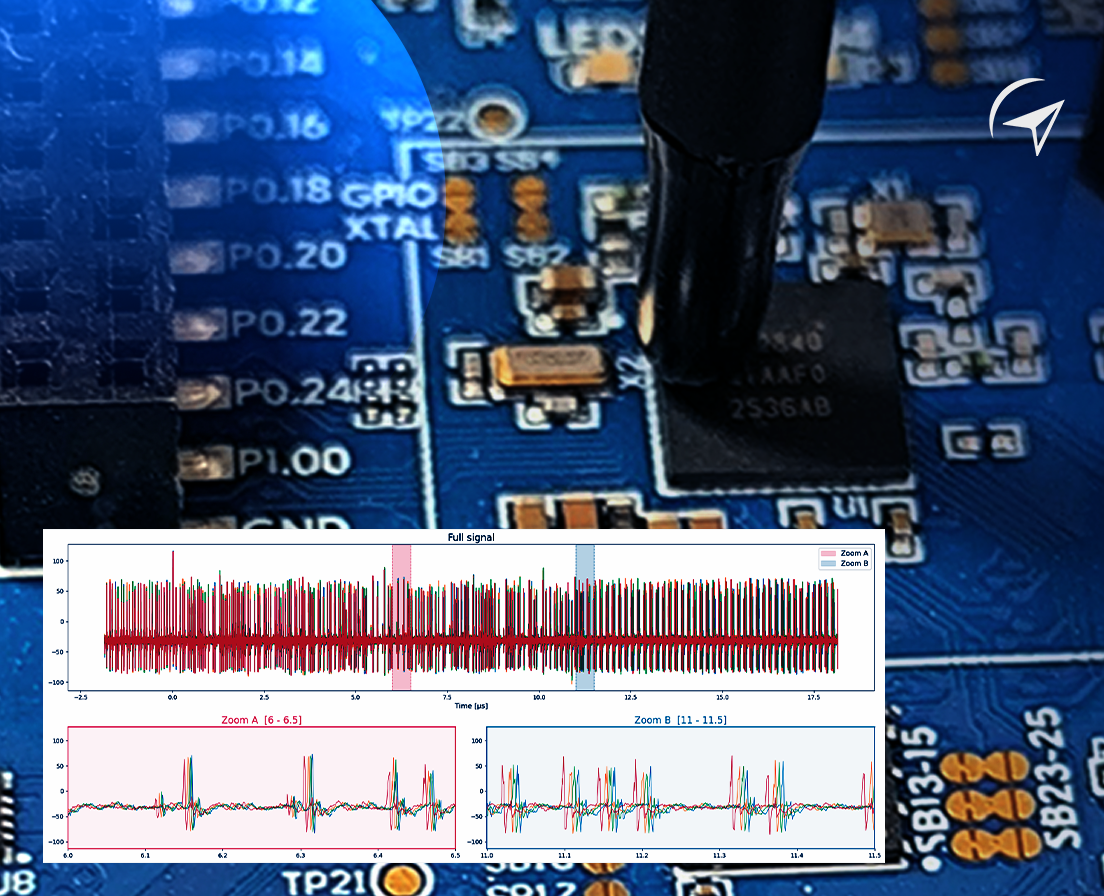
eshard@infosec.exchangeA first public side-channel attack on the Arm CryptoCell-310.
Our latest blog post walks through the full methodology: EM signal analysis, a collision-correlation attack, and full AES key recovery.
Read it here: https://www.eshard.com/blog/side-channel-analysis-arm-cryptocell-310-aes
#SCA #HARdware #CYBERsecurity #ARM #ARM64 #SCA
 0
4
0
repeated
Gynvael Coldwind 🐈
gynvael@infosec.exchange[Commercial, since it involved my company] Two of my friends - Jarosław Jedynak and Michał Leszczyński - are doing a webinar on Kubernetes hacking tomorrow, with live demos and stuff. It's free, but you do have to sign up to hackArcana's newsletter:
https://hackarcana.com/workshop-session/2026-Q4-k8s/intro-webinar
0
2
0
buherator
buheratorBased on the observation that behind every warning sign there is a story I suspect that at one point a TTD trace somehow resulted in summoning MS's legal team :)
[1] https://learn.microsoft.com/en-us/windows-hardware/drivers/debuggercmds/time-travel-debugging-overview
[2] https://learn.microsoft.com/en-us/windows/win32/dxtecharts/crash-dump-analysis
0
0
0
repeated
CHERI Alliance
cheri_alliance@infosec.exchange📢 Registration for CHERITech'26 is now open!
Join us on 12-13 November 2026 alongside SEMI Europe's SEMICON Europa 2026 at the NextSEMI Arena (Hall B0), Messe München, Germany for two days of talks, technical discussions, and networking focused on CHERI, memory safety, and secure computing.
How to register:
1️⃣ Purchase a valid SEMICON Europa 2026 ticket
2️⃣ Complete the CHERITech'26 registration form
Please note: CHERITech'26 is free to attend for all SEMICON Europa 2026 visitors. However, a valid SEMICON Europa 2026 ticket is required for each day you wish to attend CHERITech'26.
🔗 Register and learn more: https://cheri-alliance.org/events/cheritech26/
0
4
0
buherator
buheratorhttps://projectzero.google/2026/09/windows-dangling-com.html
0
1
1
buherator
buheratorhttps://www.ibm.com/support/pages/node/7285846
The 90s called and want their dumb obfuscation back!
0
2
9
buherator
buherator
0
0
2
buherator
buheratorhttps://x41-dsec.de/lab/advisories/x41-2026-004-debian-live-boot/
0
1
2
buherator
buheratorhttps://minanagehsalalma.github.io/zte-smartlife-app-pwned/
0
0
0
repeated
blacktop
blacktop@mastodon.socialHigh level diff of iOS 27.2 beta vs. iOS 27.2 beta2 🎉
https://github.com/blacktop/ipsw-diffs/tree/main/27_2_24B5084k_vs_27_2_24B5089g/README.md
0
1
0
repeated
LittleAlex 🇺🇦🇮🇱🇩🇪🇳🇴
littlealex@infosec.exchangeHow Much Data Does an Idle Android Phone Send to Google? (72-Hour Packet Benchmark)
#android #google #surveillance
https://www.praveentechworld.com/research/degoogle-telemetry-2026
0
3
0
repeated
Allele Security Intelligence
alleleintel@infosec.exchangeAfter 6 successful runs of our Introduction to Linux Kernel Exploitation training—across both public and in-company cohorts—and a 100% positive rating from our students, we are offering it for the first time in English!
This is your opportunity to gain hands-on experience with computer architecture, kernel debugging, the Linux kernel, exploit development, and modern mitigation bypasses alongside an instructor doing top-tier vulnerability research.
Here are a few testimonials from our former students:
"I've always wanted to master the Linux kernel, and this course by Anderson and the Allele Security Intelligence team was the perfect opportunity. It expanded my architecture knowledge, sparked my interest in binary exploitation, and completely exceeded my expectations!"
"An exceptional course on computer architecture and the Linux kernel. The clear structure made complex concepts intuitive, and the practical exercises were game-changing for learning how to identify and exploit kernel vulnerabilities."
What sets our training apart:
Direct support: Personalized contact and guidance starting as soon as you enroll.
Cutting-edge content: Up-to-date curriculum drawn from public sources and our own internal security research.
Expert instruction: Taught by an instructor with over 10 years of world-class vulnerability research experience.
Flexible learning: Class recordings uploaded within 24 hours so you never miss a lesson.
Structured & Accessible: Detailed, beginner-friendly documentation that makes complex concepts easy to follow.
Registration is open! We have a Super Early Bird discount available for the first 4 students.
We also offer corporate group packages. If you have any questions or need assistance with the enrollment process, please let us know—we’re happy to help!
Check out the link below for more details and to enroll:
Introduction to Linux Kernel Exploitation – September 2027
https://allelesecurity.com/introduction-to-linux-kernel-exploitation-september-2027/
0
2
0
repeated
Was going to write a couple of posts here about my weekend experiment but decided to make it a bit more permanent so it can be tested by time. If not, just a bit of random (silly) writing practice before those skills are lost forever.
https://reverse.put.as/linesignal/
1
2
0
repeated
Underrated YouTube channel of the century: Dude building an 8088 PC on a breadboard, then continuing with a Compaq Deskpro 386 inspired design.
https://www.youtube.com/watch?v=tY3eqQ-OKBU&list=PL0HI91x0gPoGUtu3rUd1dSInTlIL2wk2p
https://www.youtube.com/watch?v=K2-RwBgsrFM&list=PL0HI91x0gPoE9sSNmIbq5fcDDc7ziQe3c
https://www.youtube.com/watch?v=AFwNuTyhbgM&list=PL0HI91x0gPoGCINU_xEbs1fEjoHymO5l0
1
1
1
repeated
Trail of Bits
trailofbits@infosec.exchangeSAML was created in 2002 by merging four rival XML security protocols into one spec. That design still generates vulnerabilities: a canonicalization flaw via XML comments in 2018, XML round-trip bugs in Go's stdlib in 2020, a GitHub Enterprise SAML auth bypass in 2025, and more.
Matt Schwager breaks down 5 design flaws behind the pattern and makes the case for moving to OIDC.
https://blog.trailofbits.com/2026/09/21/saml-a-fractal-of-bad-design/
1
2
0