Posts
4645Following
742Followers
1662
 repeated
Trail of Bits
trailofbits@infosec.exchange
SAML was created in 2002 by merging four rival XML security protocols into one spec. That design still generates vulnerabilities: a canonicalization flaw via XML comments in 2018, XML round-trip bugs in Go's stdlib in 2020, a GitHub Enterprise SAML auth bypass in 2025, and more.
Matt Schwager breaks down 5 design flaws behind the pattern and makes the case for moving to OIDC.
https://blog.trailofbits.com/2026/09/21/saml-a-fractal-of-bad-design/
 1
2
 0
repeated
David Chisnall (*Now with 50% more sarcasm!*)
david_chisnall@infosec.exchangeWhen I was at Microsoft, I worked quite closely with some teams at MSRC. They had a lot of concerns like this (relevant to me, memory-safety bugs had been close to 70% of critical vulnerabilities for over a decade, relevant to everyone the absolute number of vulnerabilities had been steadily climbing for 20+ years).
On the 'Decrease the birth rate' axis, I found one piece of framing useful. They differentiated between 'durable' and 'non-durable' mitigations. Durable mitigations render a class of vulnerability non-exploitable. For example, if a short-lived program runs with free turned into a no-op, temporal safety bugs are now non-exploitable. It's not a universally applicable mitigation but it's an easily deployed durable mitigation. In contrast, non-durable defences block specific techniques for exploiting vulnerabilities but don't prevent the vulnerabilities. New exploit techniques eventually bypass non-durable mitigations.
There's a lot of hesitation to deploy non-durable mitigations because they're almost impossible to remove. Even if exploit toolkits come with an automated step to bypass the mitigation, no one wants to be responsible for some large-scale compromise that doesn't include the mitigation bypass and being told that it would have been prevented if the mitigation had remained enabled.
I found this framing useful for reasoning about a lot of things in this space. LLM-based vulnerability discovery remains a non-durable mitigation because it allows closing vulnerabilities but not classes of vulnerability, and it's probabilistic and doesn't find all vulnerabilities of a class. So it motivates attackers to use vulnerability-discovery techniques that find ones LLMs miss.
0
1
0
repeated
Eloy. @ pmOS and Alpine Linux conference
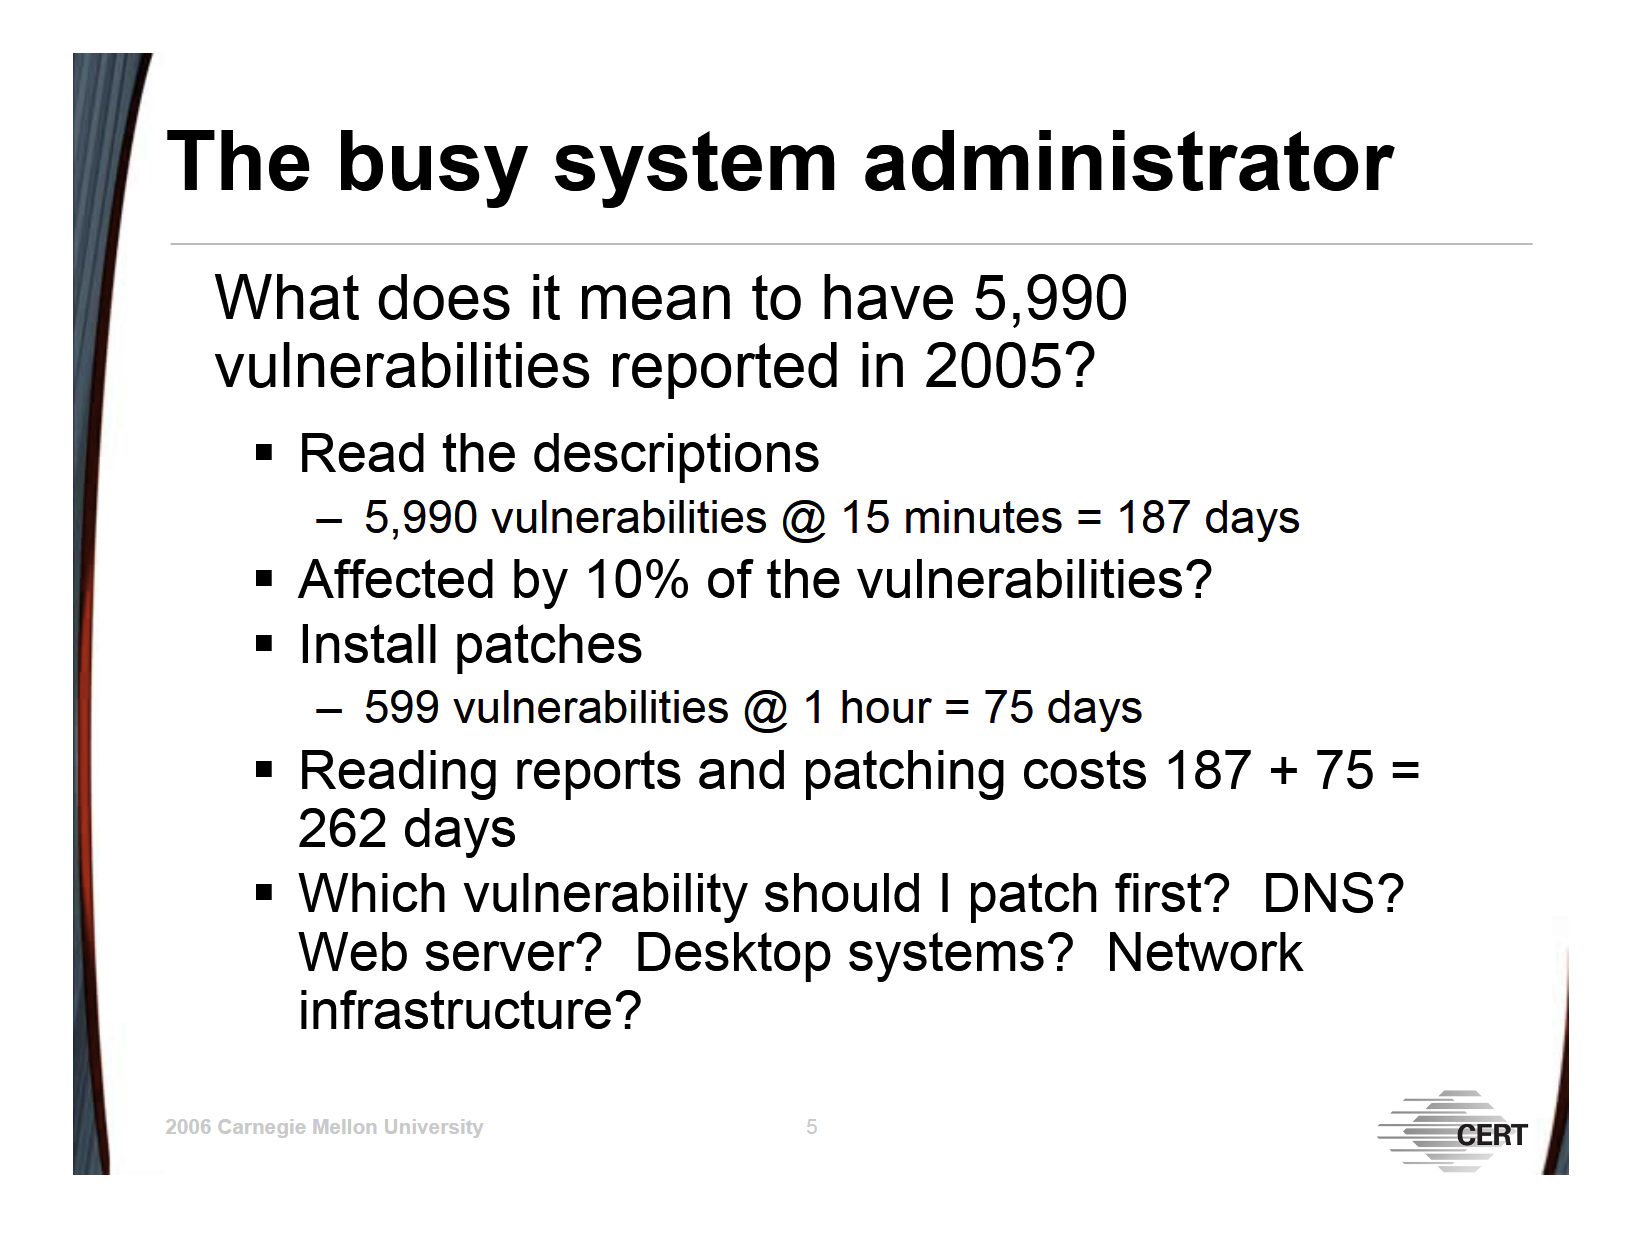
eloy@hsnl.socialpeople talk a lot about the "vulnpocalypse" this year, a supposedly new trend where there are too many CVEs to patch.
Here is a presentation slide by the Carnegie Mellon CERT Coordination Center from 2006. Two decades ago!
https://web.archive.org/web/20070714104234/http://www.cert.org/archive/pdf/CERTCC-DSS_Tool.ppt.pdf
 2
3
0
buherator
buheratorhttps://fs.blog/brain-food/september-20-2026/
1
4
5
buherator
buherator
1
0
1
repeated
hackaday
hackaday@hackaday.socialThe Sinclair Spectrum Gets A Desktop GUI
https://hackaday.com/2026/09/21/the-sinclair-spectrum-gets-a-desktop-gui/
1
2
0
repeated
Frédéric Jacobs
fj@mastodon.socialCongrats to Steve Weis at Anthropic for factoring RSA-896 in 10 days adapting CADO-NFS to run on a max of 2048 GPUs.
No algorithmic breakthrough, just code optimized for recent parallel compute architectures.
“it does demonstrates that RSA-1024 keys are vulnerable to many actors with data center-level fleets of GPUs.”
https://saweis.net/posts/rsa-896.html
1
4
0
repeated

 repeated
buherator
buheratorhttps://heif-heist.com/
Cool finding, but these issues have been around for ages. It's embarrassing for all the affected large corps that they didn't care to invest in testing their dependencies and proper sandboxing.
0
3
8
buherator
buheratorhttps://threadreaderapp.com/thread/2101252692635004997.html
0
1
3
repeated
Disconnect3d
disconnect3d@infosec.exchangeNew Pwndbg release!
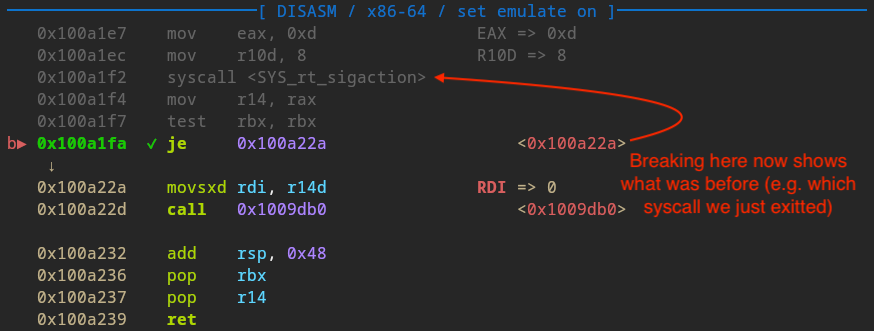
We now disassemble code backwards in context and nearpc, display indirect jumps, nearpc -f works without debug syms, added stack-vis command to visualize stack frames, improved v2p, p2w and pageinfo kernel debugging commands & more!
See https://github.com/pwndbg/pwndbg/releases/tag/2026.09.15
Please sponsor us: https://github.com/sponsors/pwndbg !
#pwndbg #gdb #lldb #reverseengineering #security #lowlevel #exploitation #pwning
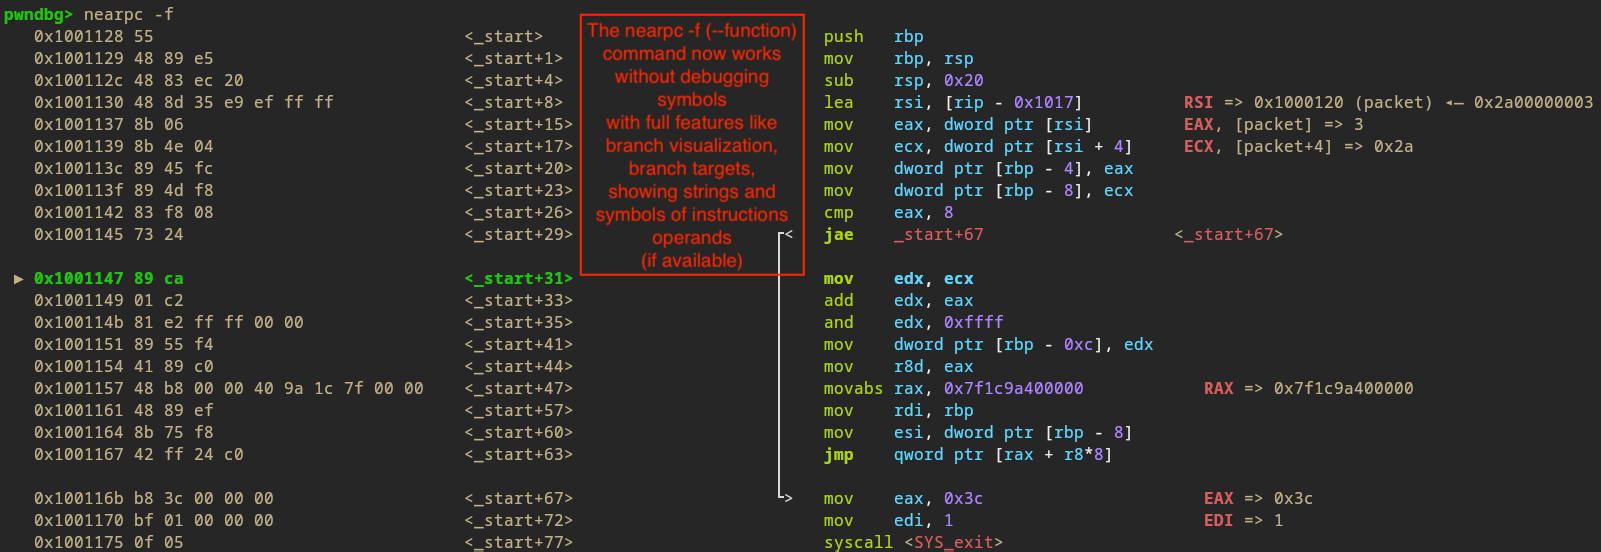
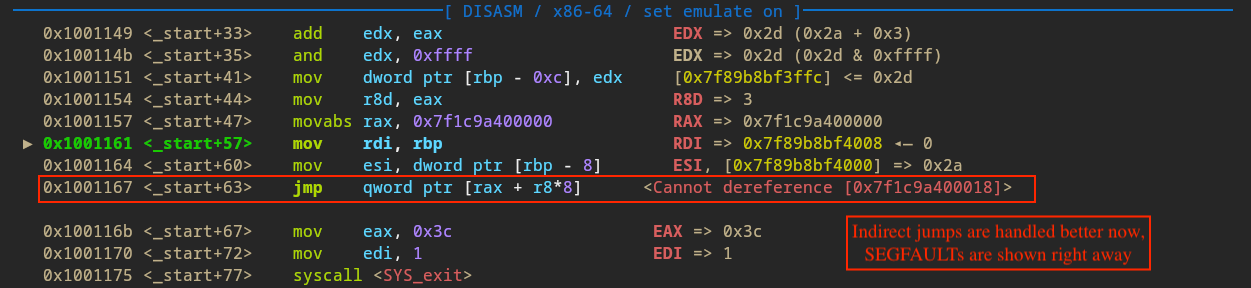
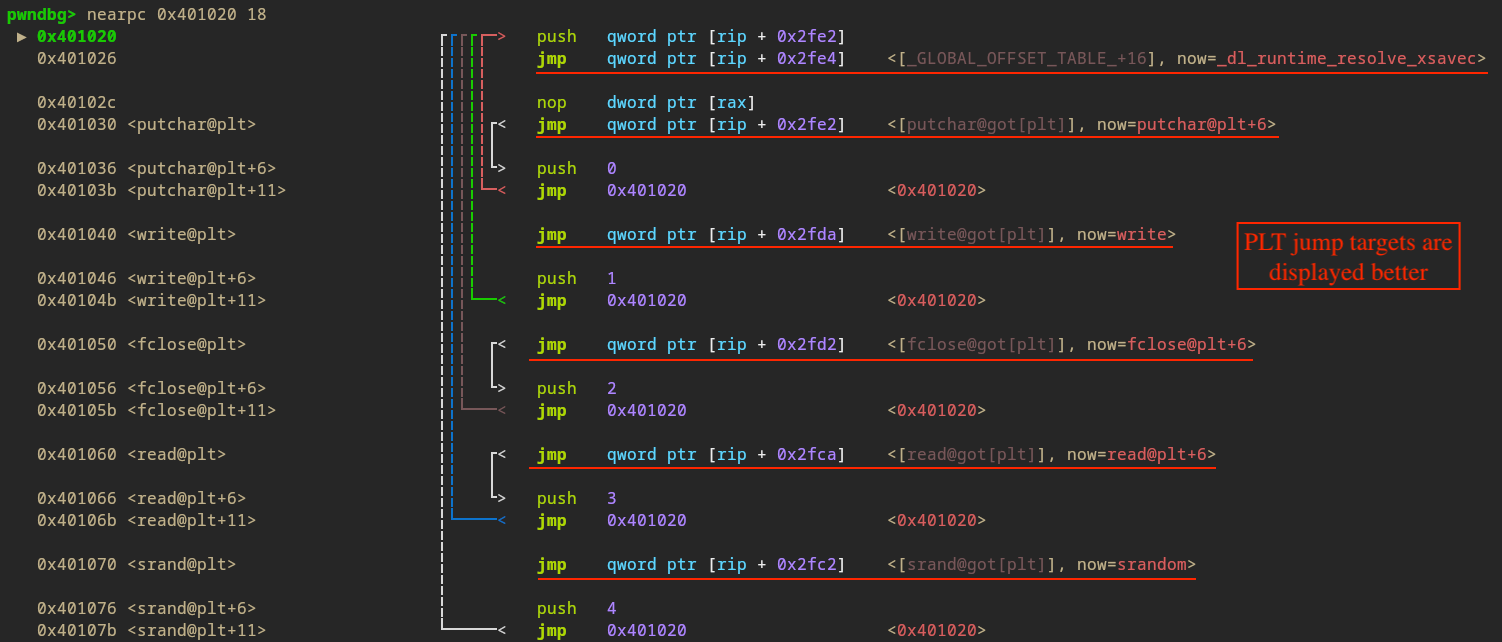 1
4
0
repeated
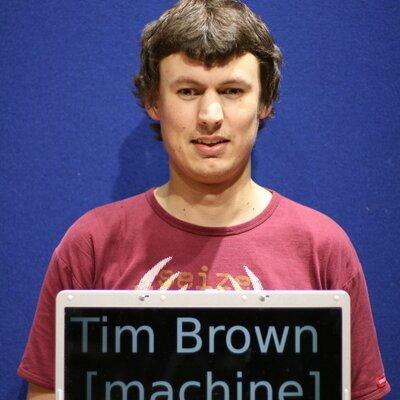
Tim (Wadhwa-)Brown 
timb_machine@infosec.exchange
Are "HACK THE PLANET" t-shirts responsible for multi-modal prompt injection into the agents at world leading AI labs?
2
1
0
repeated
raspberry_pi@bird.makeup
raspberry_pi@bird.makeupLasers. Microscopes. $250K. One secured chip.
Ledger Donjon just showed how they cracked debug access on RP2350-A4, a break worthy of Raspberry Pi's own Hacking Challenge.
Respin or no respin? Raspberry Pi says no. Read why: https://www.raspberrypi.com/news/everything-is-better-with-lasers/
0
2
0
repeated
Emeritus Prof. Christopher May
ChrisMayLA6@mastodon.me.ukI love a cartoon that sums up a line of argument I have often made as a political economist, so here's a great example from the (recently deceased) P.C.Vey - whose work appeared in the New Yorker & elsewhere.
#economics #regulation #politics
h/t Loren Fox/LinkedIn
 1
10
0
repeated
Ivan Ožić Bebek
obivan@infosec.exchangeWindows Defender Update DoS Vulnerability https://github.com/MSNightmare/BigDiskBuster
0
1
0
repeated
Mx. Luna Corbden 🪿🐸
corbden@defcon.socialMy son is reading Lord of the Rings for the first time and he just stuck his head out the door:
"Who the fuck is Tom Bombadil??"
6
10
1
buherator
buheratorhttps://debugagent.com/what-go-taught-us-about-java-garbage-collection
0
0
0