Posts
4544Following
741Followers
1654
 repeated

🦜 Pivot To AI
pivot-to-ai.com@rss-parrot.net
Microsoft Vibe Gaming: an AI to play your games for you
pivot-to-ai.com/2026/09/09/microsoft-vibe-gaming-an-ai-to-play-your-games-for-you
Microsoft isn’t just the company that bought all the game studios so it could run them into the ground — Microsoft Research is hard at work exploring new realms in how to make gaming suck. Welcome to Project Vega! The blog headline is literally: “Vibe…
 0
1
 0
repeated
hanno
hanno@mastodon.socialFollowerpower: there are a bunch of online + offline tools to turn PDFs with only images into searchable PDFs.
Anyone who has tried plenty of them and can give suggestions which one (requirement would be: either online tool or available on linux) gives best results?
1
1
0
repeated
Lukasz Olejnik
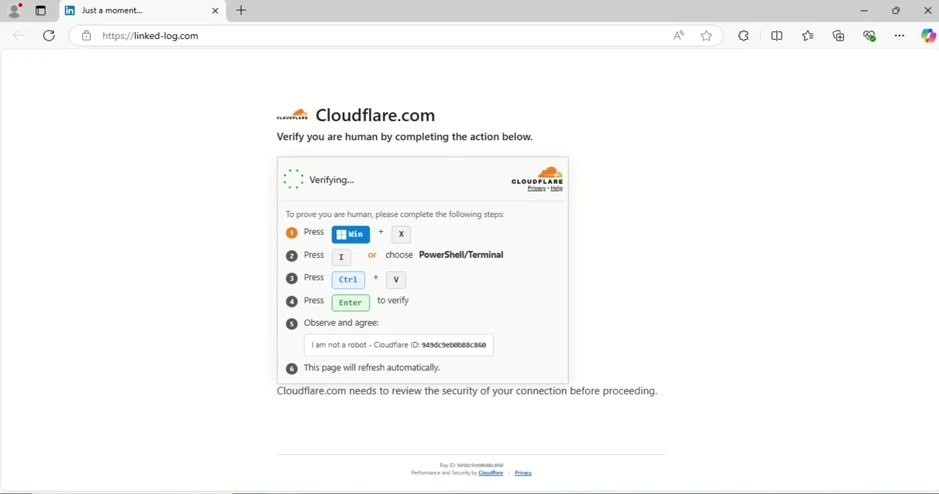
LukaszOlejnik@mastodon.socialBerlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
 6
4
0
repeated

Will Dormann
wdormann@infosec.exchangeAnthropic notices another felony that they committed. They noticed this one by not using AI to look for it.
https://www.theregister.com/ai-and-ml/2026/09/10/anthropic-reveals-fourth-likely-crime-committed-by-its-ai/5295412
1
4
0
repeated

SSD Secure Disclosure
SSDSecureDisclosure@infosec.exchange🚨 New advisory was just published!
A heap buffer overflow in a Windows DCOM service can be leveraged to escalate privileges from a Medium IL standard user to SYSTEM IL, an issue that occurs when attacker-controlled Power Setting data and length are passed to the PSM callback.
This vulnerability earned 3rd place in the Windows LPE category at TyphoonPWN 2026. Read all the details at: https://ssd-disclosure.com/dcom-service-psmserviceexthost-lpe/
0
2
0
repeated
 repeated

James Kettle
albinowax@infosec.exchangeTwo hours till my HTTP Terminator talk kicks off at SEC-T! You can catch the livestream at 9:15 UTC:
https://www.youtube.com/watch?v=S6R7cBZDdK4
0
3
0
buherator
buheratorhttps://github.com/v-p-b/mdsrv
Static webserver that renders #Markdown files and #MermaidJS diagrams for your viewing pleasure. With live updates!
#python #llm
0
2
4
repeated

David Chisnall (*Now with 50% more sarcasm!*)
david_chisnall@infosec.exchange@zzt Most feature phones are hard to compromise because every time a malware author learns something about how they work, their brains explode.
0
2
0
repeated

 repeated

Hackaday
hackaday@robot.villasReverse Engineering The Philips PM5139
https://hackaday.com/2026/09/09/reverse-engineering-the-philips-pm5139/
0
2
0
repeated
CISA KEV Tracker
cisakevtracker@mastodon.socialCVE ID: CVE-2026-20079
Vendor: Cisco
Product: Secure Firewall Management Center (FMC) and Security Cloud Control (SCC) Firewall Management
Date Added: 2026-09-09
CVE URL: https://nvd.nist.gov/vuln/detail/CVE-2026-20079
0
1
0
repeated
CISA KEV Tracker
cisakevtracker@mastodon.socialCVE ID: CVE-2026-87491
Vendor: Google
Product: Chromium V8
Date Added: 2026-09-09
CVE URL: https://nvd.nist.gov/vuln/detail/CVE-2026-87491
0
1
0
repeated
blacktop
blacktop@mastodon.socialHigh level diff of iOS 27 beta8 vs. iOS 27 RC 🎉
https://github.com/blacktop/ipsw-diffs/tree/main/27_0_24A5430a_vs_27_0_24A435/README.md
0
1
0
 repeated

Volexity 
volexity@infosec.exchange
Earlier this month, @volexity detected multiple Chinese threat actors launching attacks against its customers using chained 0-day exploits in Google Chrome (CVE-2026-85046 & CVE-2026-87491) and Microsoft Windows (CVE-2026-85880). Volexity observed threat actors it tracks as UTA0560 and JungleBamboo using variations of the same exploits to deliver different malware implants. These implants ranged from a JScript backdoor (GRIMWEDGE) to a fake Google Gemini Chrome extension (LONGTALE).
Read the full analysis of the exploit chain and post-exploitation tradecraft here: https://www.volexity.com/blog/2026/09/09/mind-the-patch-gap-multiple-chinese-threat-actors-chain-0-day-exploits-in-chrome-windows/
#DFIR #threatintel
 0
2
0
buherator
buheratorHeat.
Heat.
[Music]
1-2-3
0
0
1